The Pentest Management OS for Modern Offsec Teams

Run testing, reporting, remediation and client delivery from one platform.

  • SOC2 Certified
  • Cloud SaaS or On-Prem
  • Integrated Scanning ASM & DAST

Trusted By World Leading Cybersecurity Companies. 6.000+ Organizations Protected.

Time saved per project

%

Time Spent on Reporting

Reports Generated last 12 month

Improve Operational Efficiency: 1-2h to Finalize Pentest Reports

Use Cases

Built for every role. Ready for every use case.

Connect security teams, pentest providers, and engineers across pentesting, red teaming, and continuous exposure validation.

Service Provider
Internal Pentest Team

Pentest Reporting

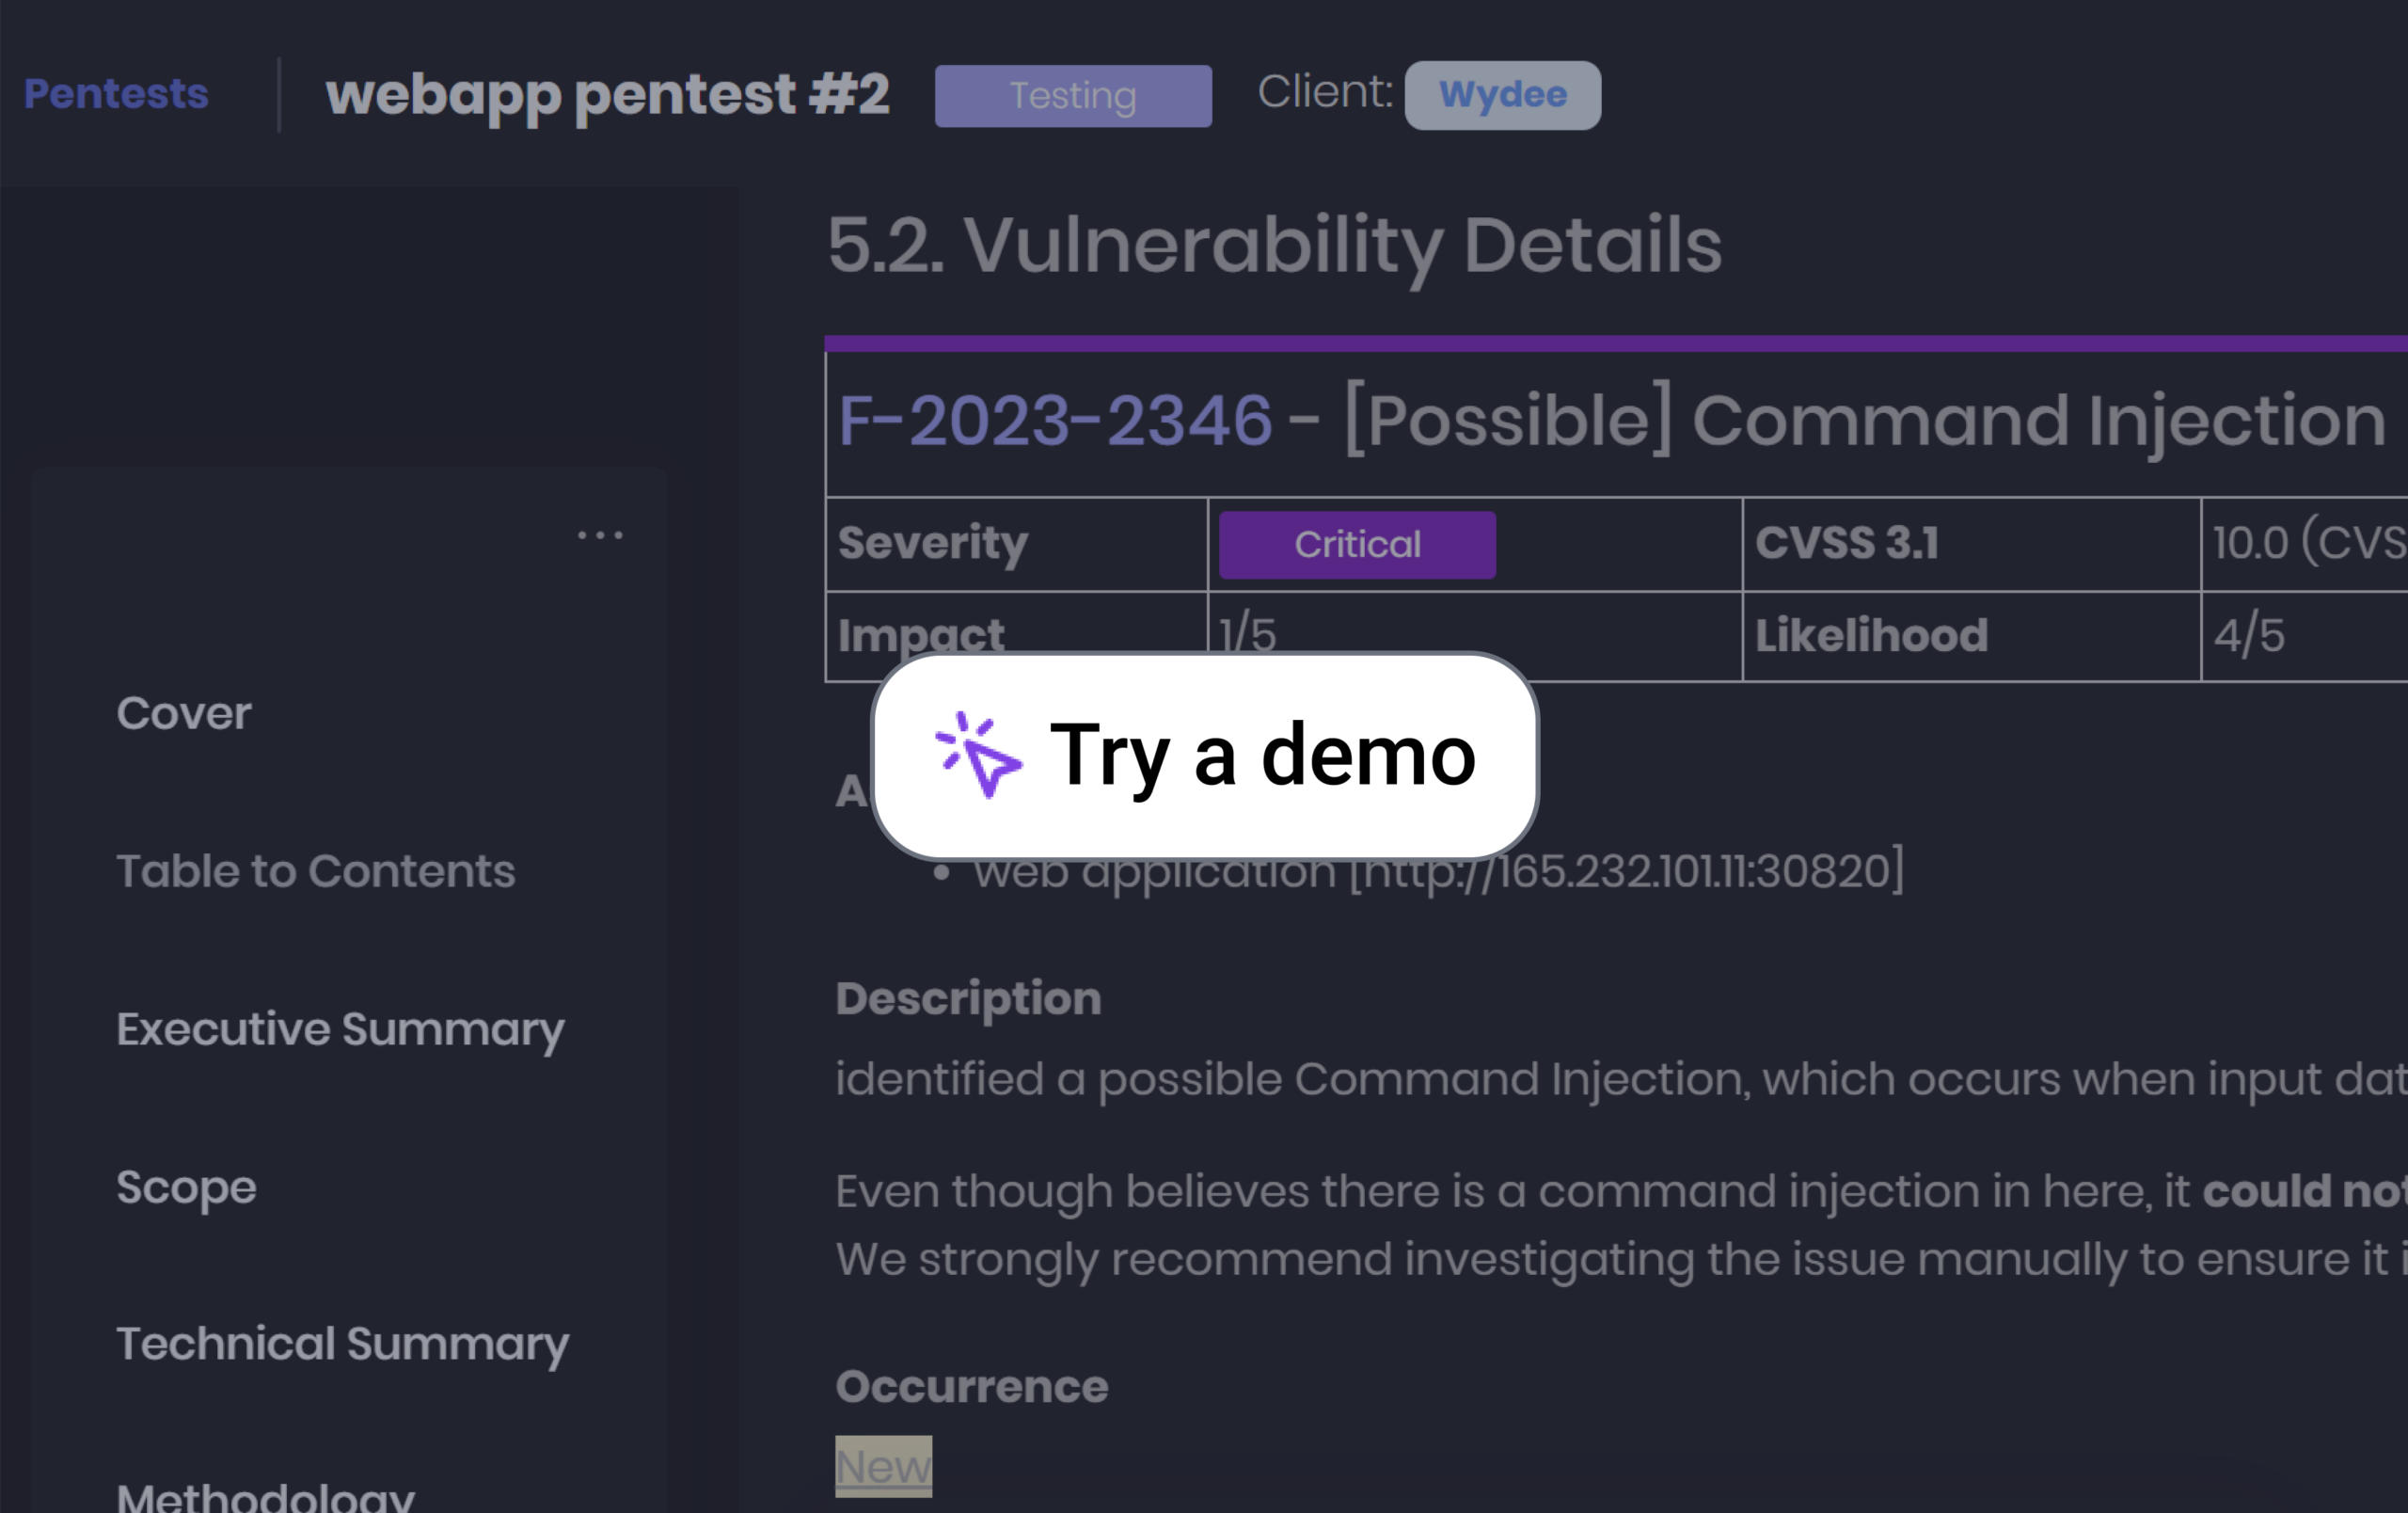
Standardize and Scale Pentest Reporting. From tool output to structured, consistent reports, delivered professionally to every client.
Red Teaming

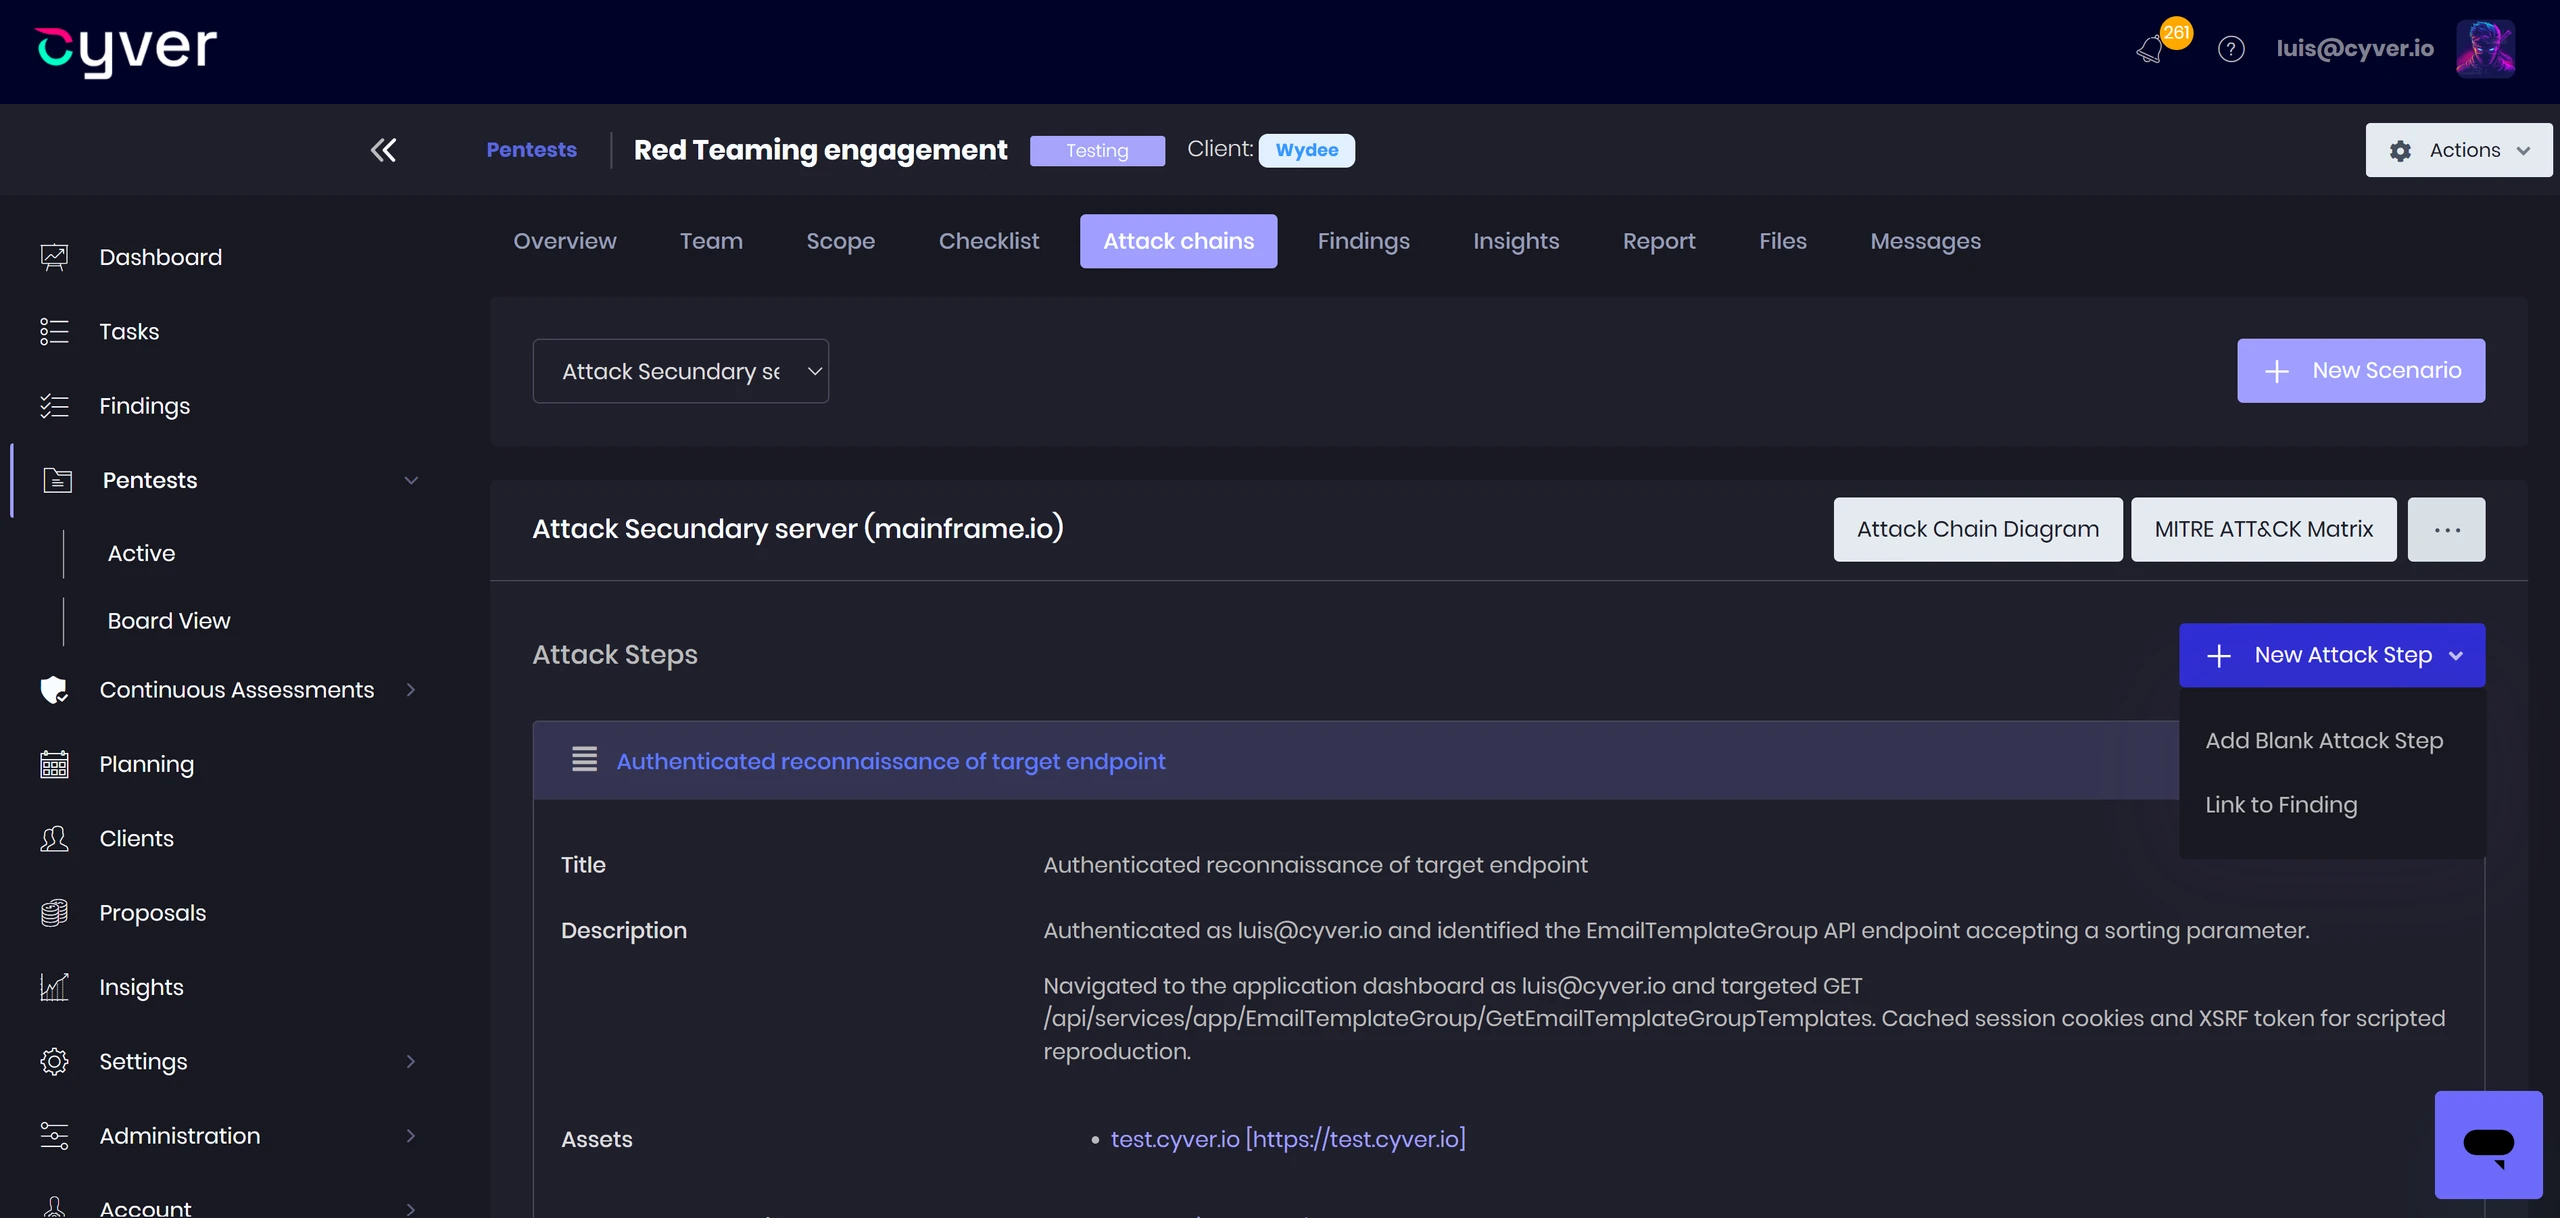
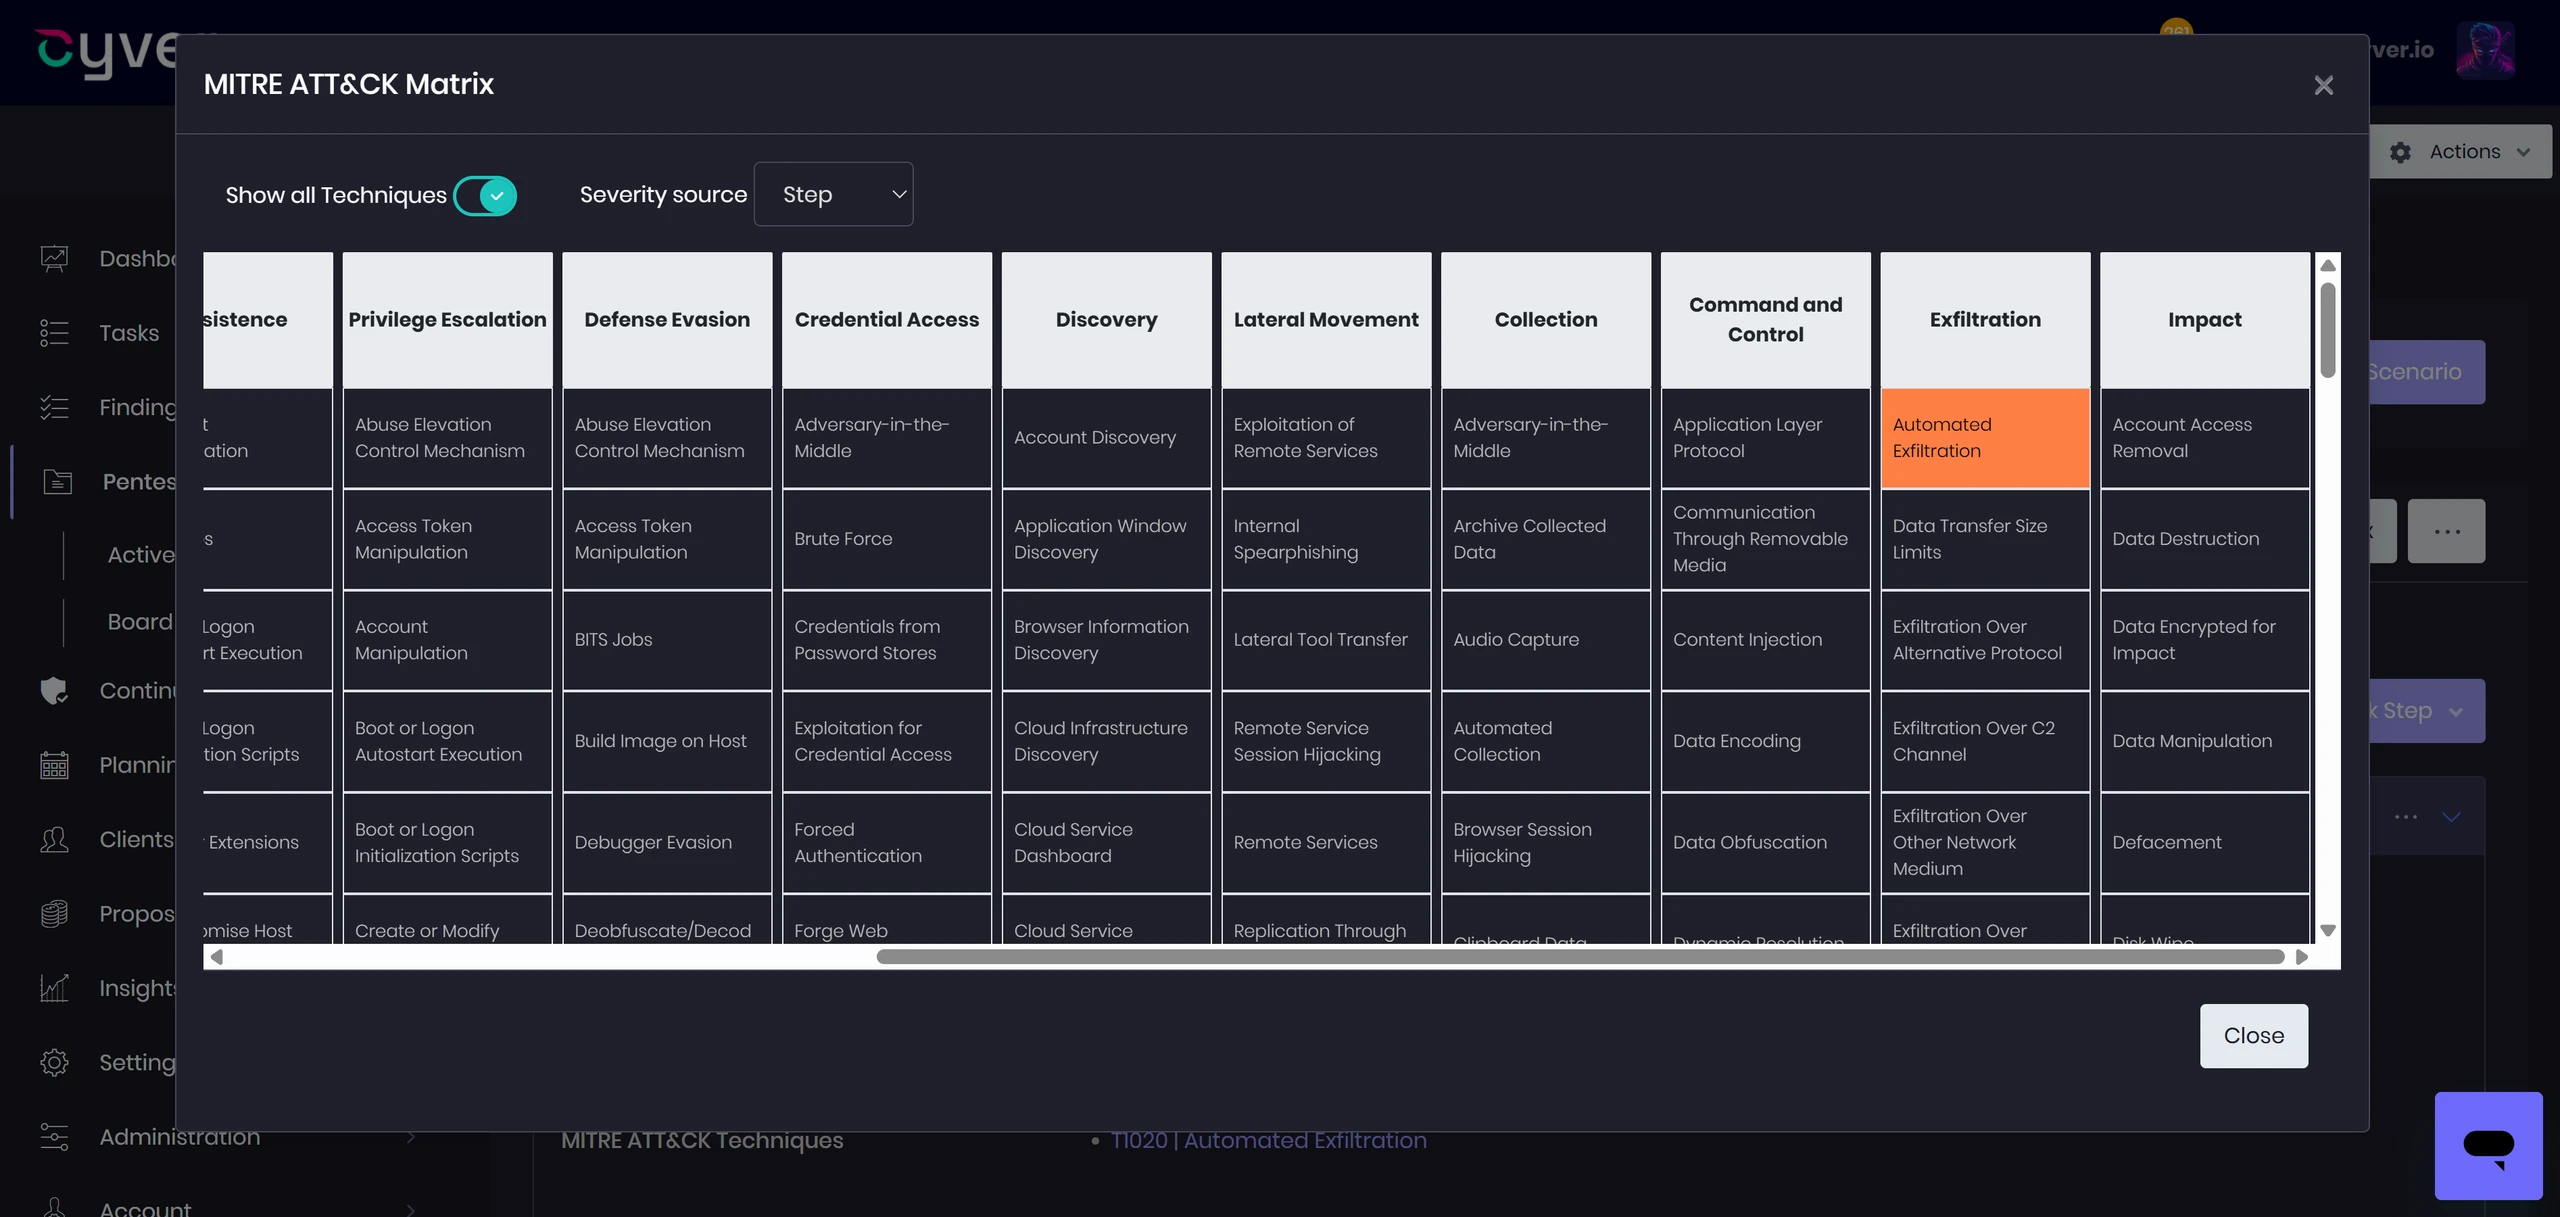
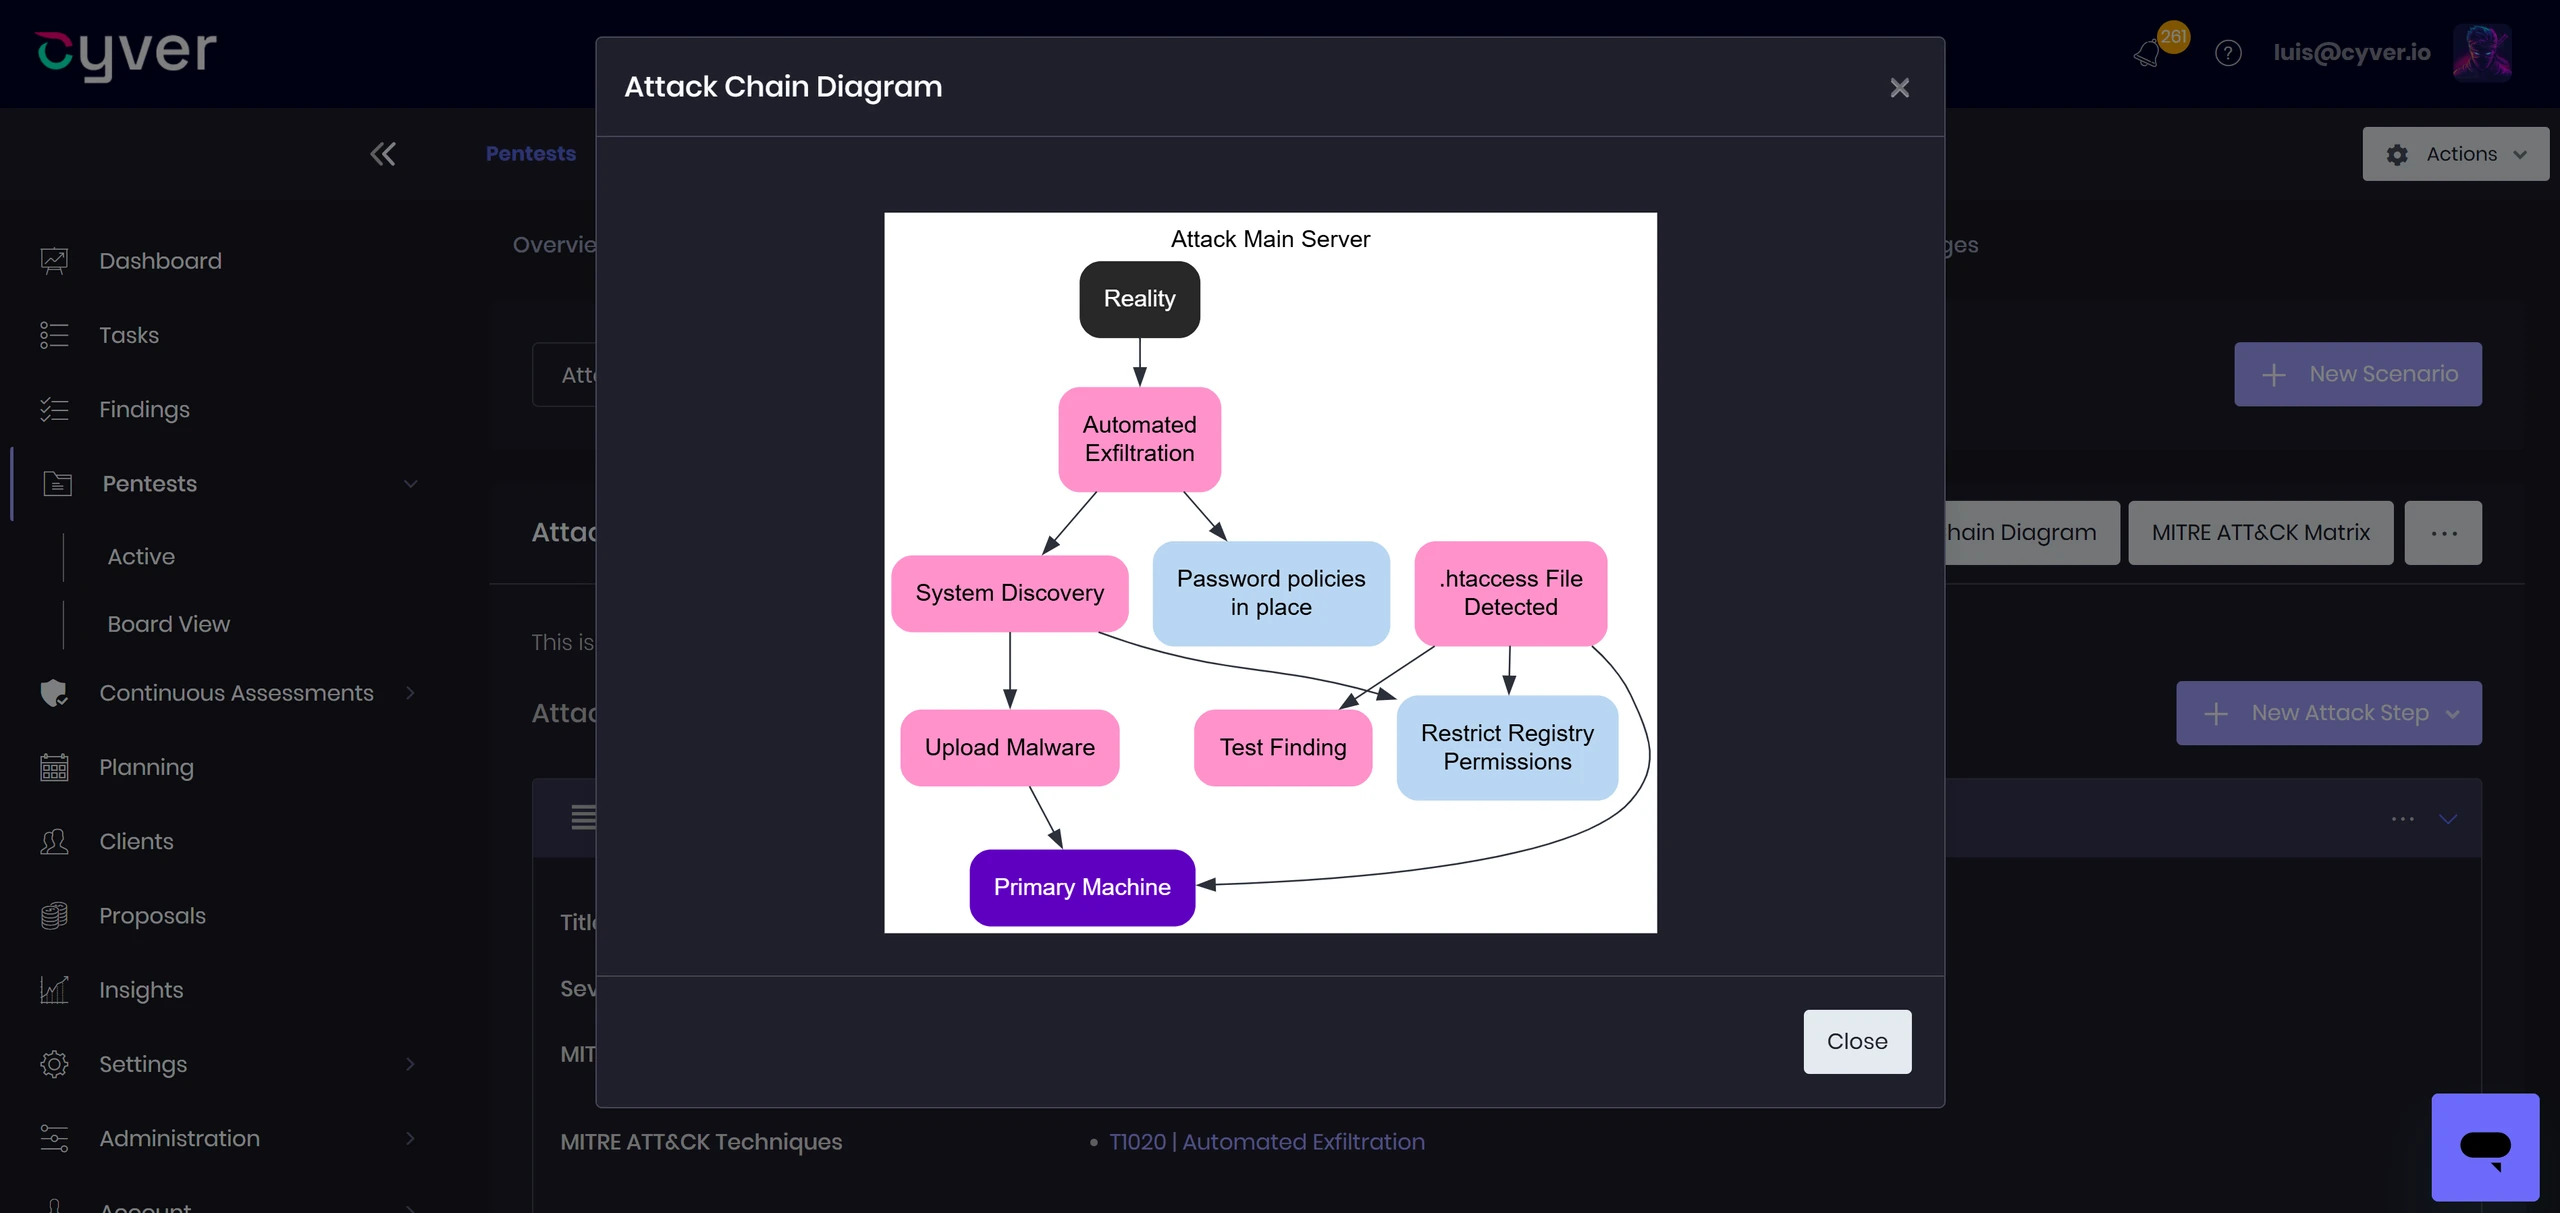
Plan and communicate adversary simulations with attack chain visibility and MITRE ATT&CK mapping.
Pentest-as-a-Service

Deliver continuous pentest engagements with consistent reporting and professional White-label client portal collaboration at scale.
Audit & Benchmarks

SOC

Vulnerability Management

CTEM

Vulnerability Management

Centralize vulnerabilities from multiple tools, validate exposures through testing, and collaborate with teams to track remediation and risk reduction.
Pentest Reporting

Standardize and Scale Pentest Reporting. From tool output to structured, consistent reports, delivered professionally to every client.

CTEM

Continuously identify, validate, prioritize, and reassess exposures through offensive testing workflows, attack surface visibility, and continuous security operations.
Audit & Benchmarks

SOC

Pentest-as-a-Service

Red Teaming
%

Customer Satisfaction

%

Customer Retention

%

Reporting Time

%

Repetitive Work
“The best investment we have made! We started using Cyver Core software over two years ago and it has been the best investment we have made since we started our business. The task checklists cover every pentesting framework imaginable and help us manage our team effectively.” 

Founder and Managing Director, WardenSec
Vratislav Pavel Skořepa
Features

The Full Pentest Journey

From onboarding and testing to reporting and remediation, Cyver connects every step of your pentest lifecycle.
1. Scoping Braces Content

Initiate and structure engagements from the start.

  • Scoping requests – Collect targets and requirements through custom forms.
  • Quotes and SoWs – Prepare proposals for client approval and signature.
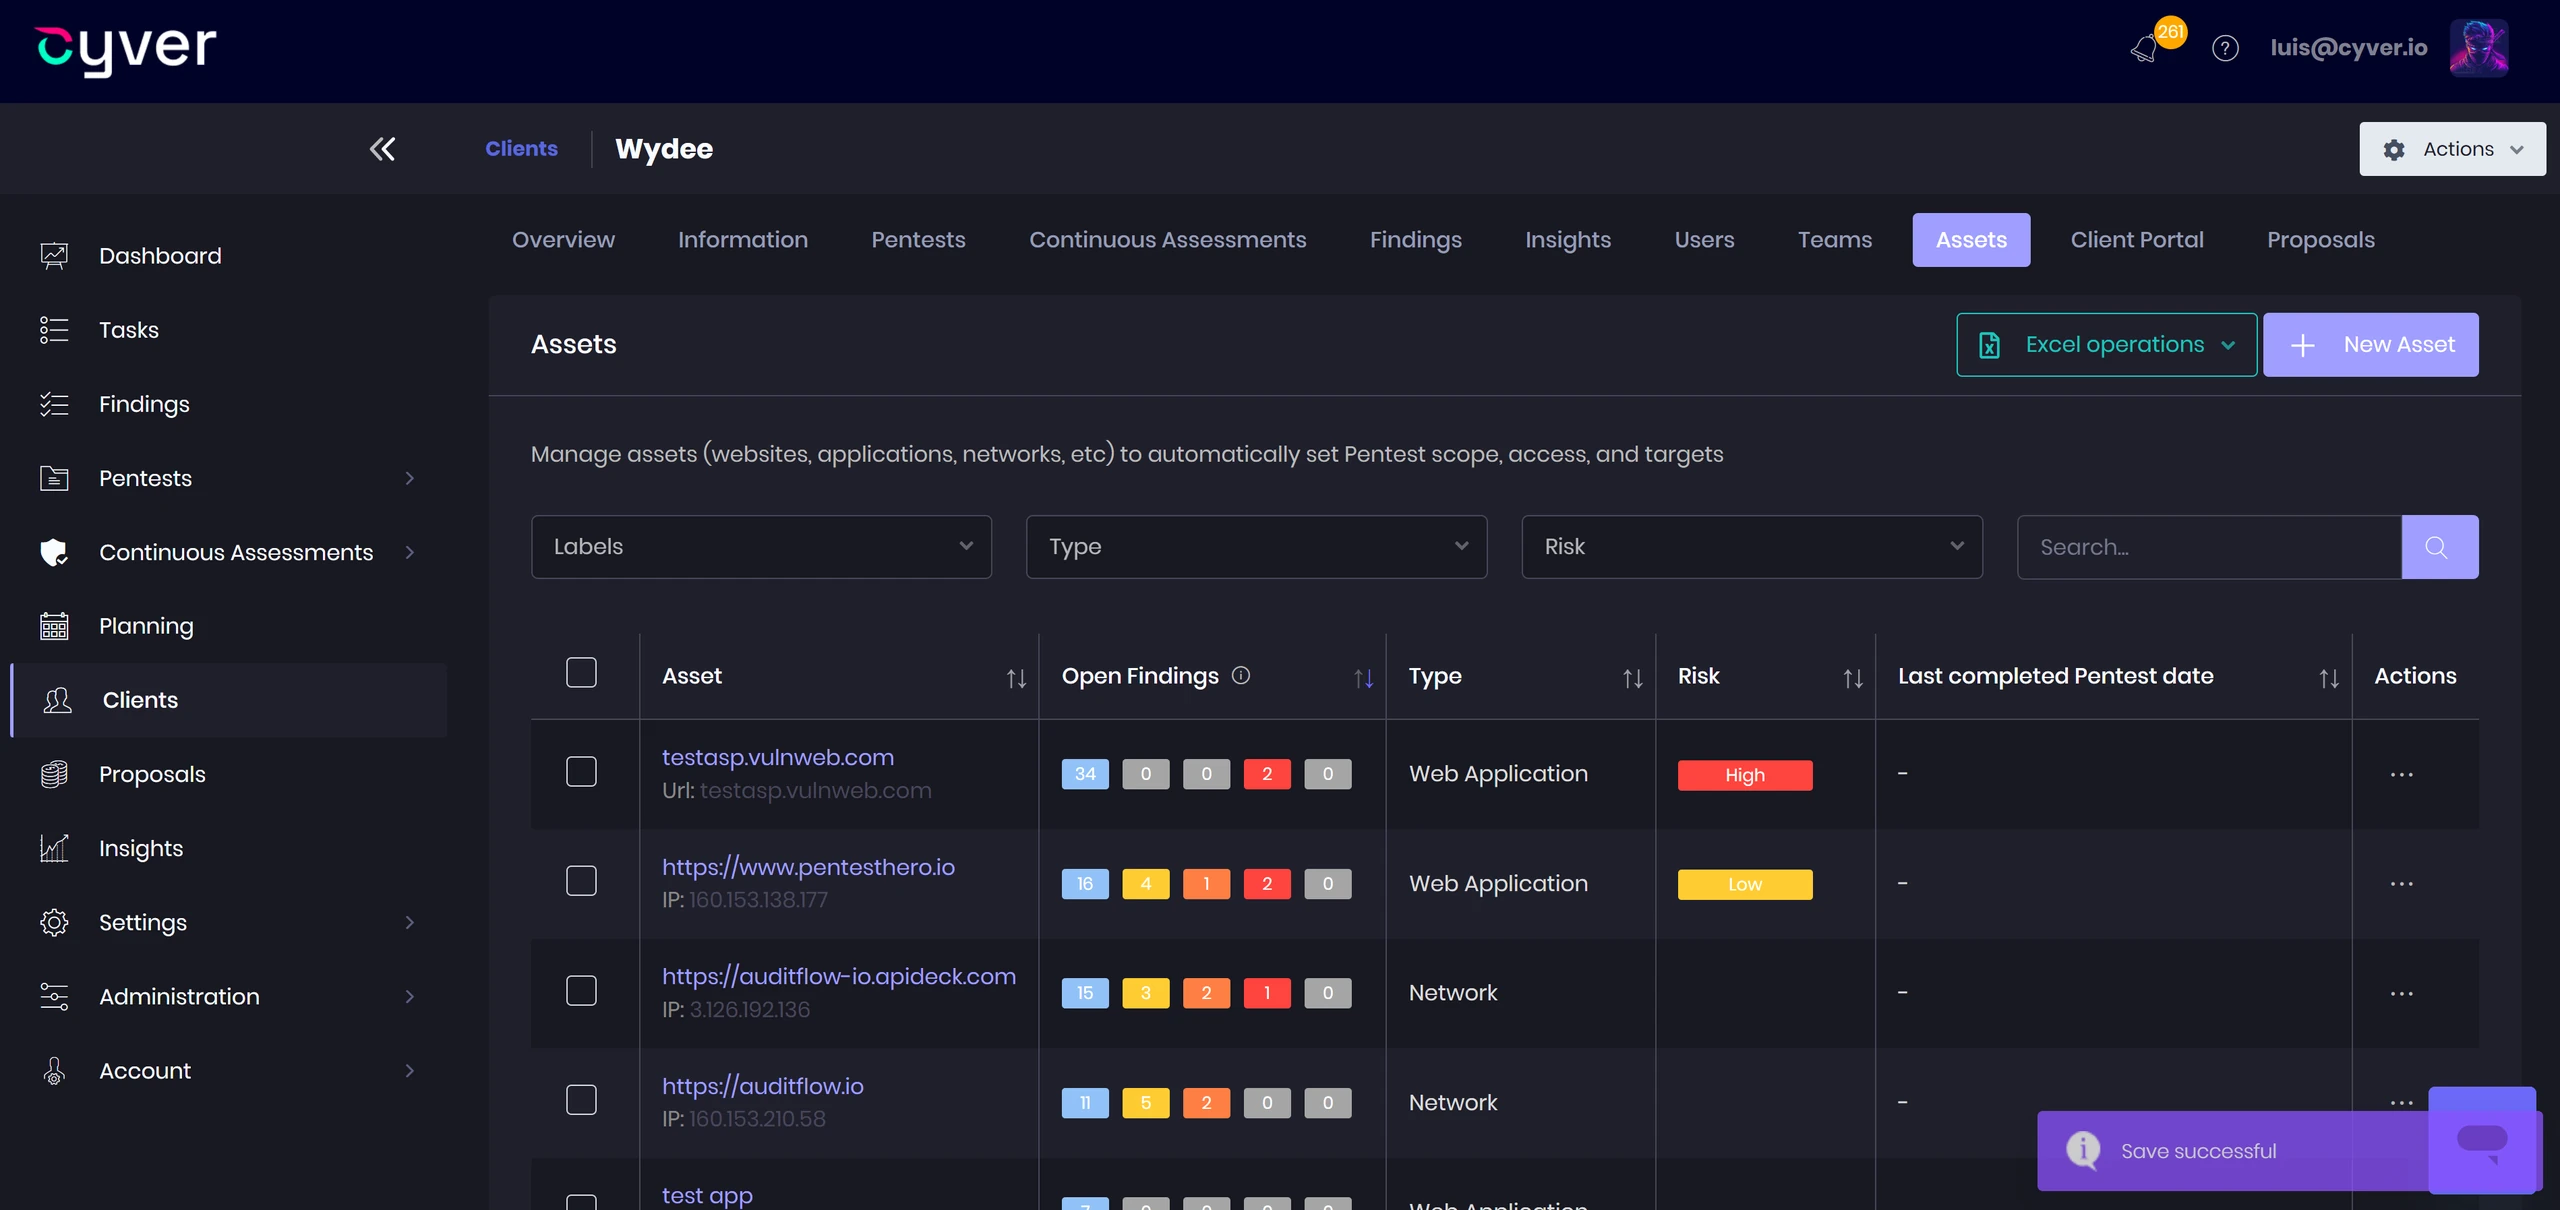
  • Target assets – Manage in-scope assets with Excel import and export.
  • Engagement templates – Reuse workflows, checklists, and custom fields.
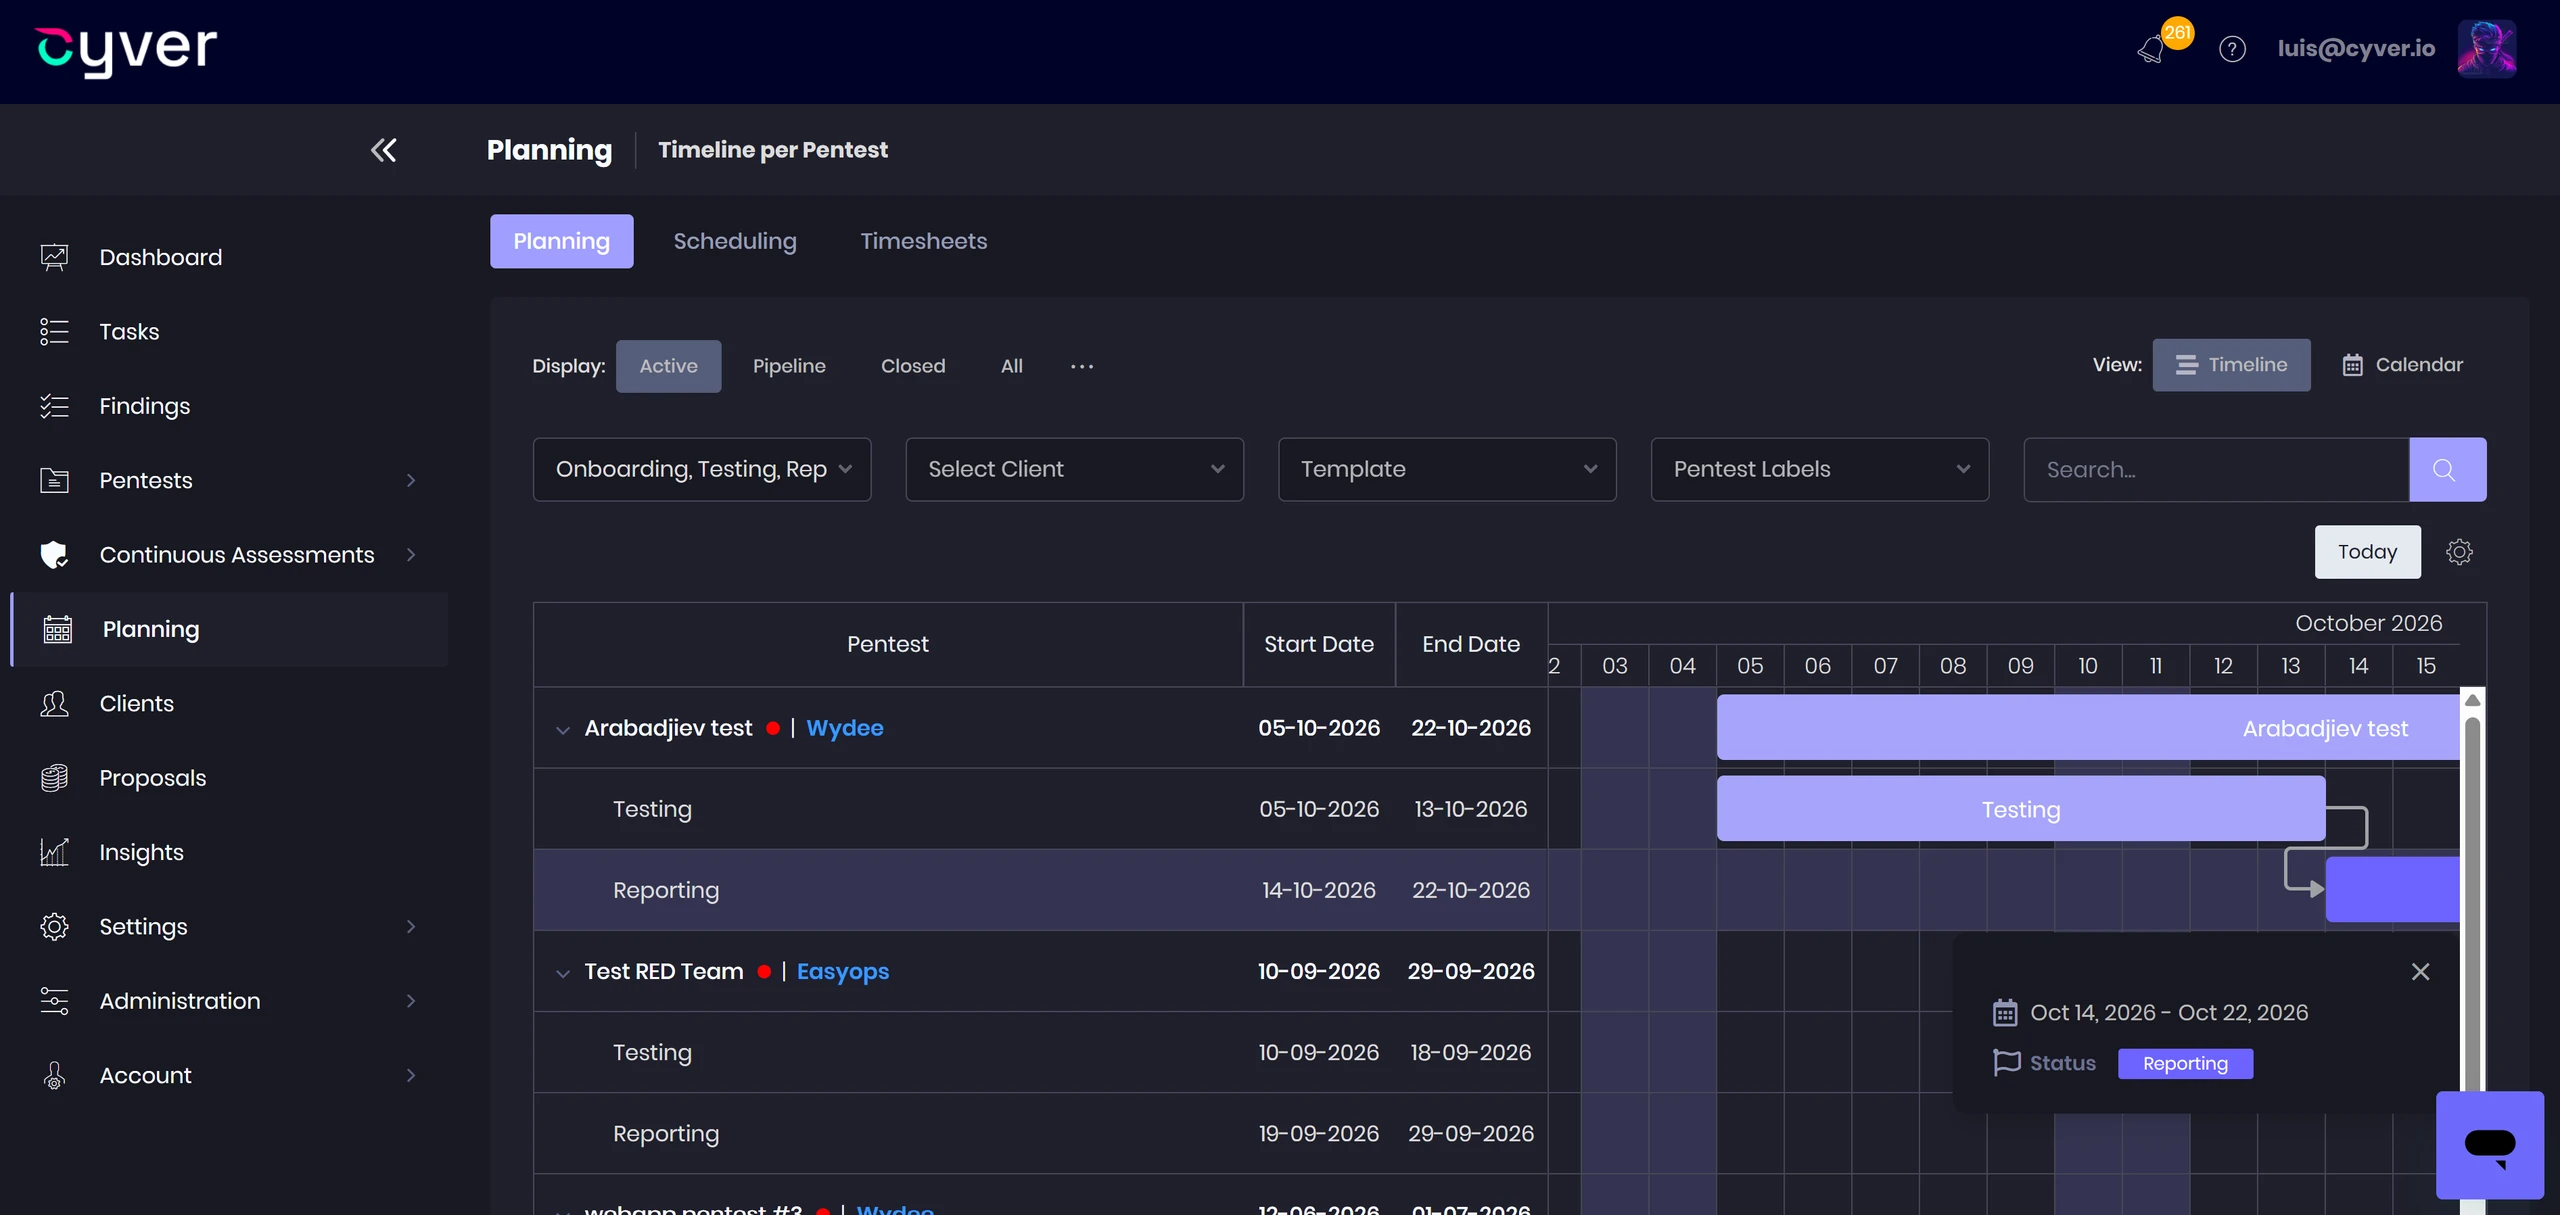
  • Team planning – Schedule pentesters through calendar and Gantt views.
2. Testing Braces Content

Run structured pentest and red team operations.
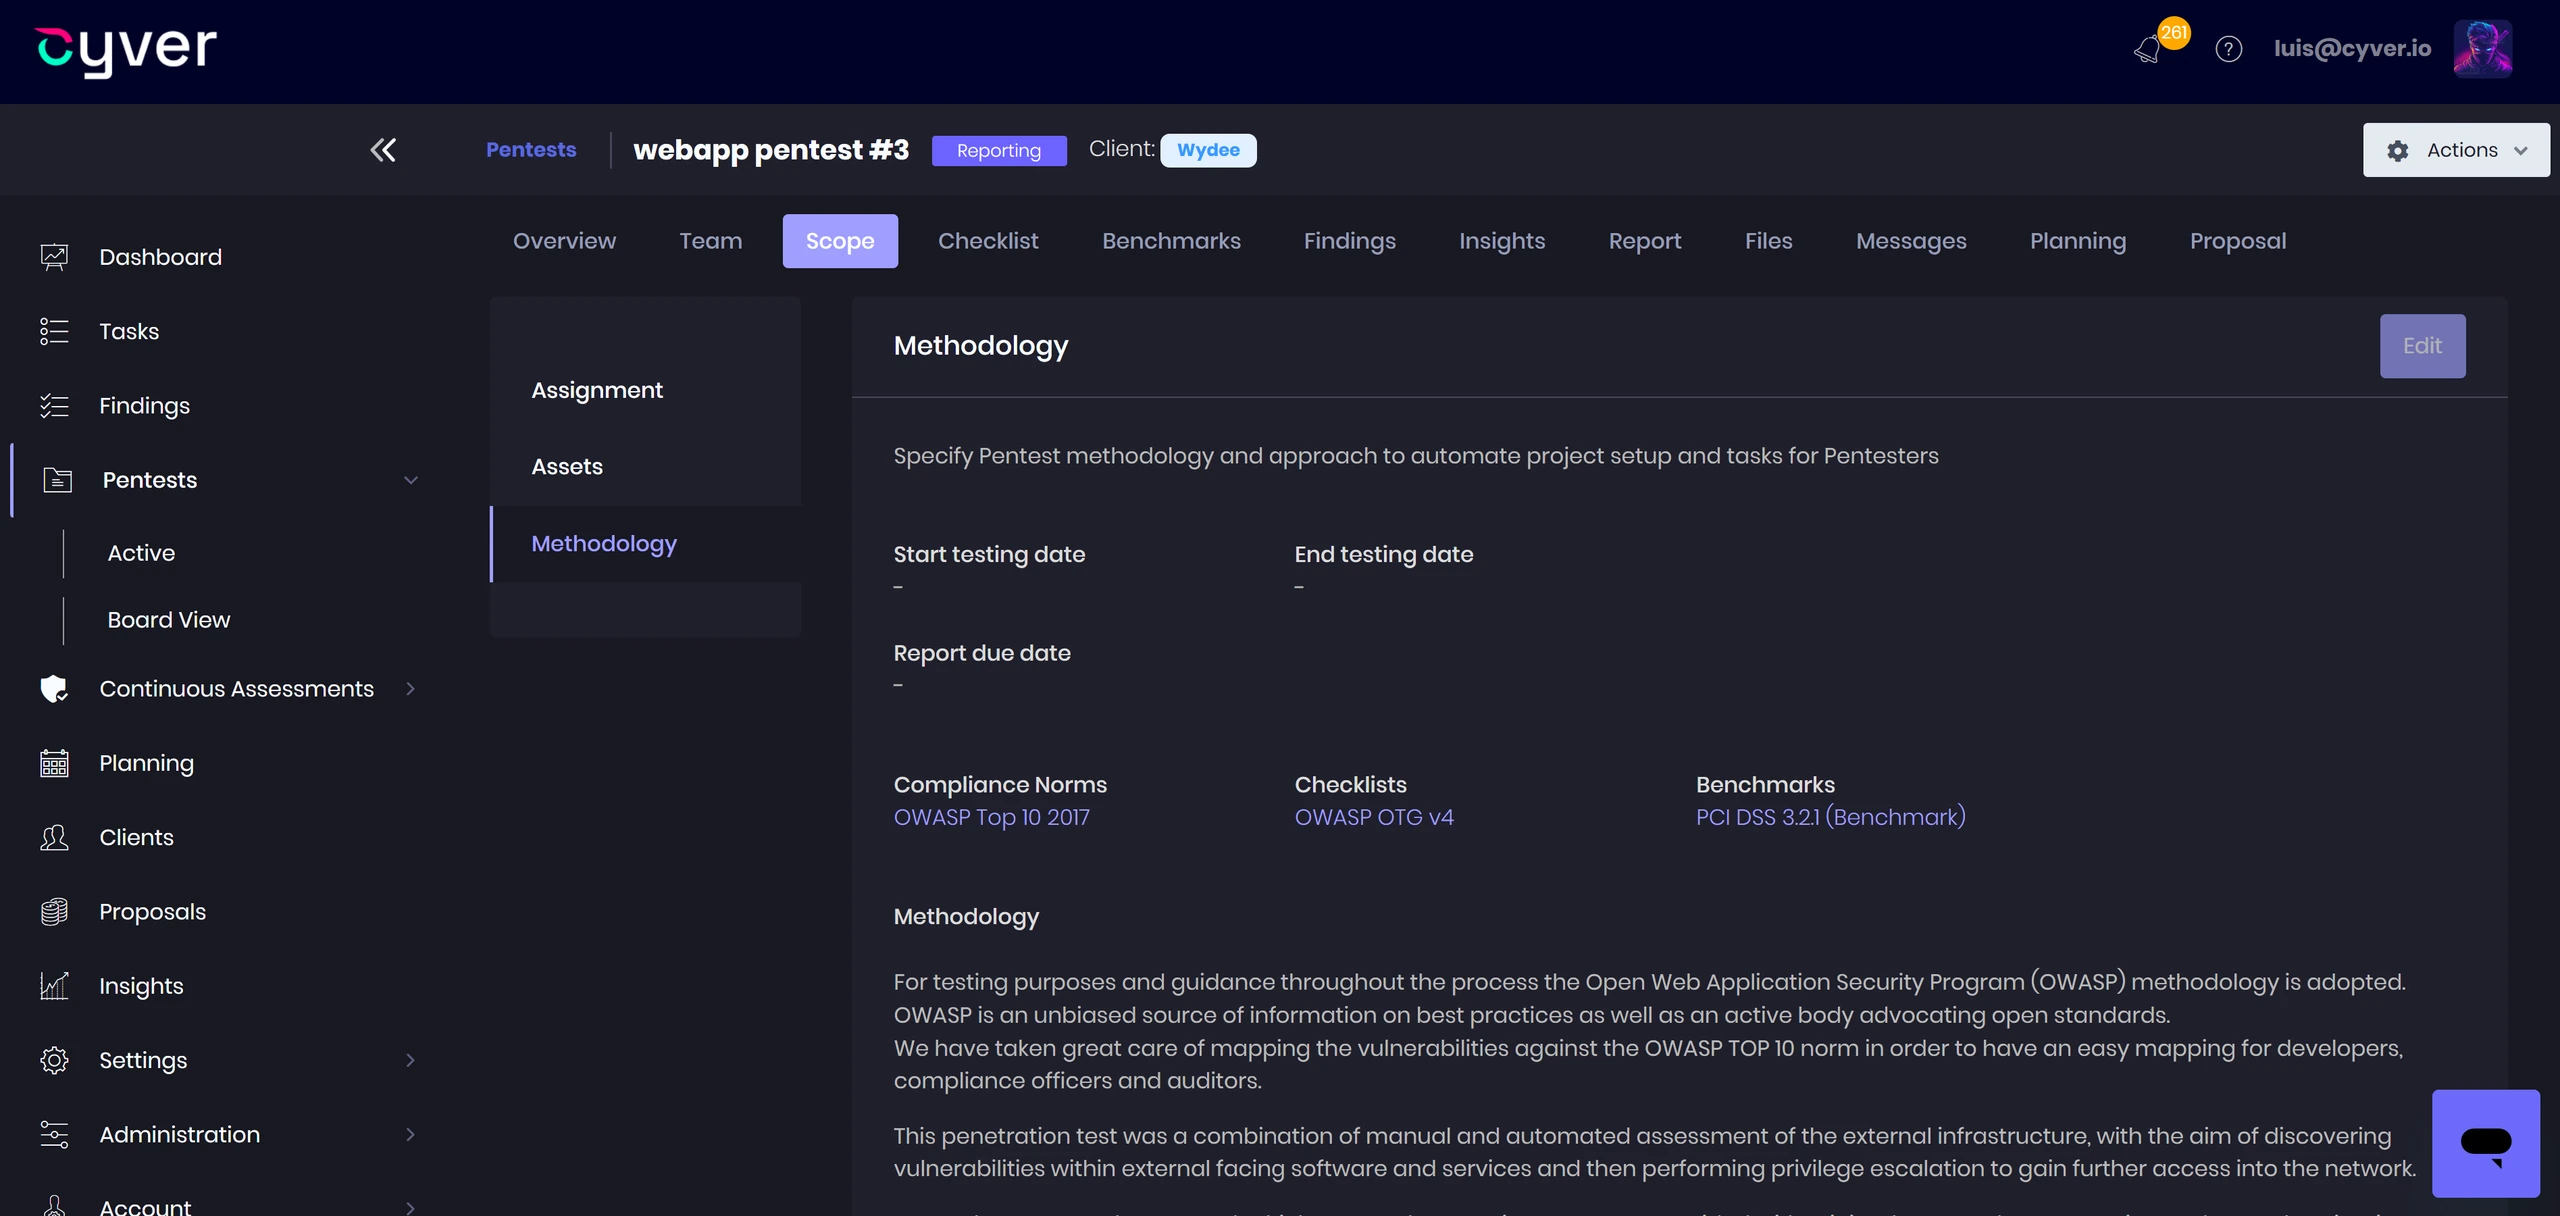
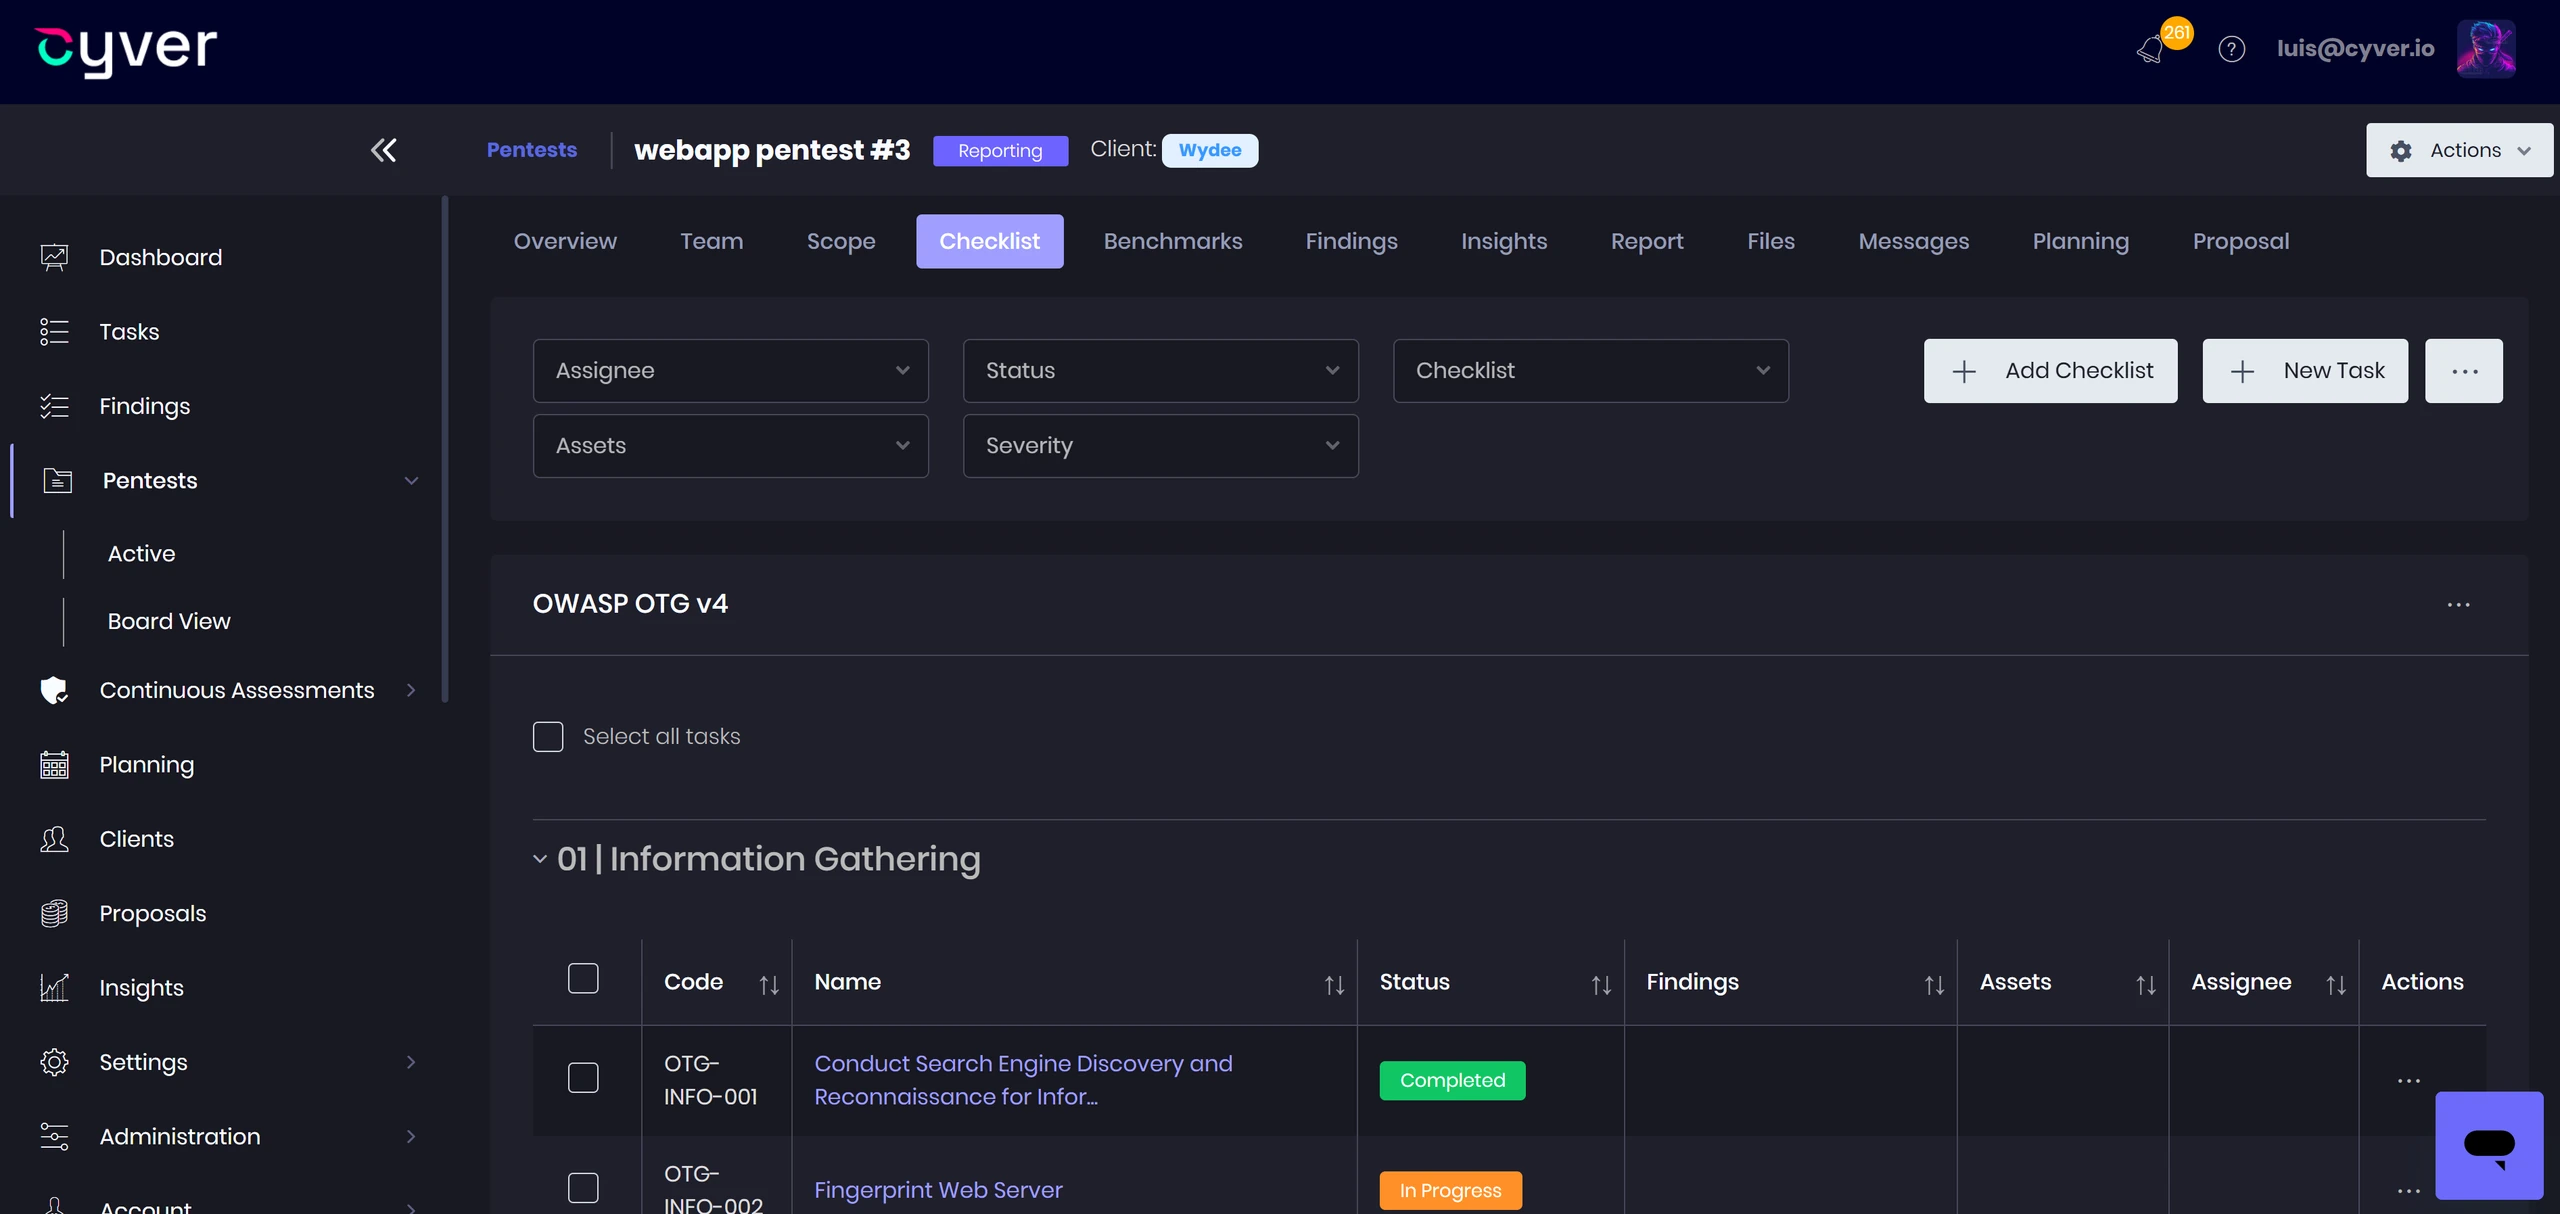
  • Testing checklists – Use OWASP OTG, ASVS, or custom procedures.
  • Asset-linked coverage – Link testing tasks to assets across methodologies.
  • Benchmarks and frameworks – Apply CIS Benchmarks, OWASP Top 10, and PCI DSS.
  • Red team scenarios – Map objectives, ATT&CK techniques, and attack chains.
  • AI and MCP access – Retrieve context and update permitted data through AI assistants.

3. Finding Management Braces Content

Centralize and structure all security findings.
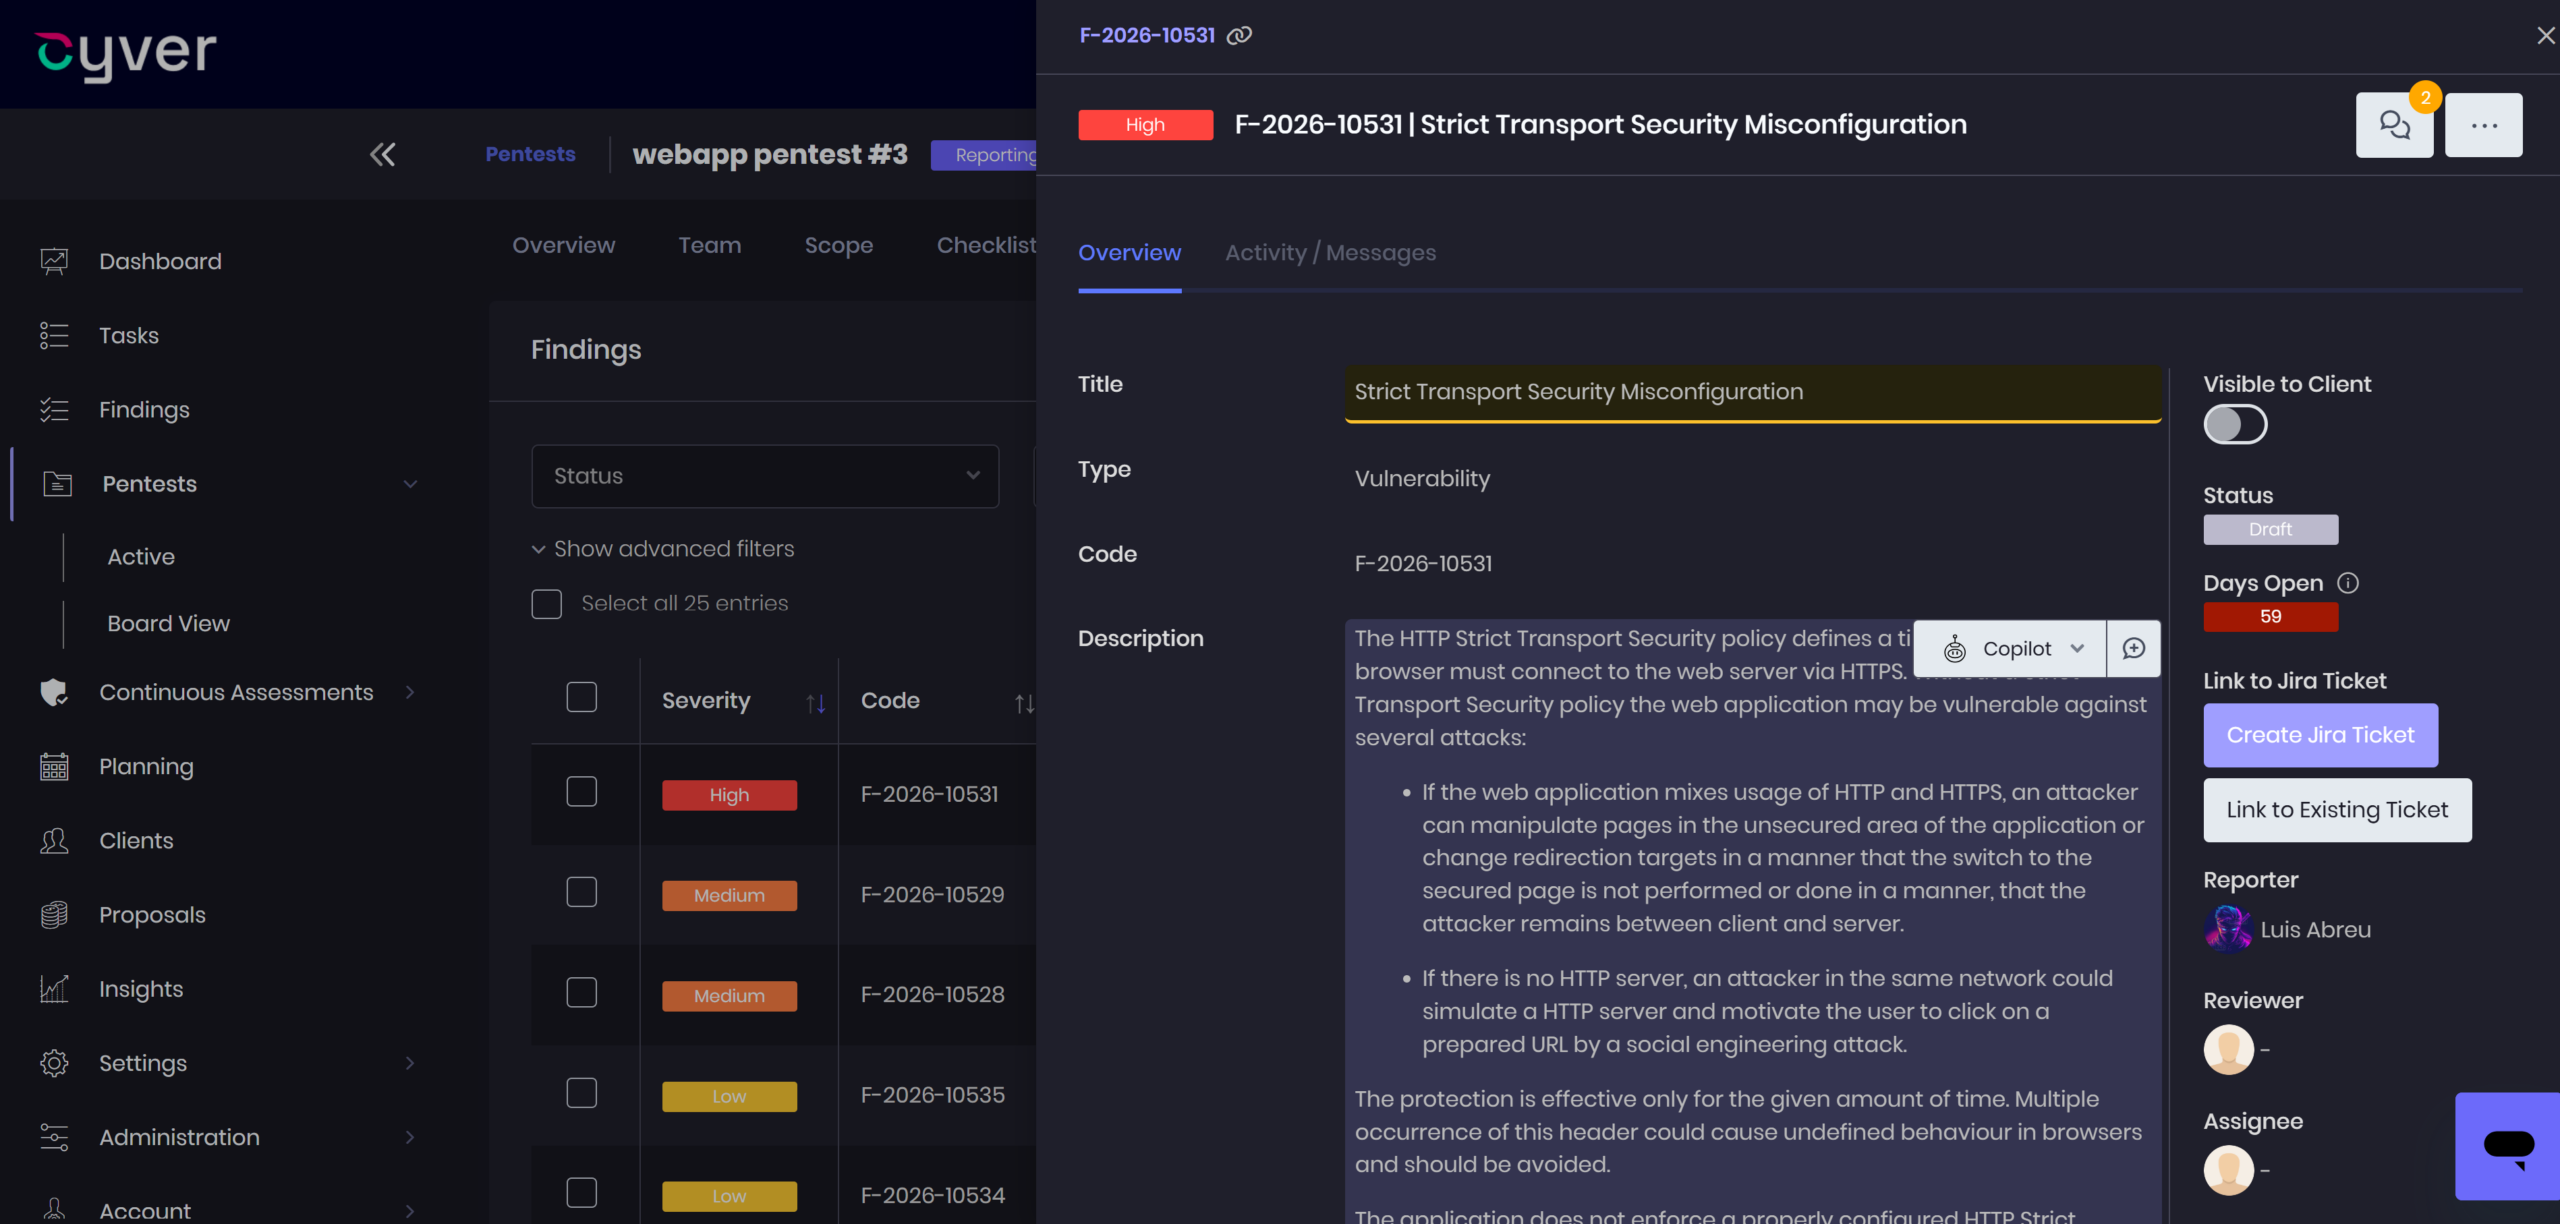
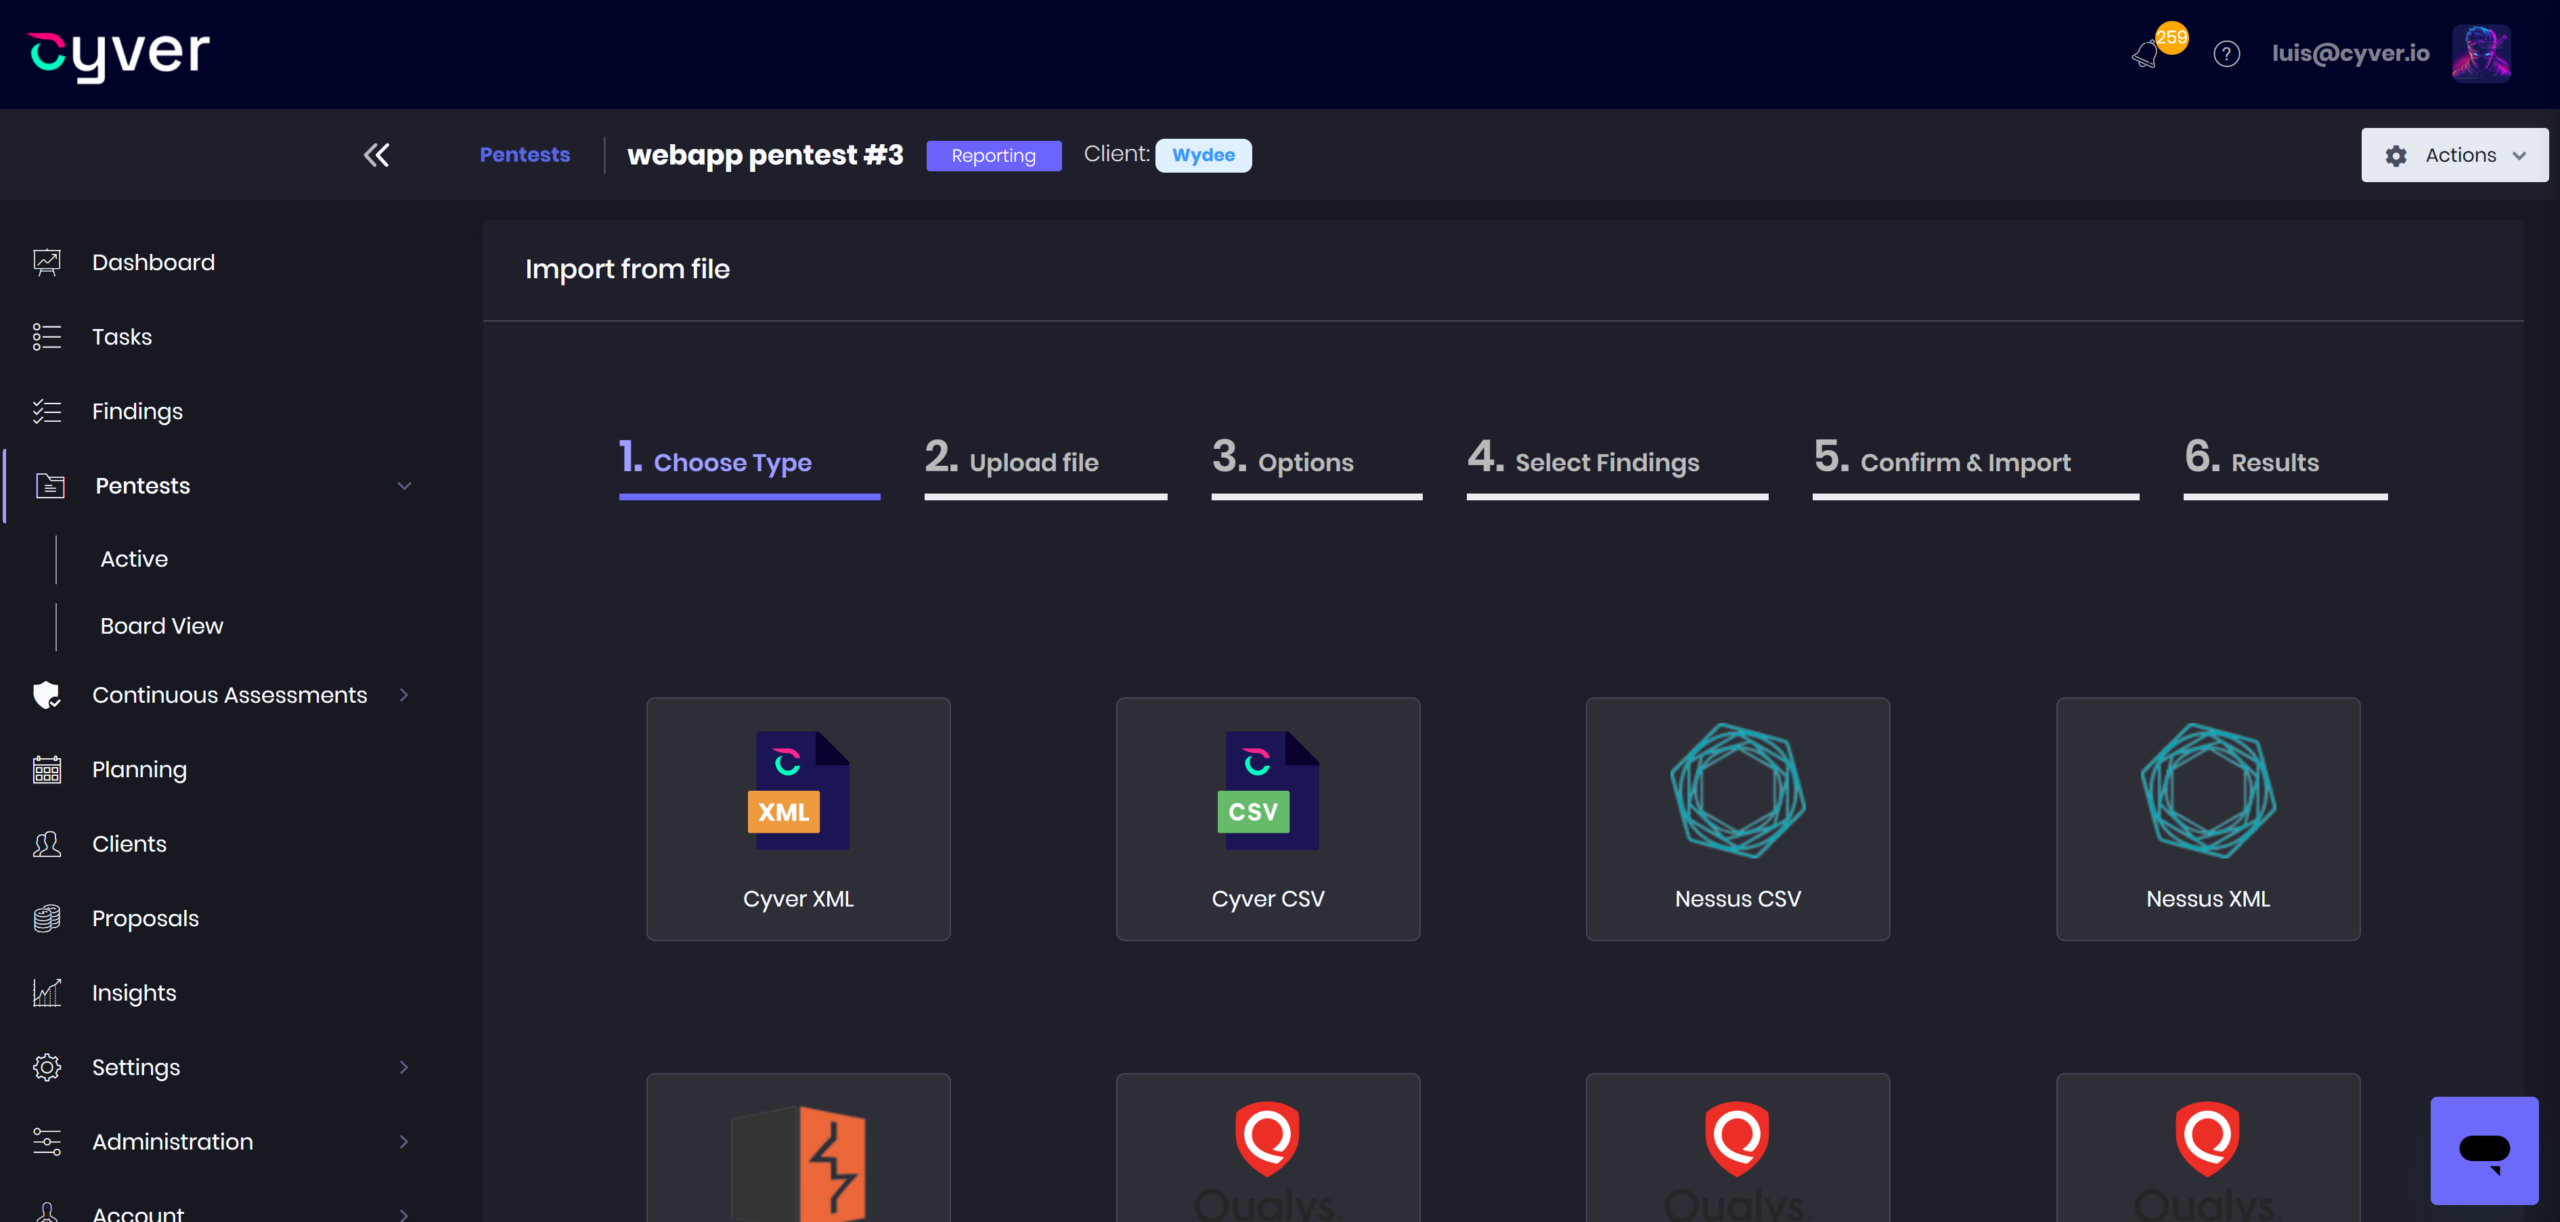
  • Tool imports – Import Burp Suite, Nessus, Nmap, Qualys, and other outputs.
  • Libraries and enrichment – Reuse write-ups with CVE, CWE, and Exploit-DB references.
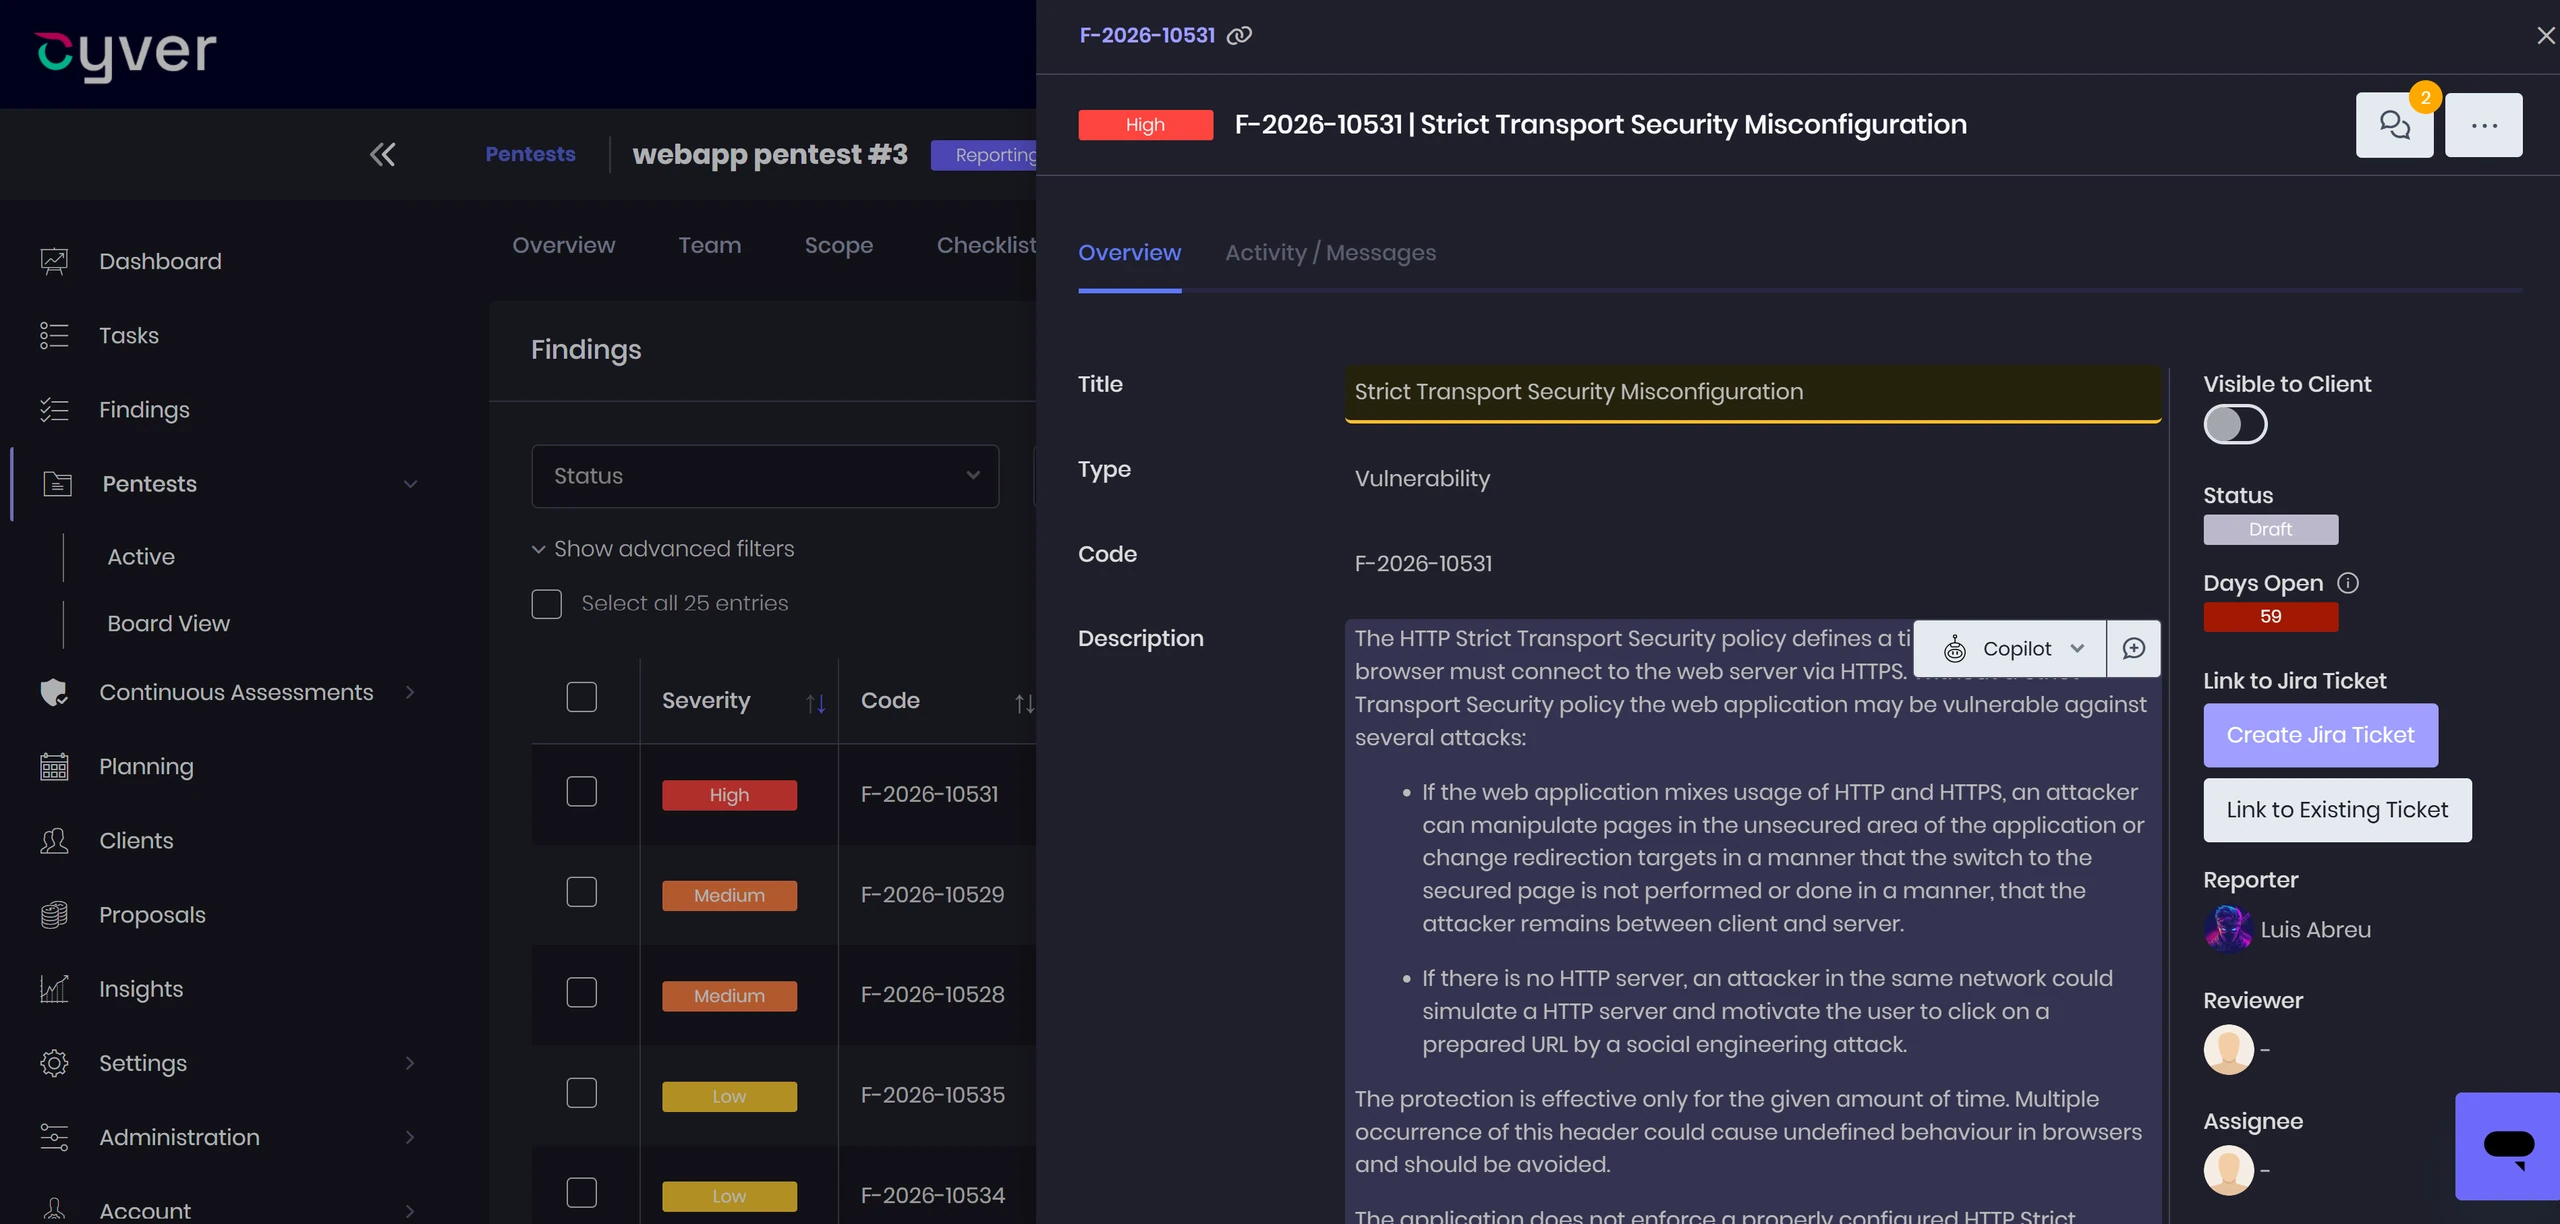
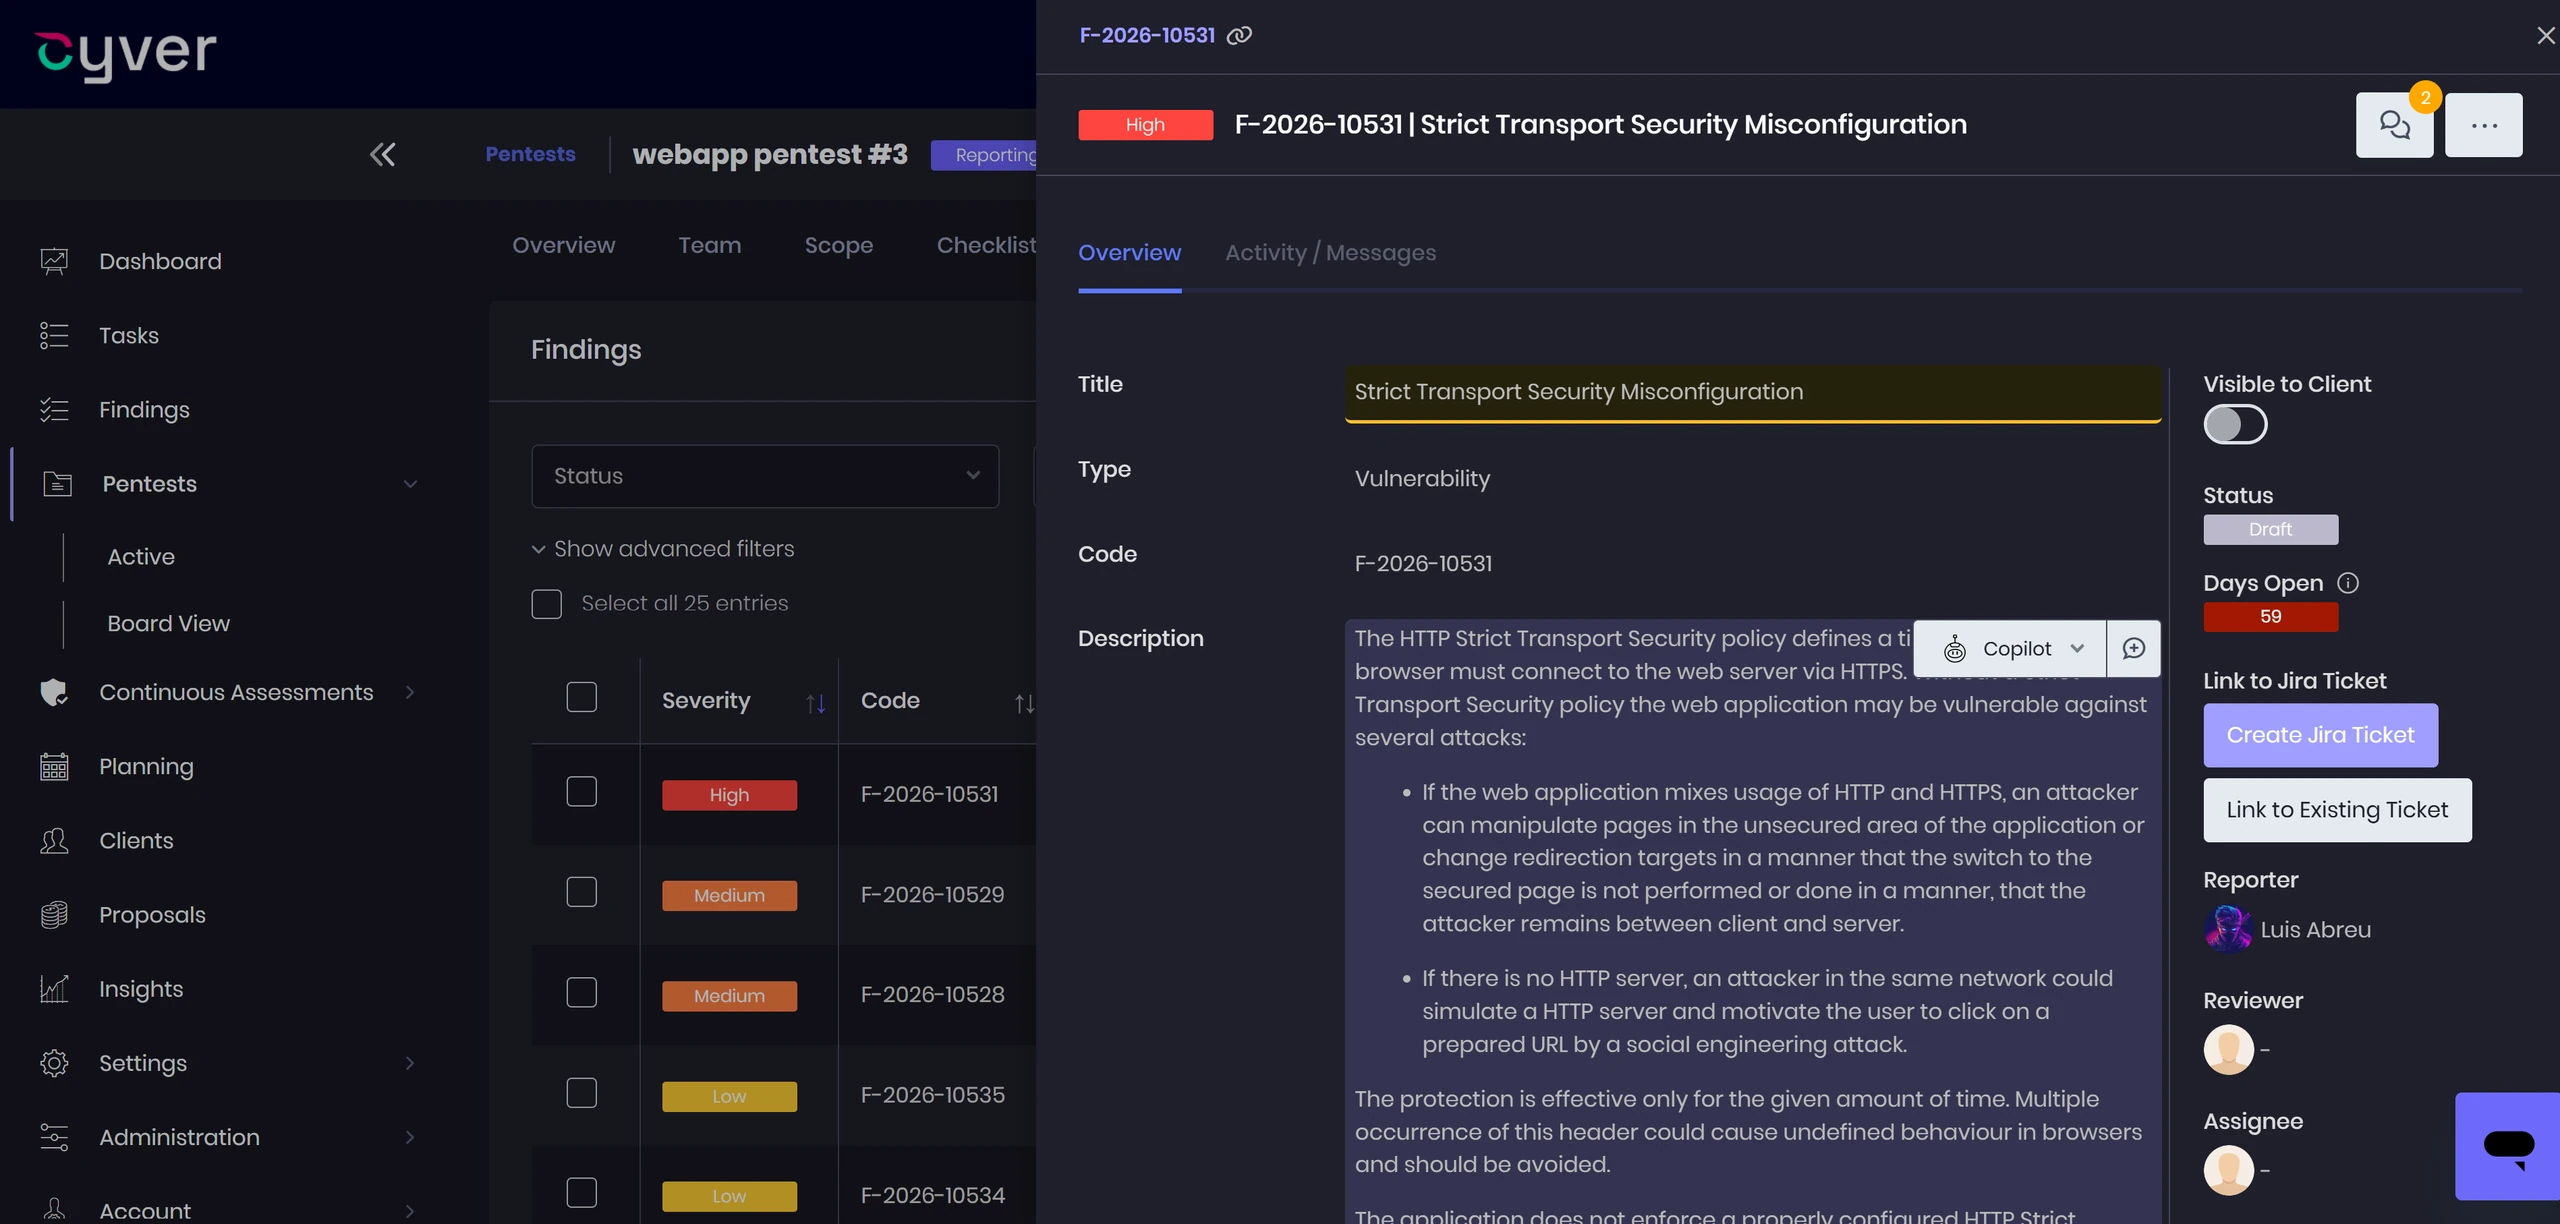
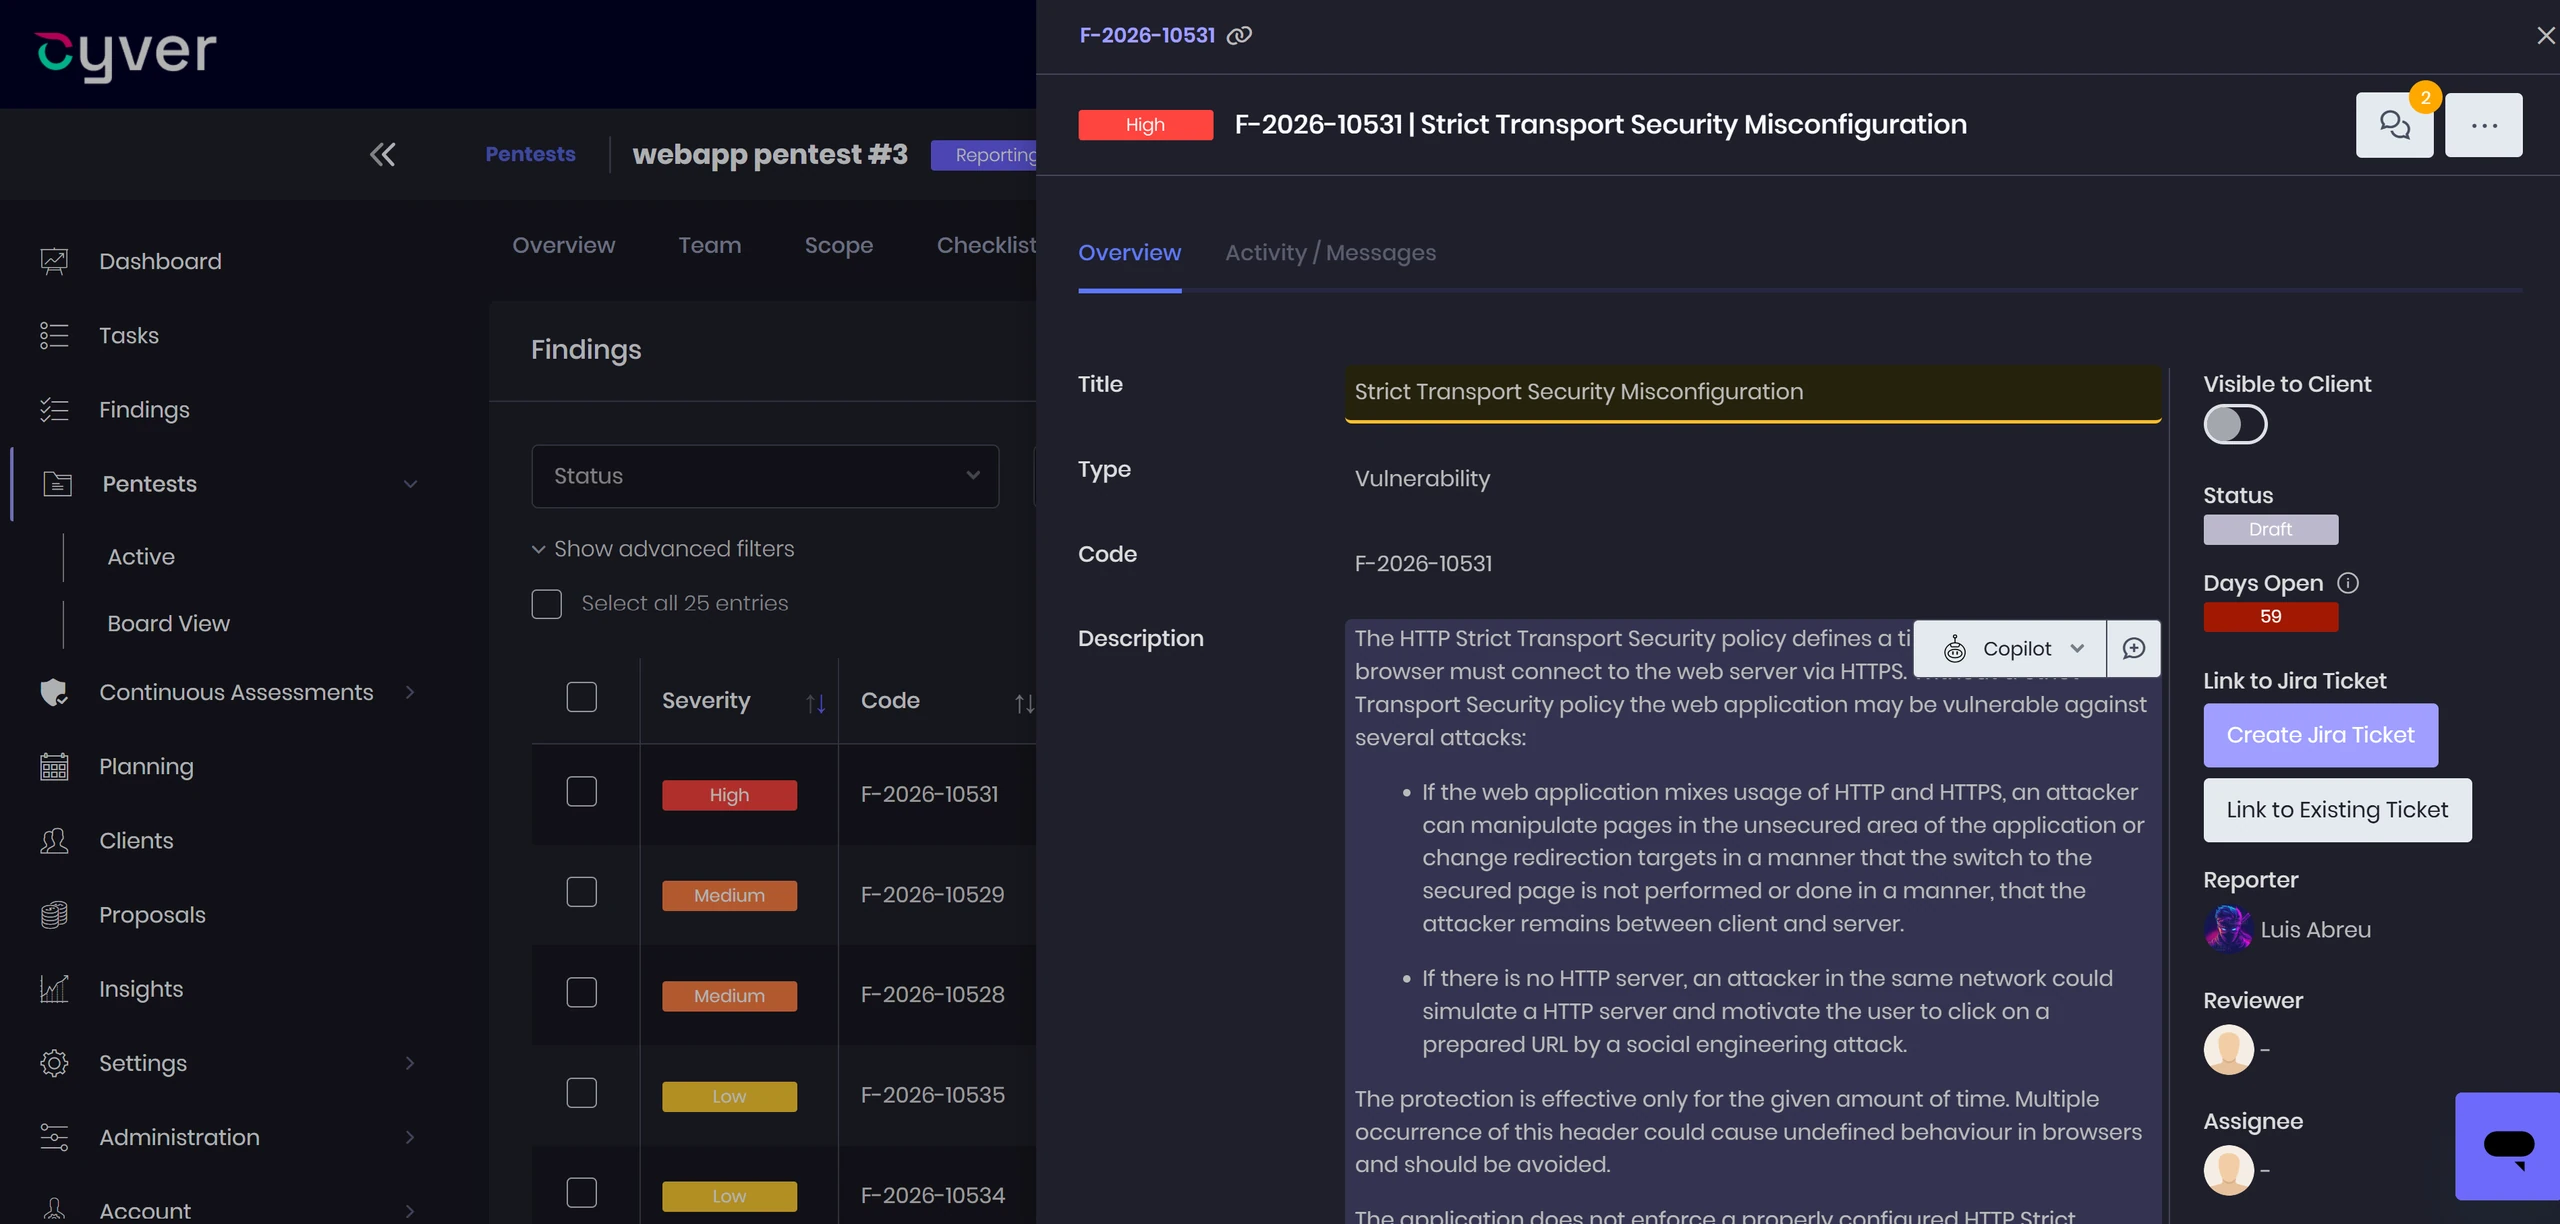
  • Technical evidence – Capture reproduction steps, affected assets, and supporting evidence.
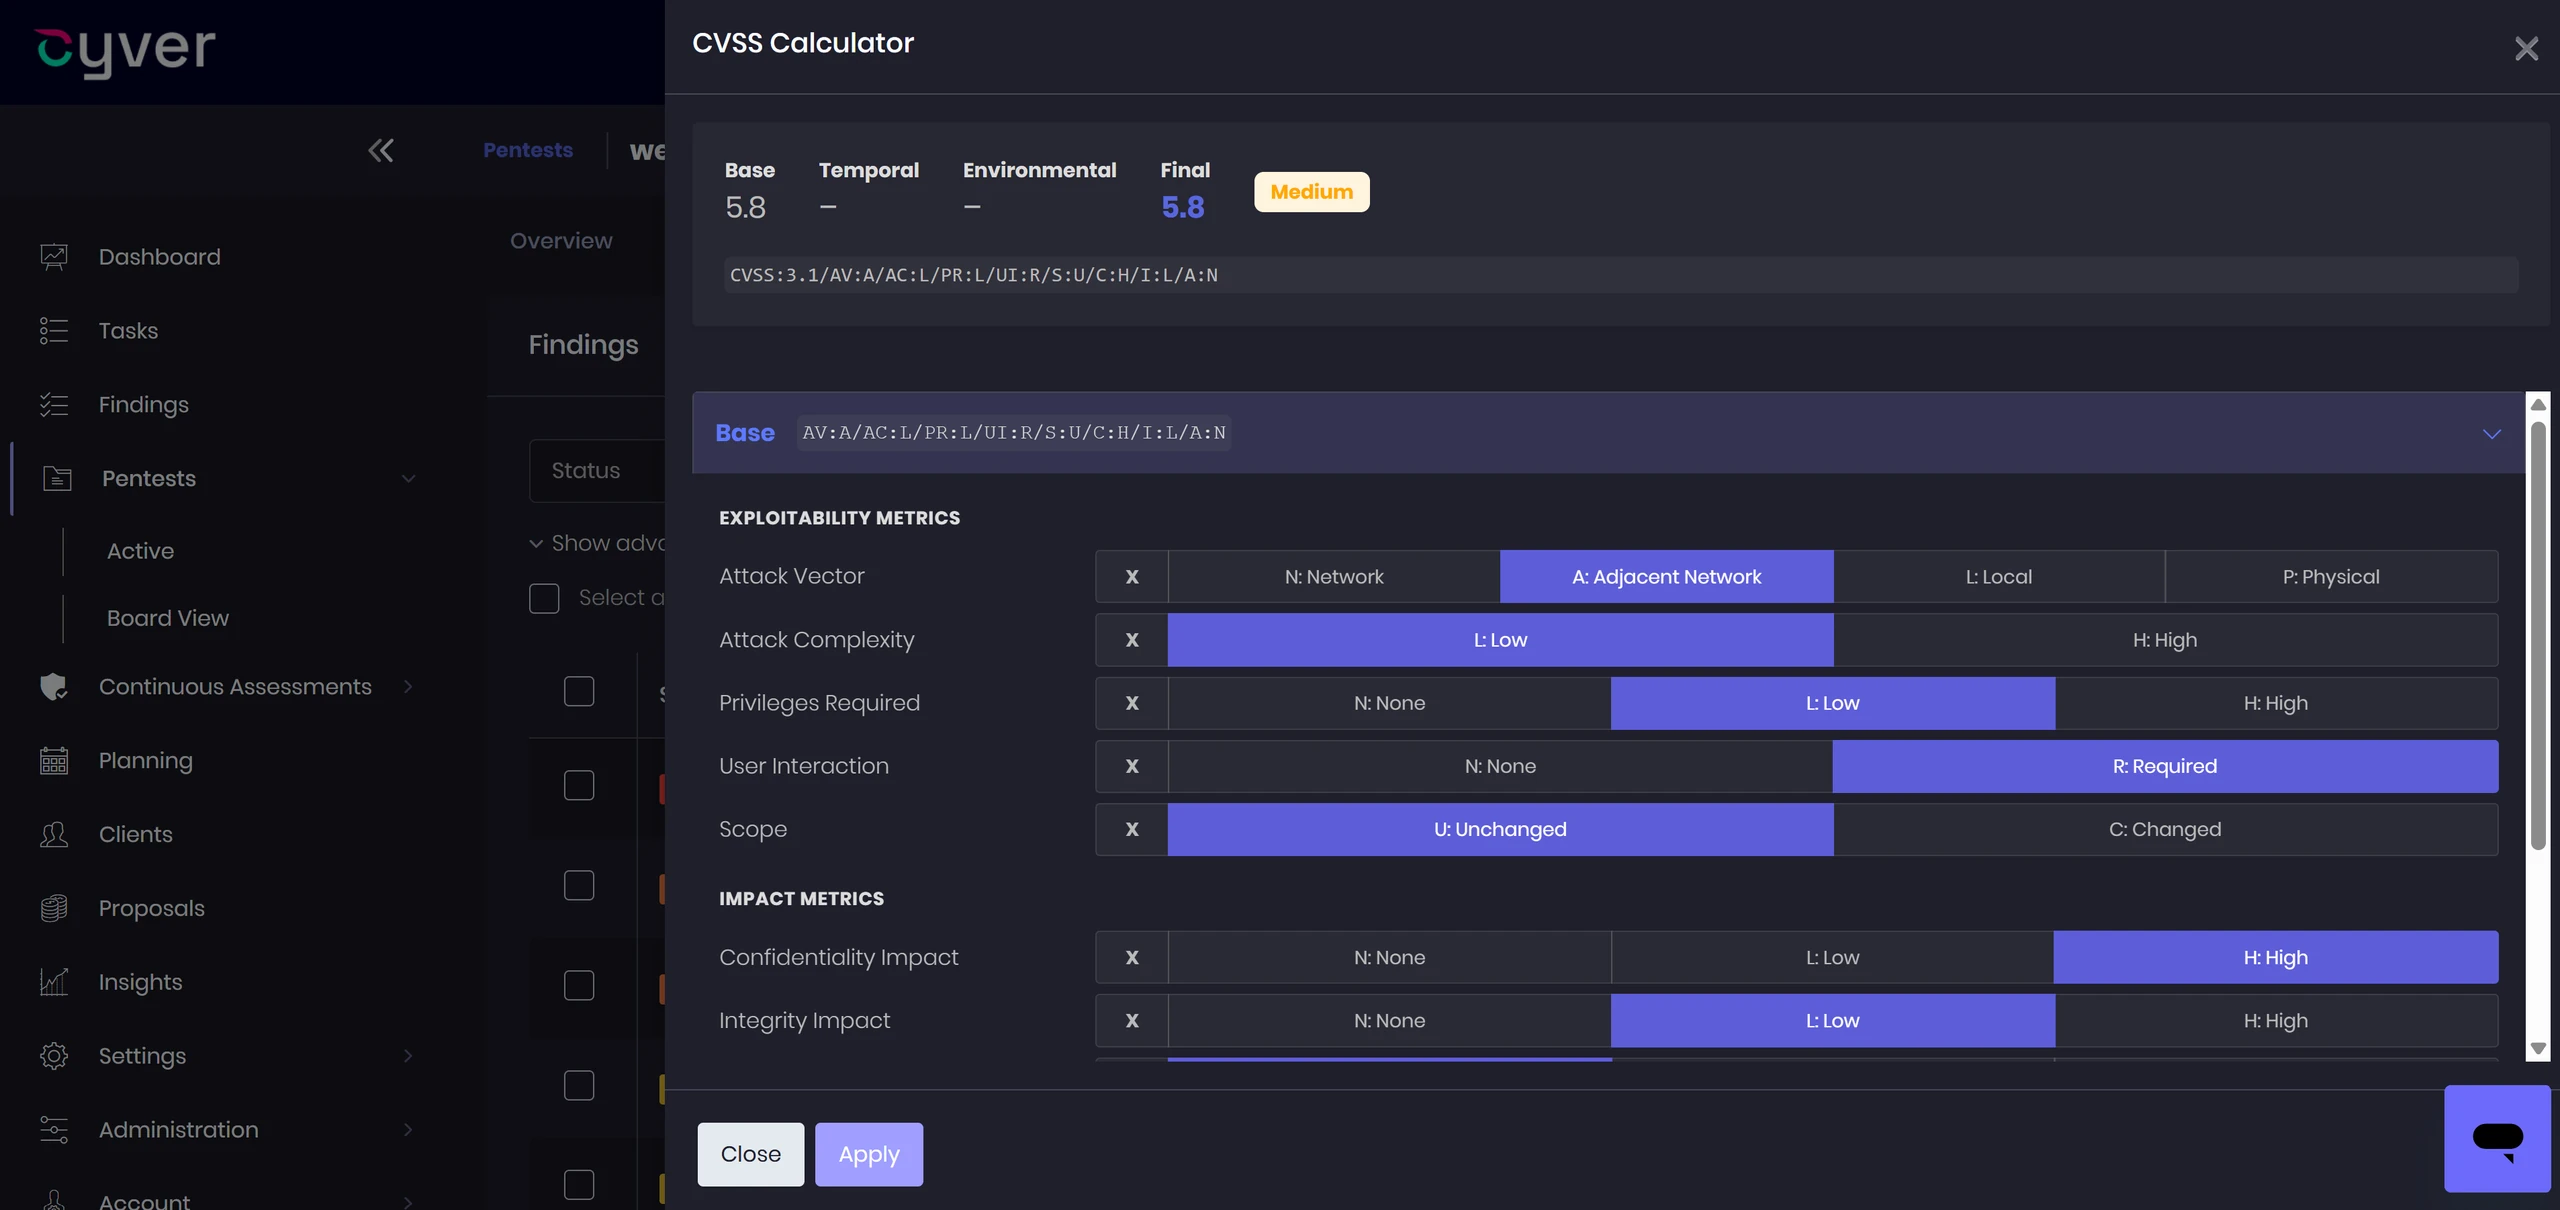
  • CVSS and custom scoring – Rate findings with the CVSS calculator or custom scores.
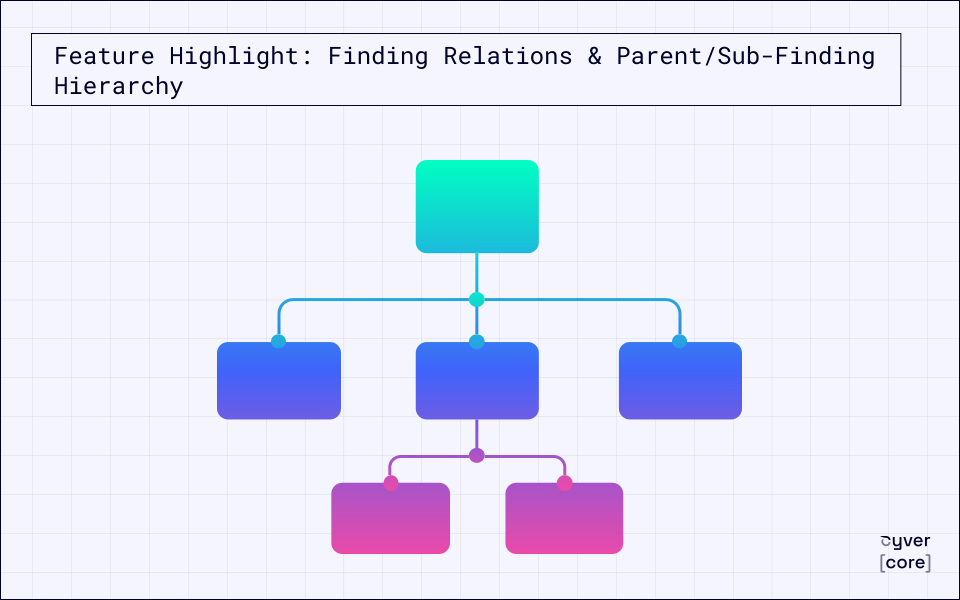
  • Finding relationships – Merge, clone, and link findings in parent/sub-finding structures.

4. Reporting and Delivery Braces Content

Turn findings into clear, professional deliverables.

  • Report templates – Customize branding, sections, and reusable content.
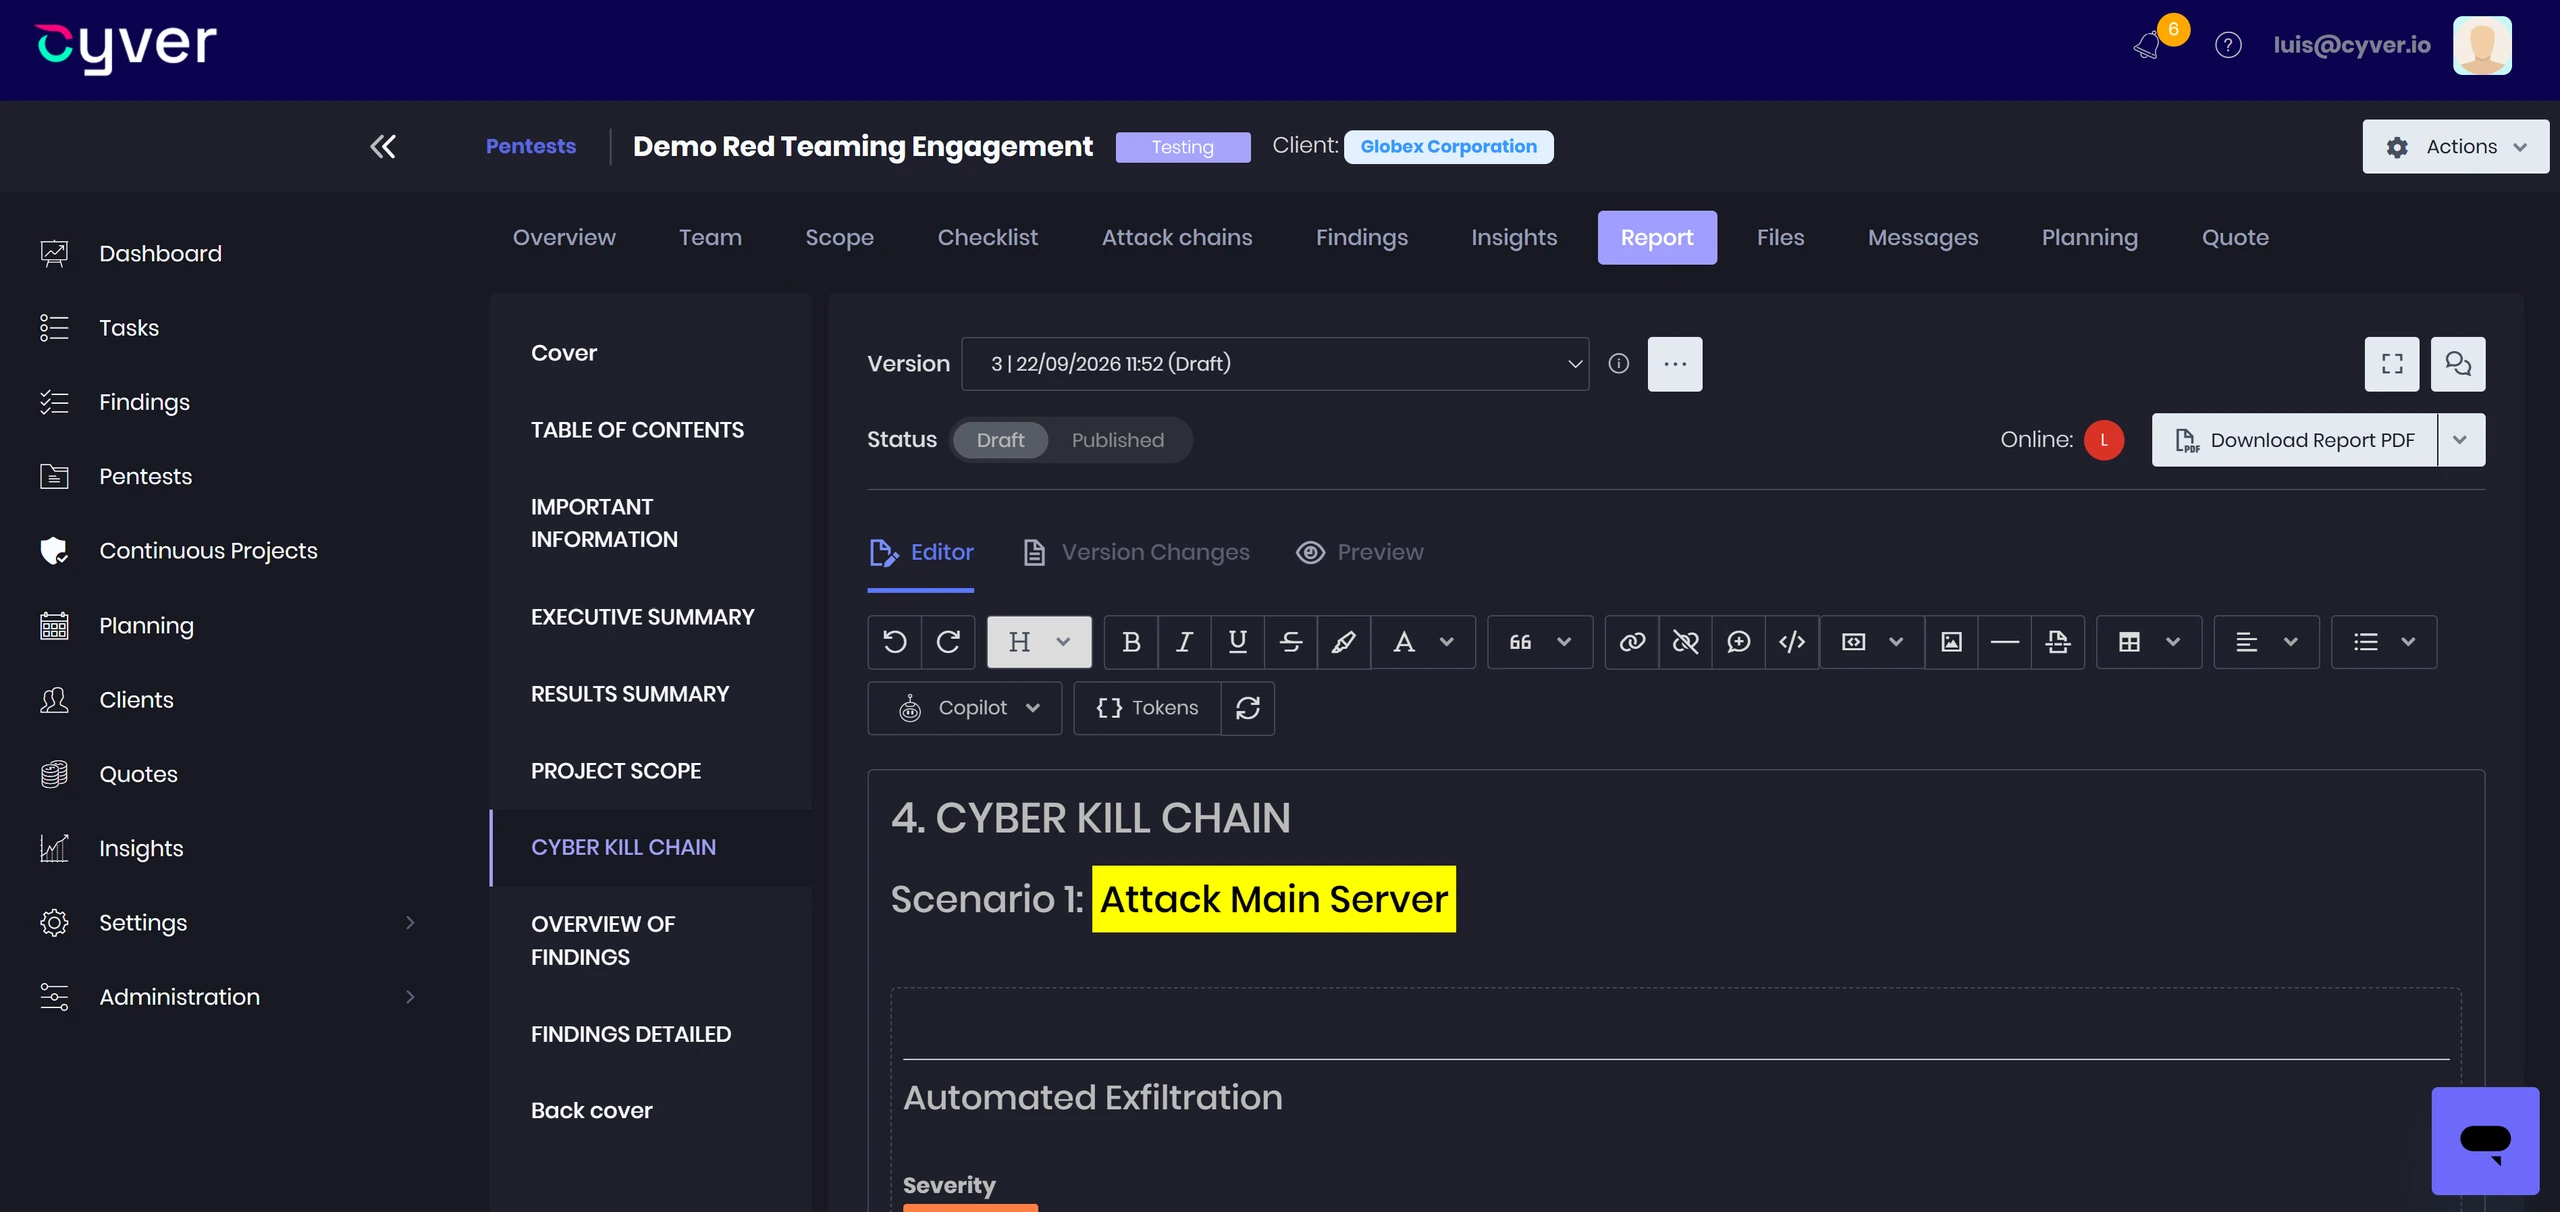
  • Dynamic tokens – Populate reports with project data, findings, and attack chains.
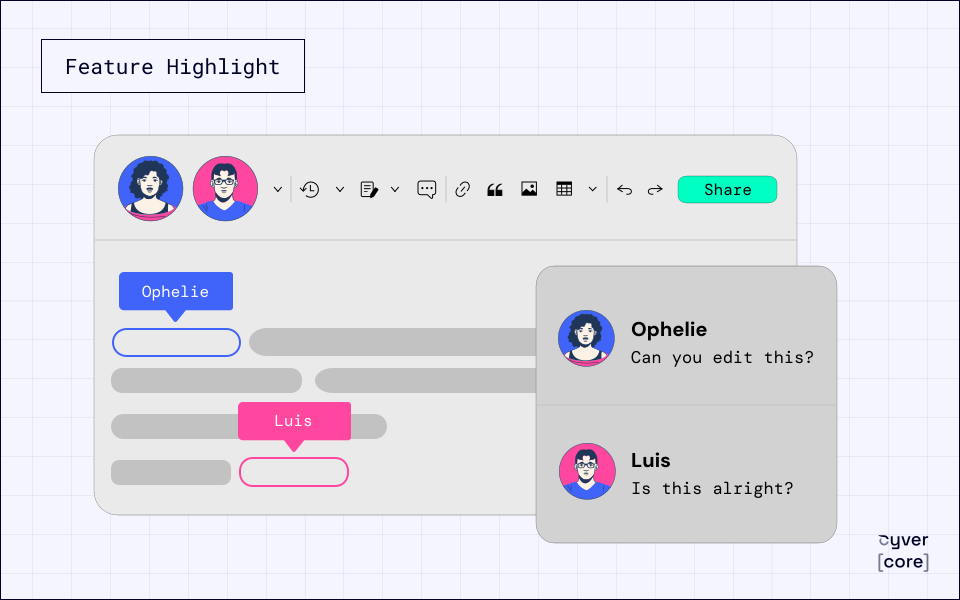
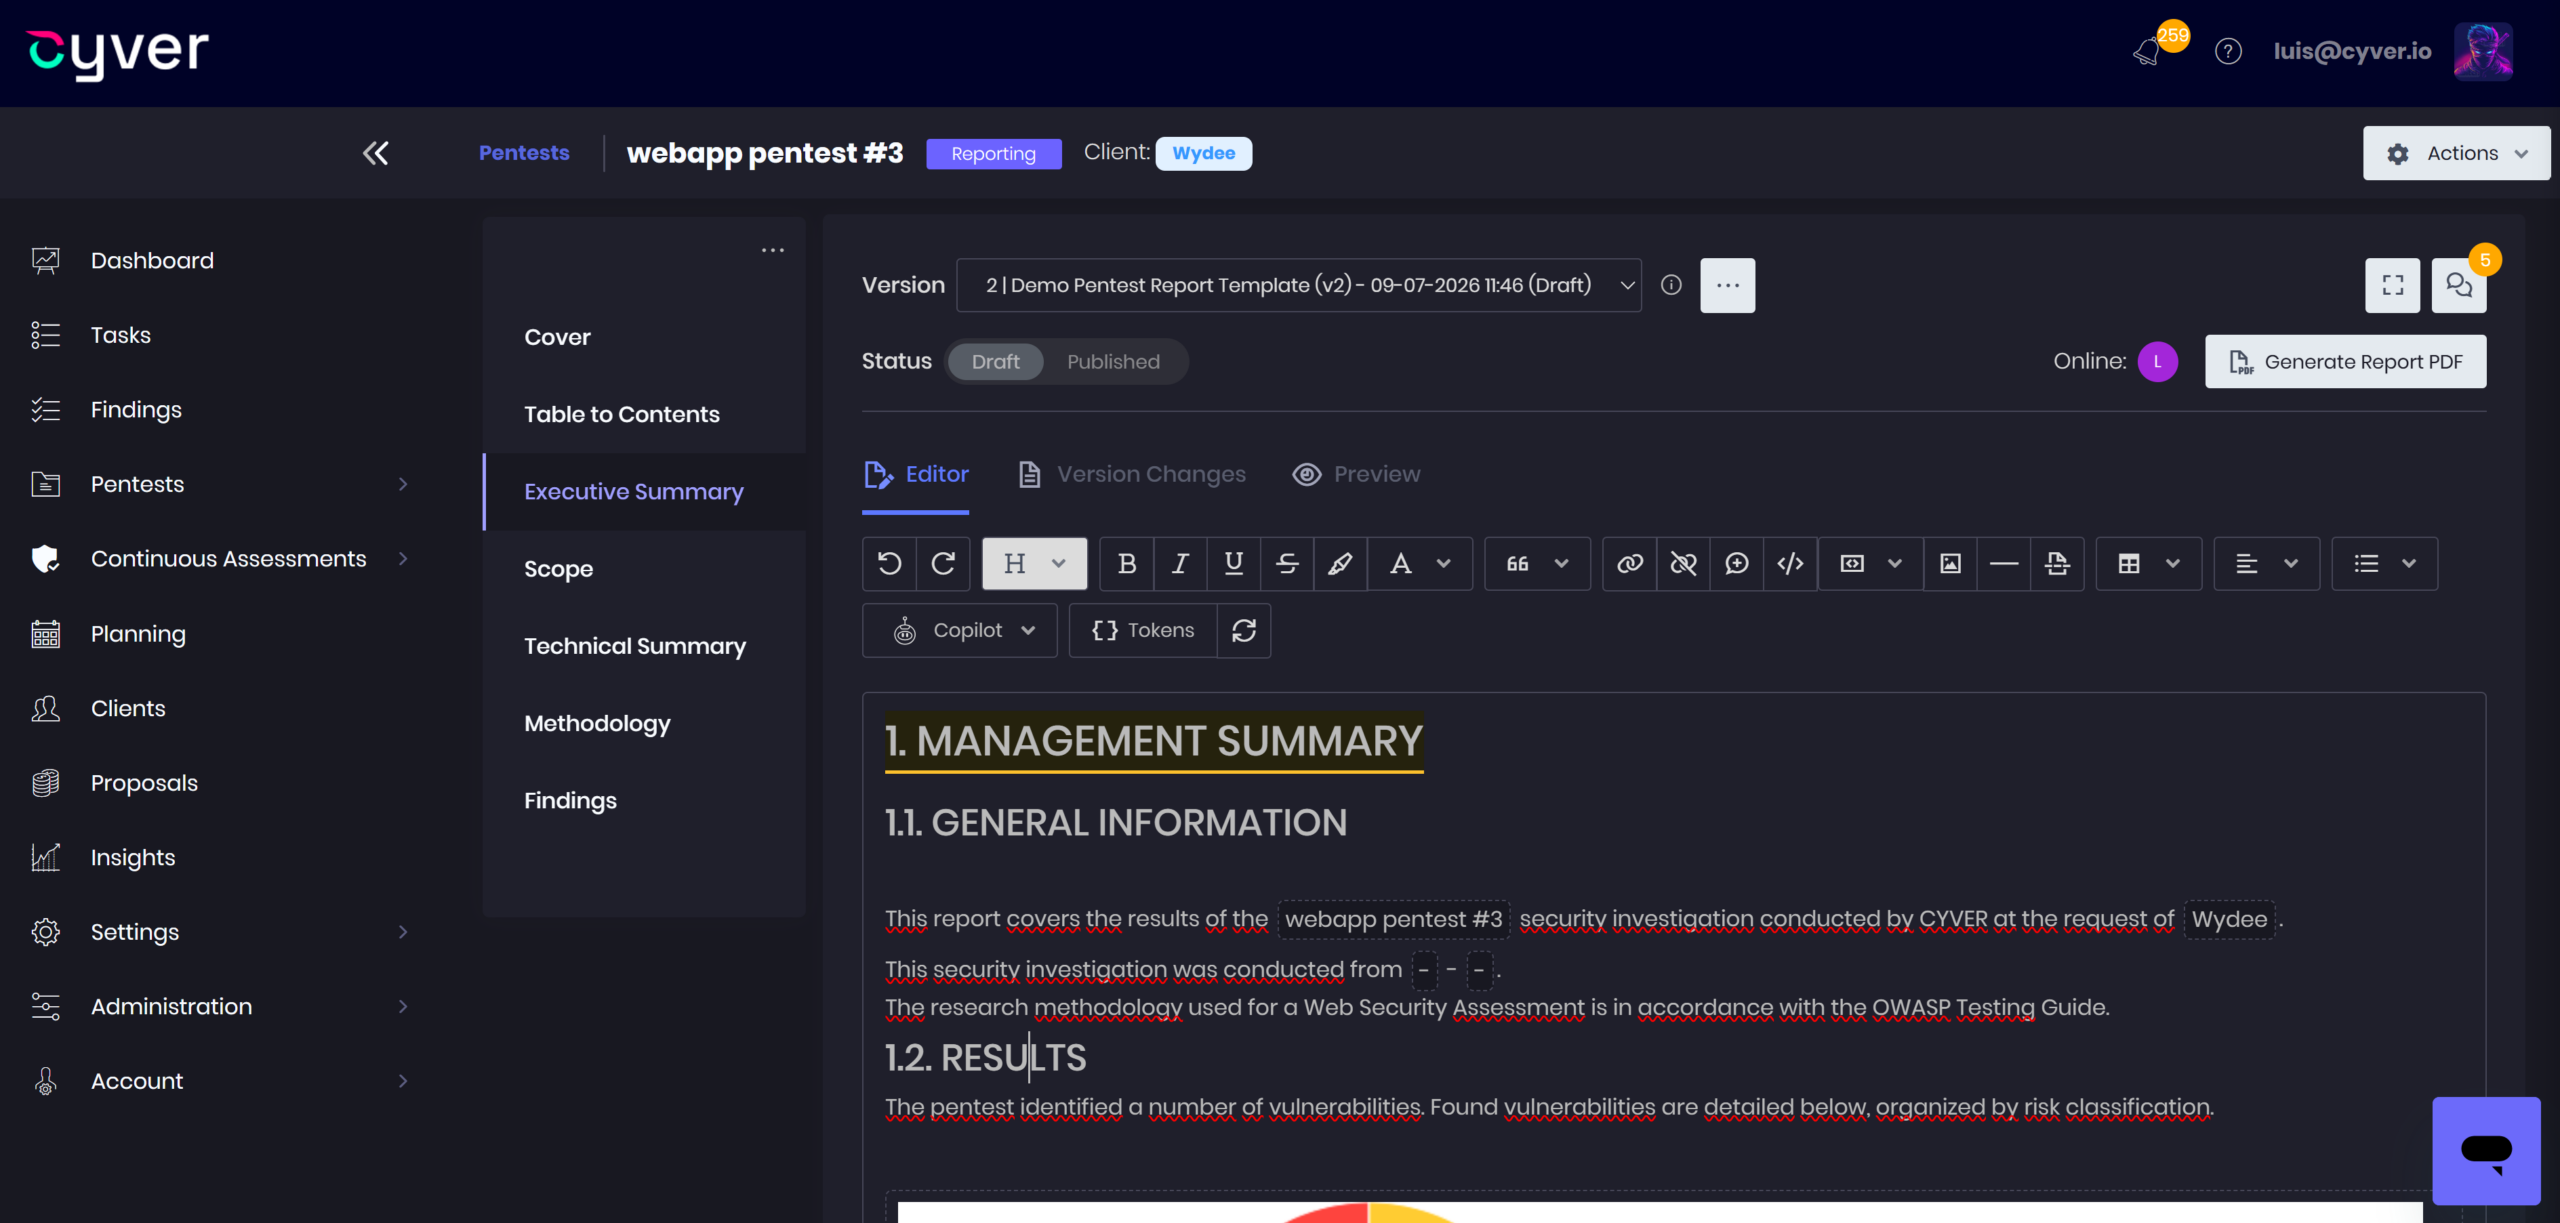
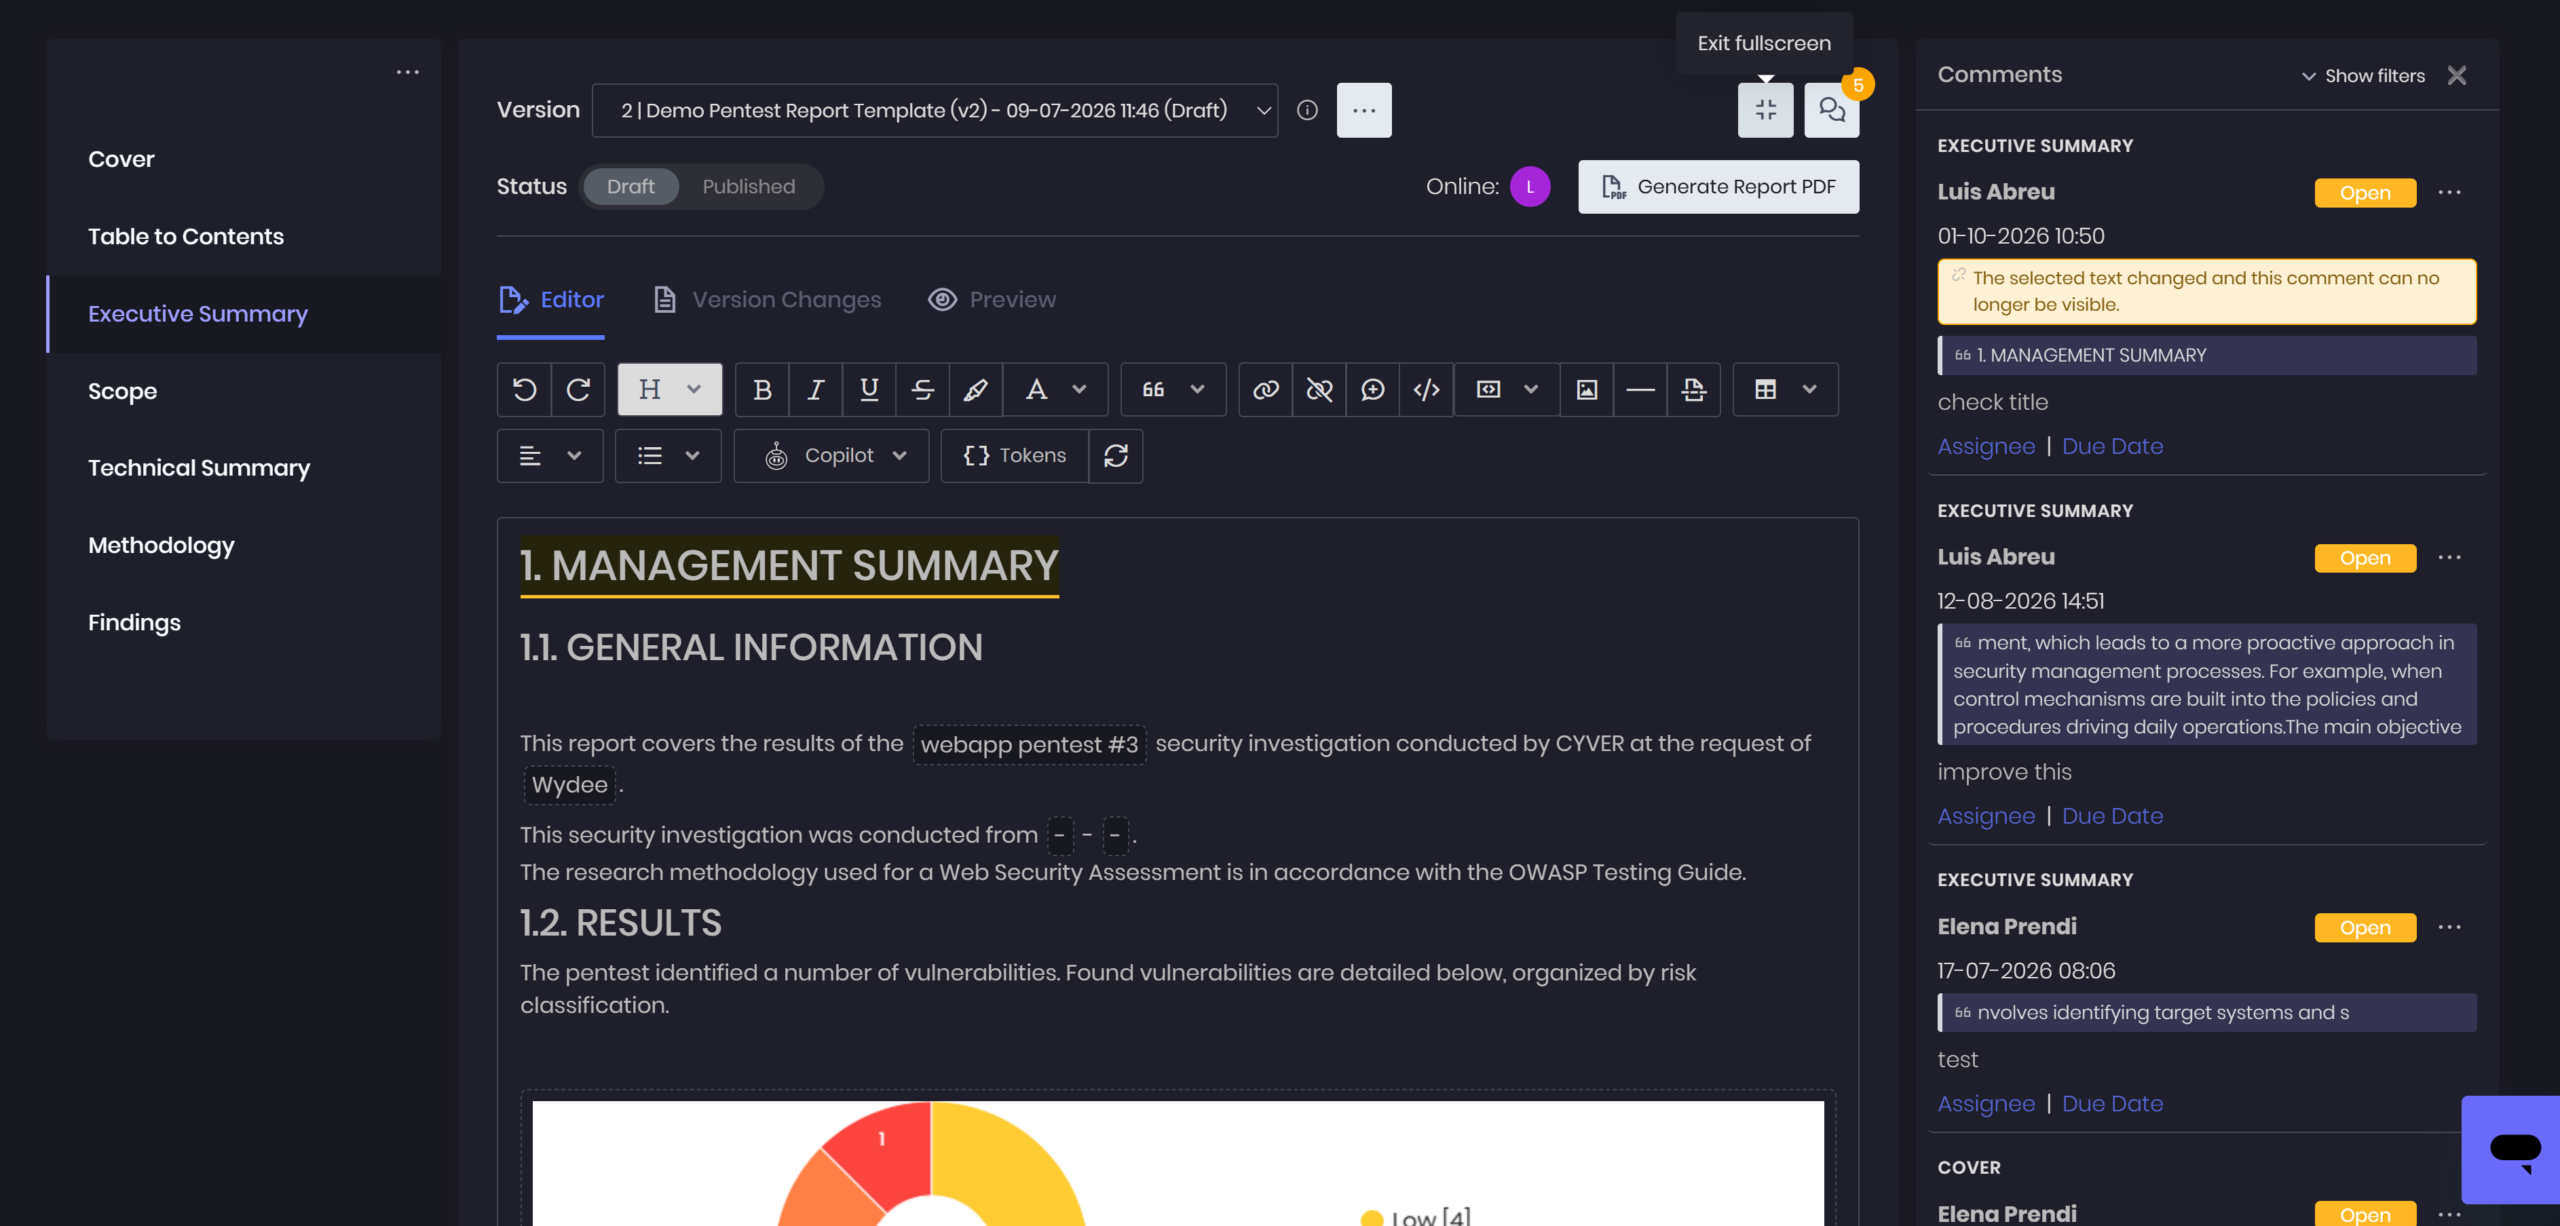
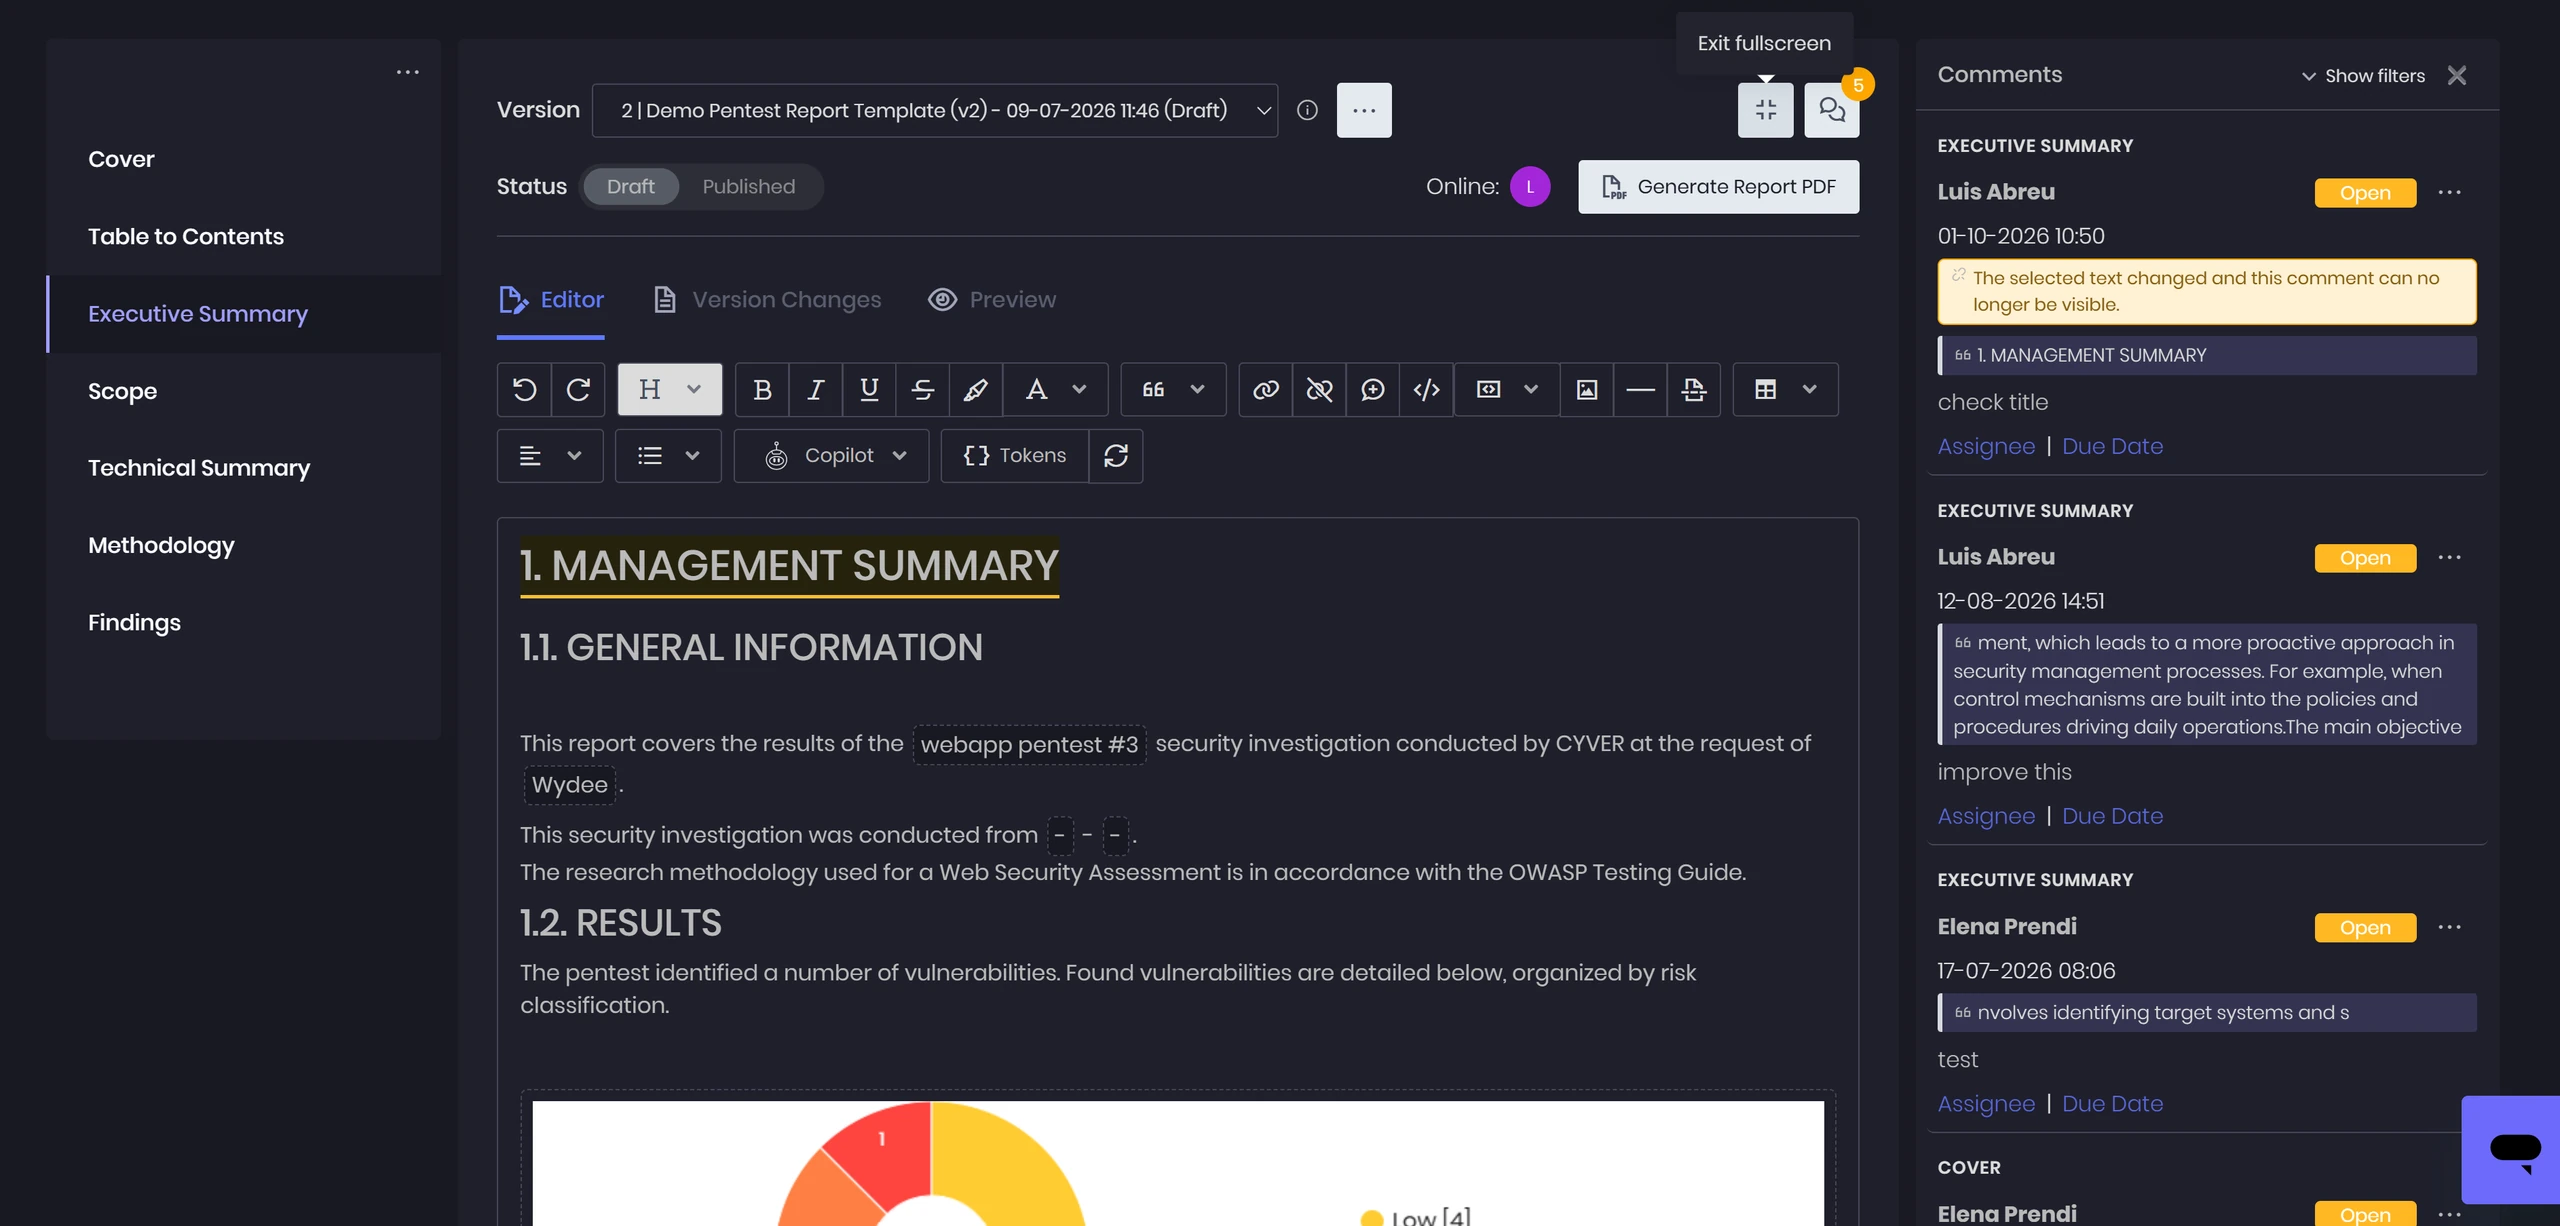
  • Collaborative editing – Write together with review comments and version history.
  • AI assistance – Draft and refine findings and executive summaries.
  • Report delivery – Generate PDF, Word, or HTML reports and share through your portal.

5. Remediation and Continuous Improvement Braces Content

Track, validate, and improve security over time.

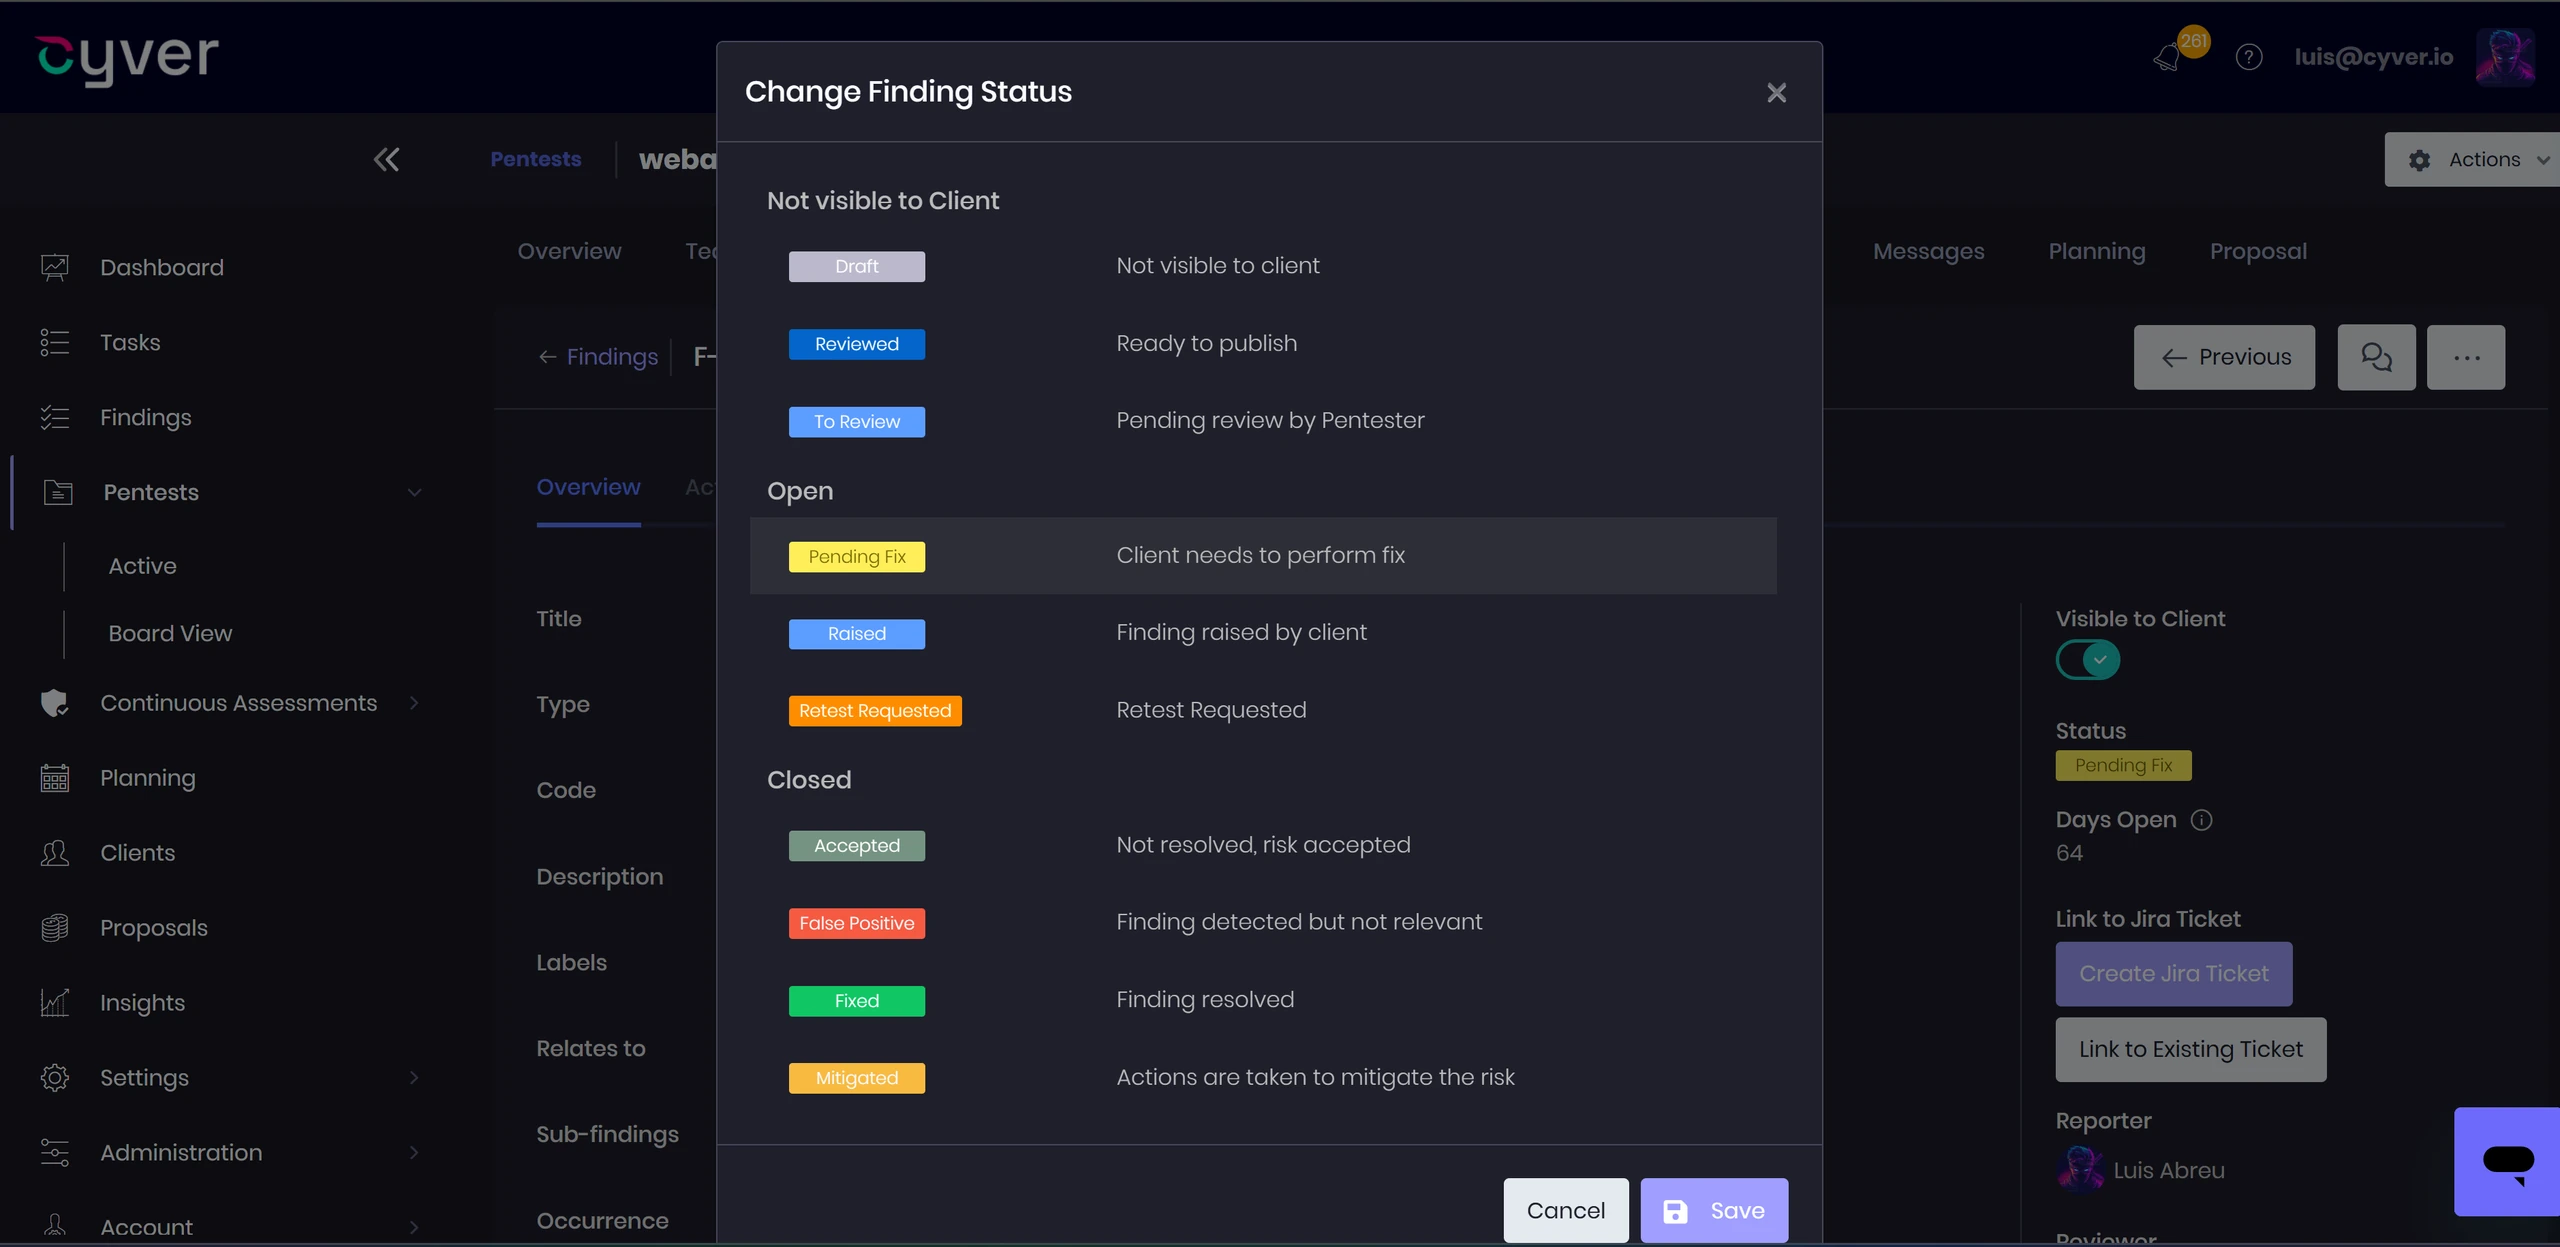
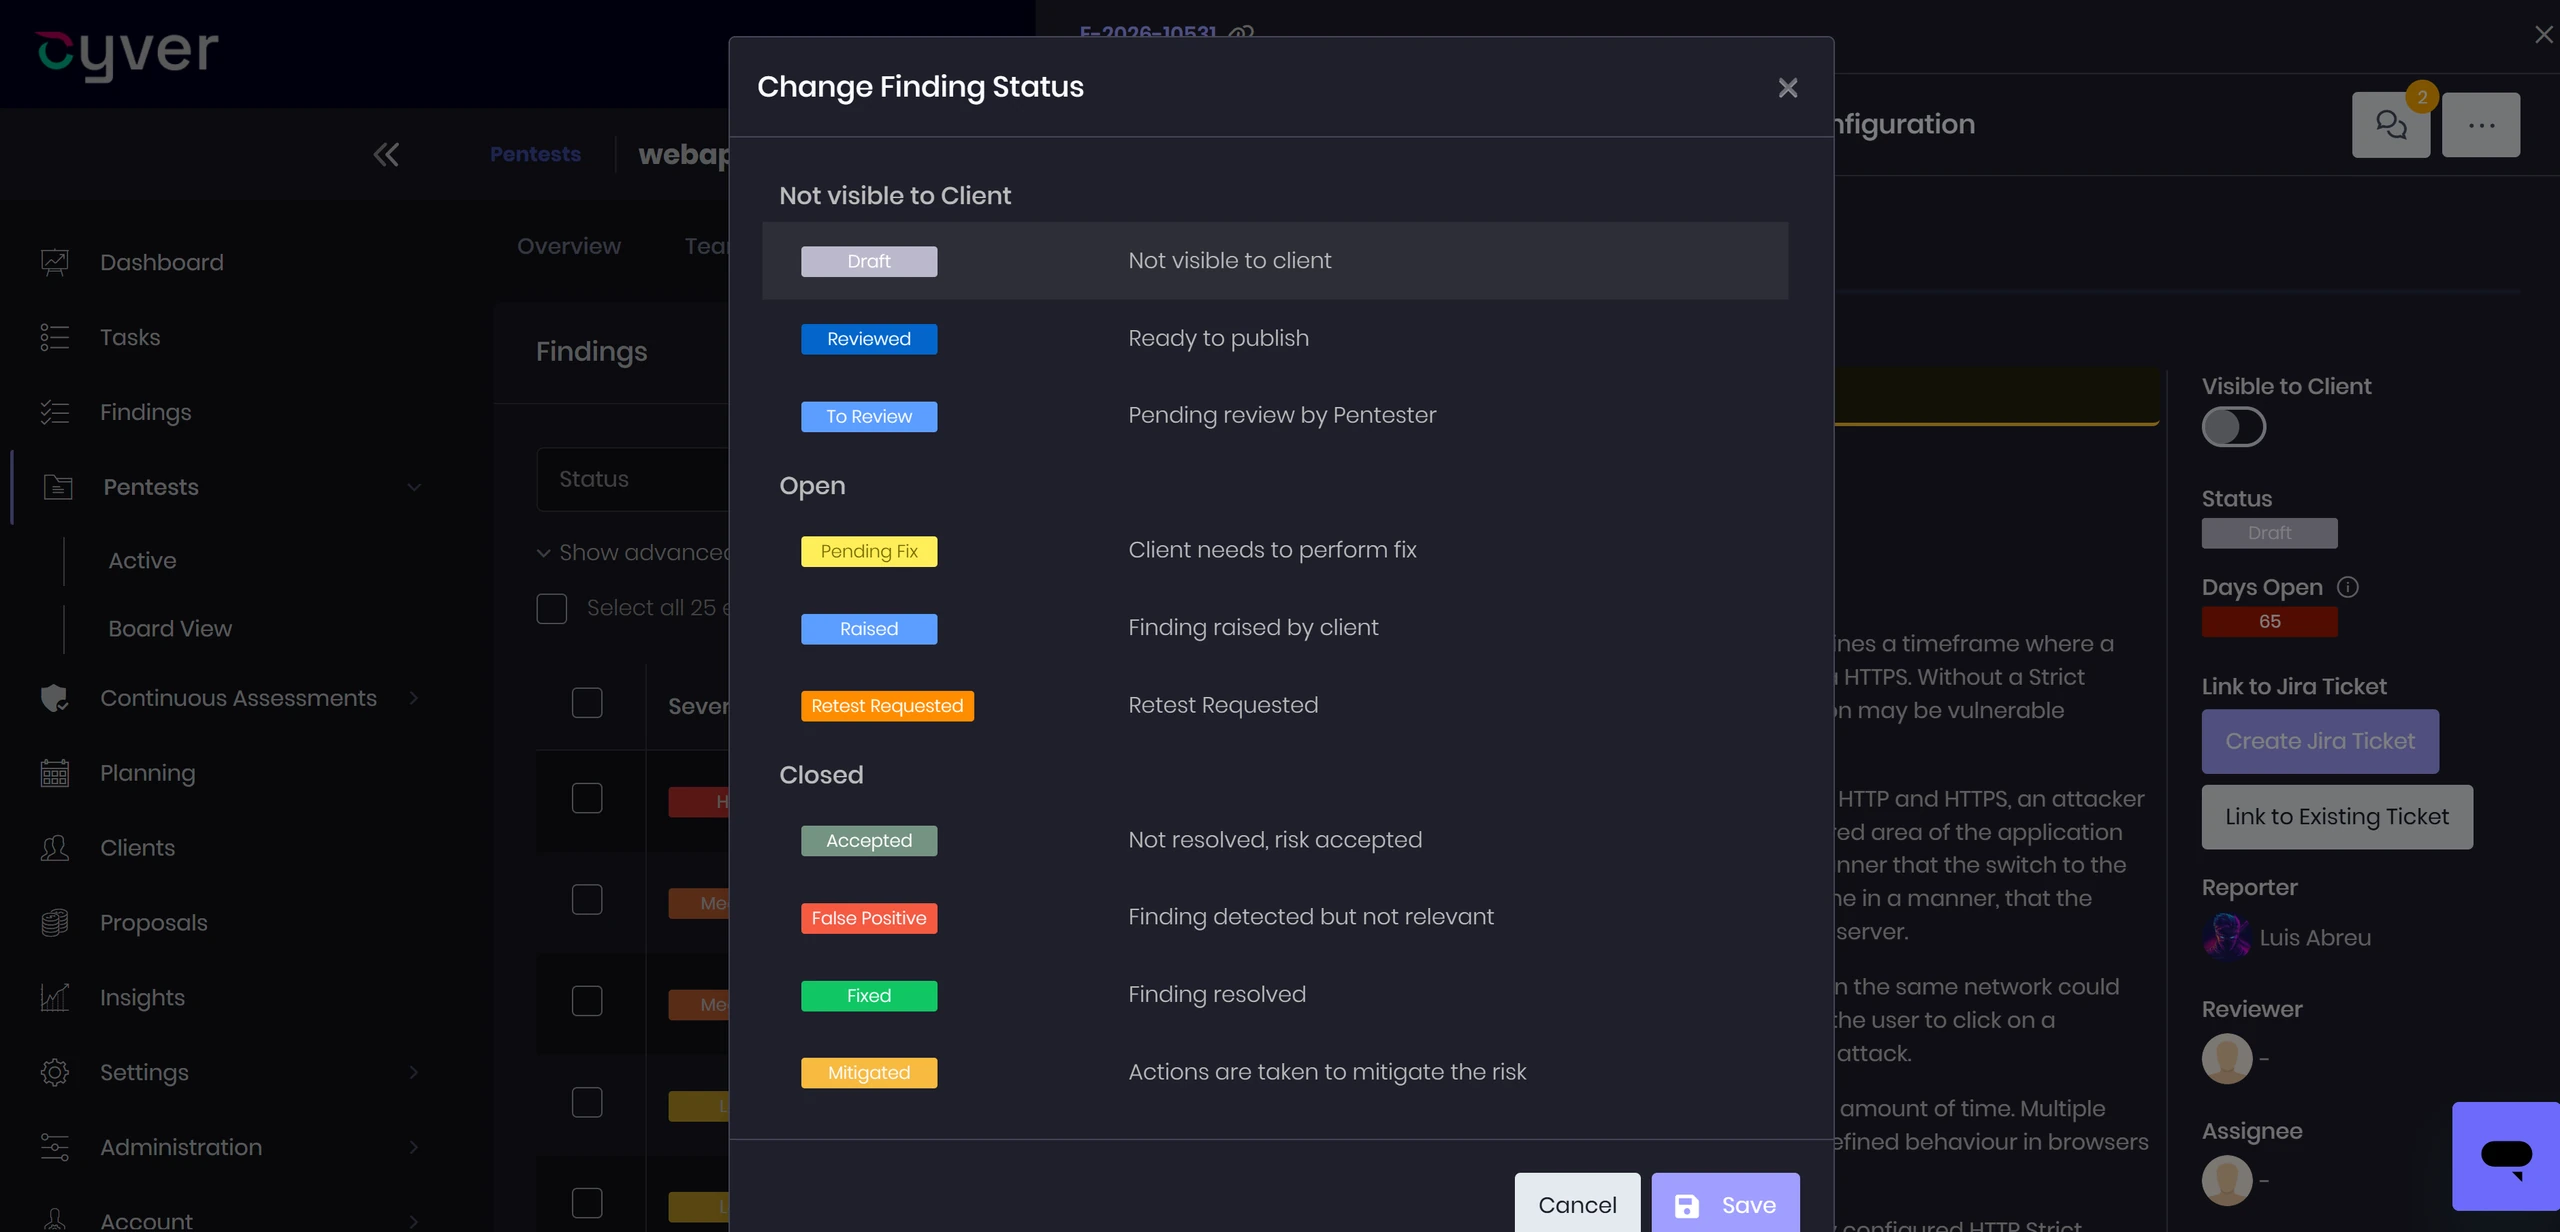
  • Remediation tracking – Monitor finding statuses and remediation SLAs.
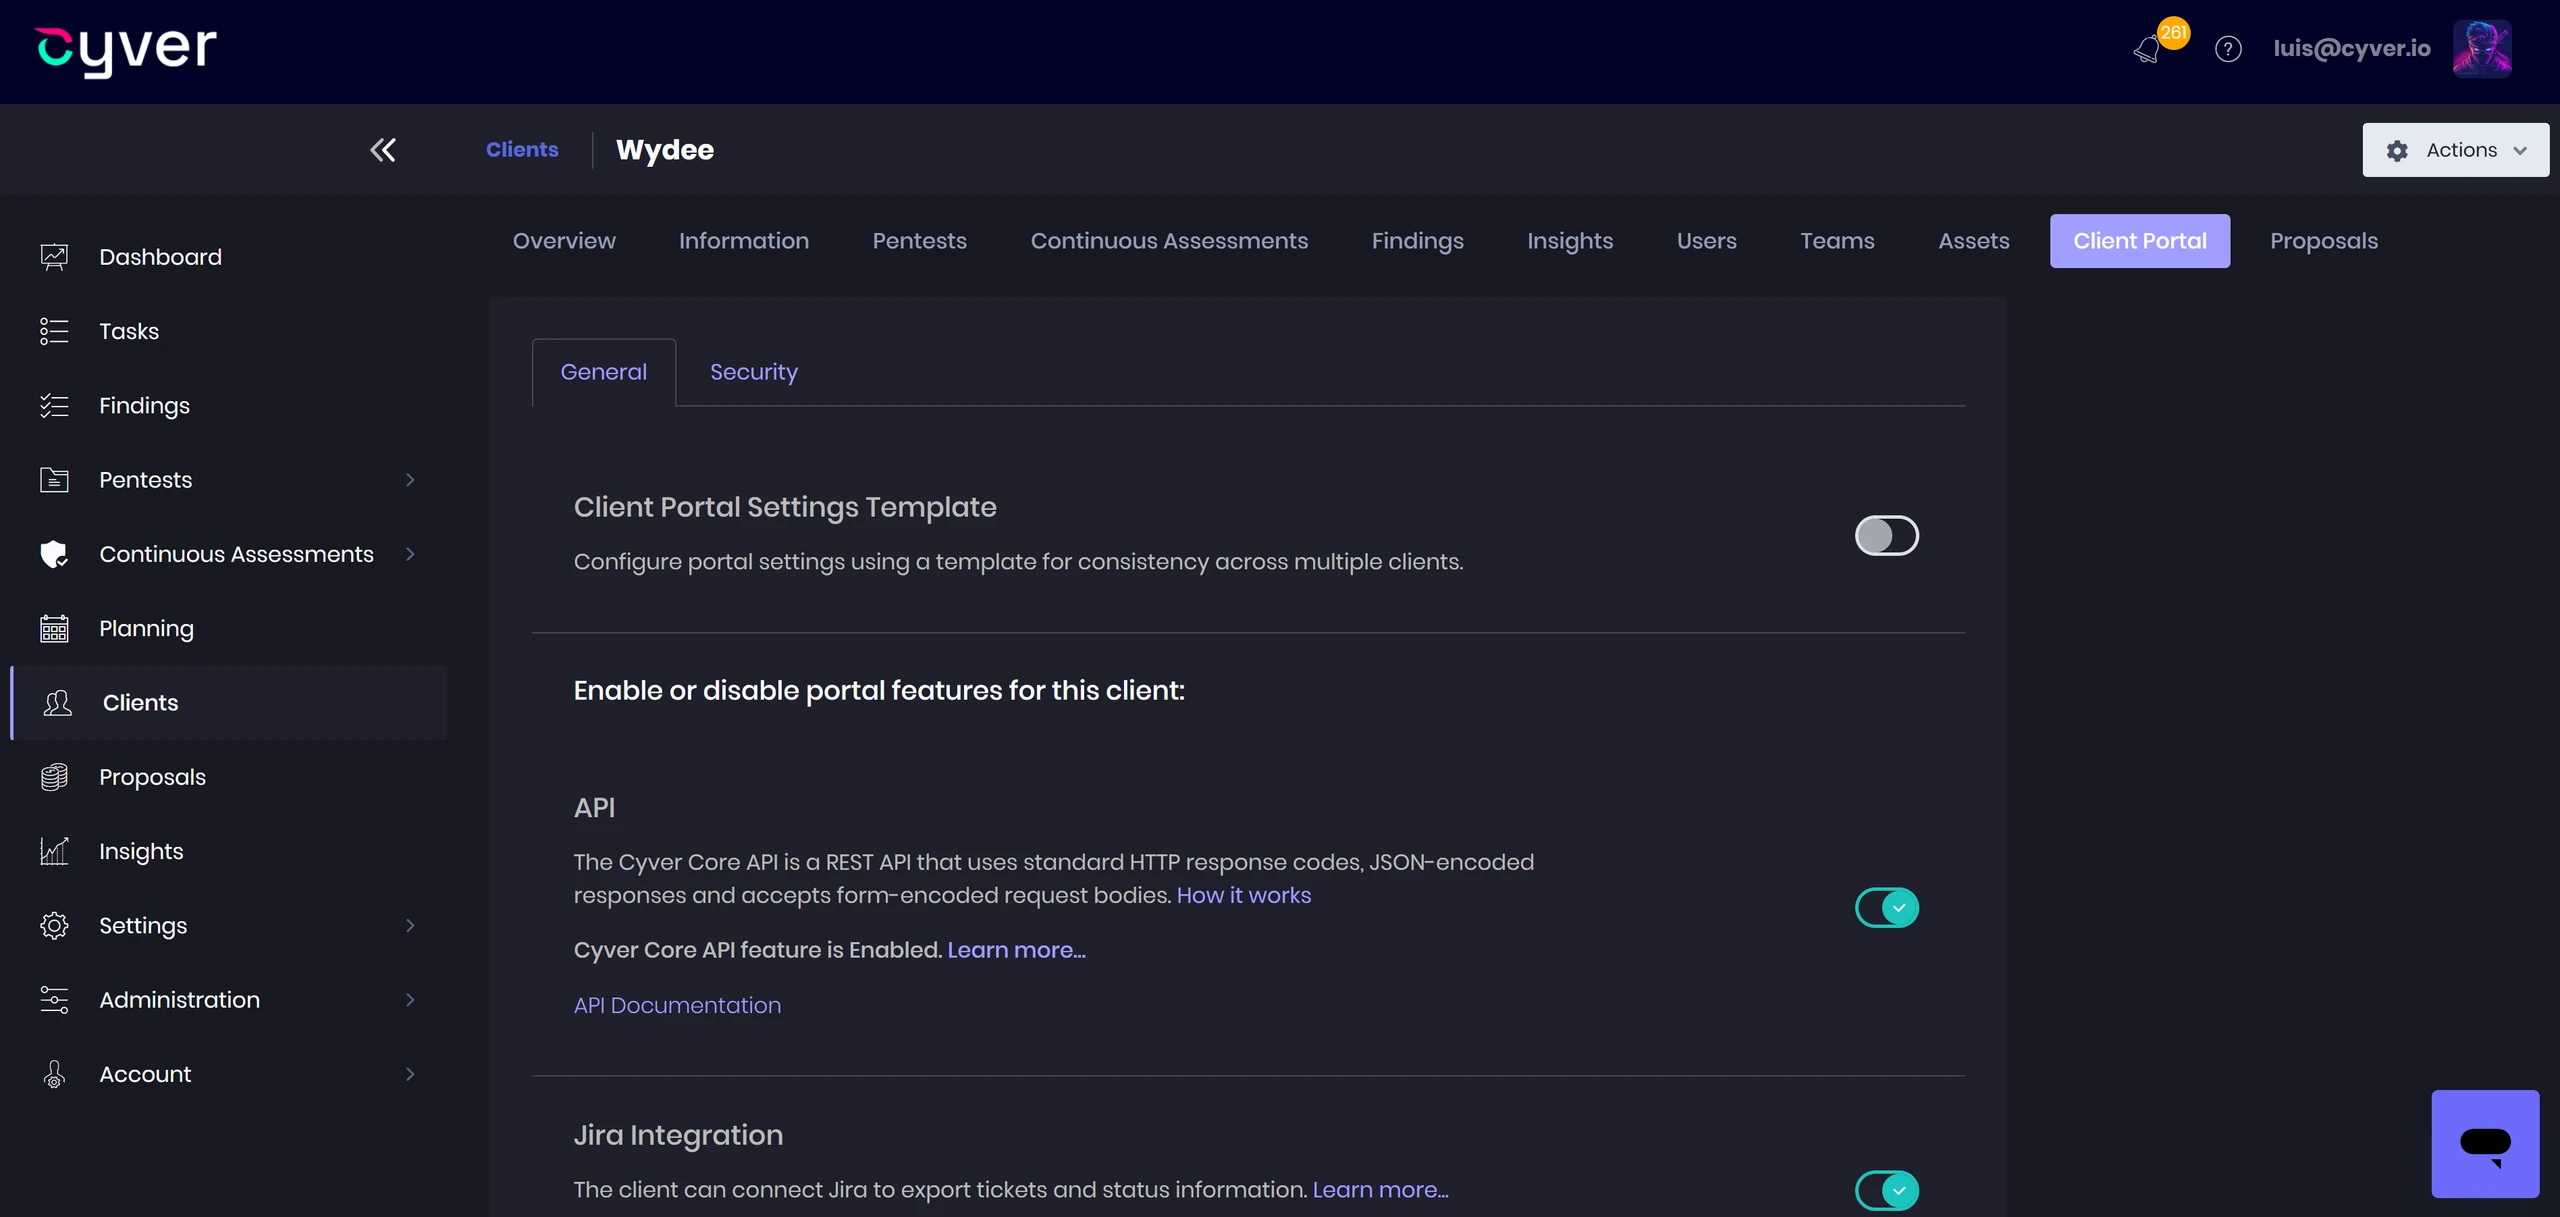
  • Ticketing integrations – Connect findings with Jira, Azure DevOps, and other tools.
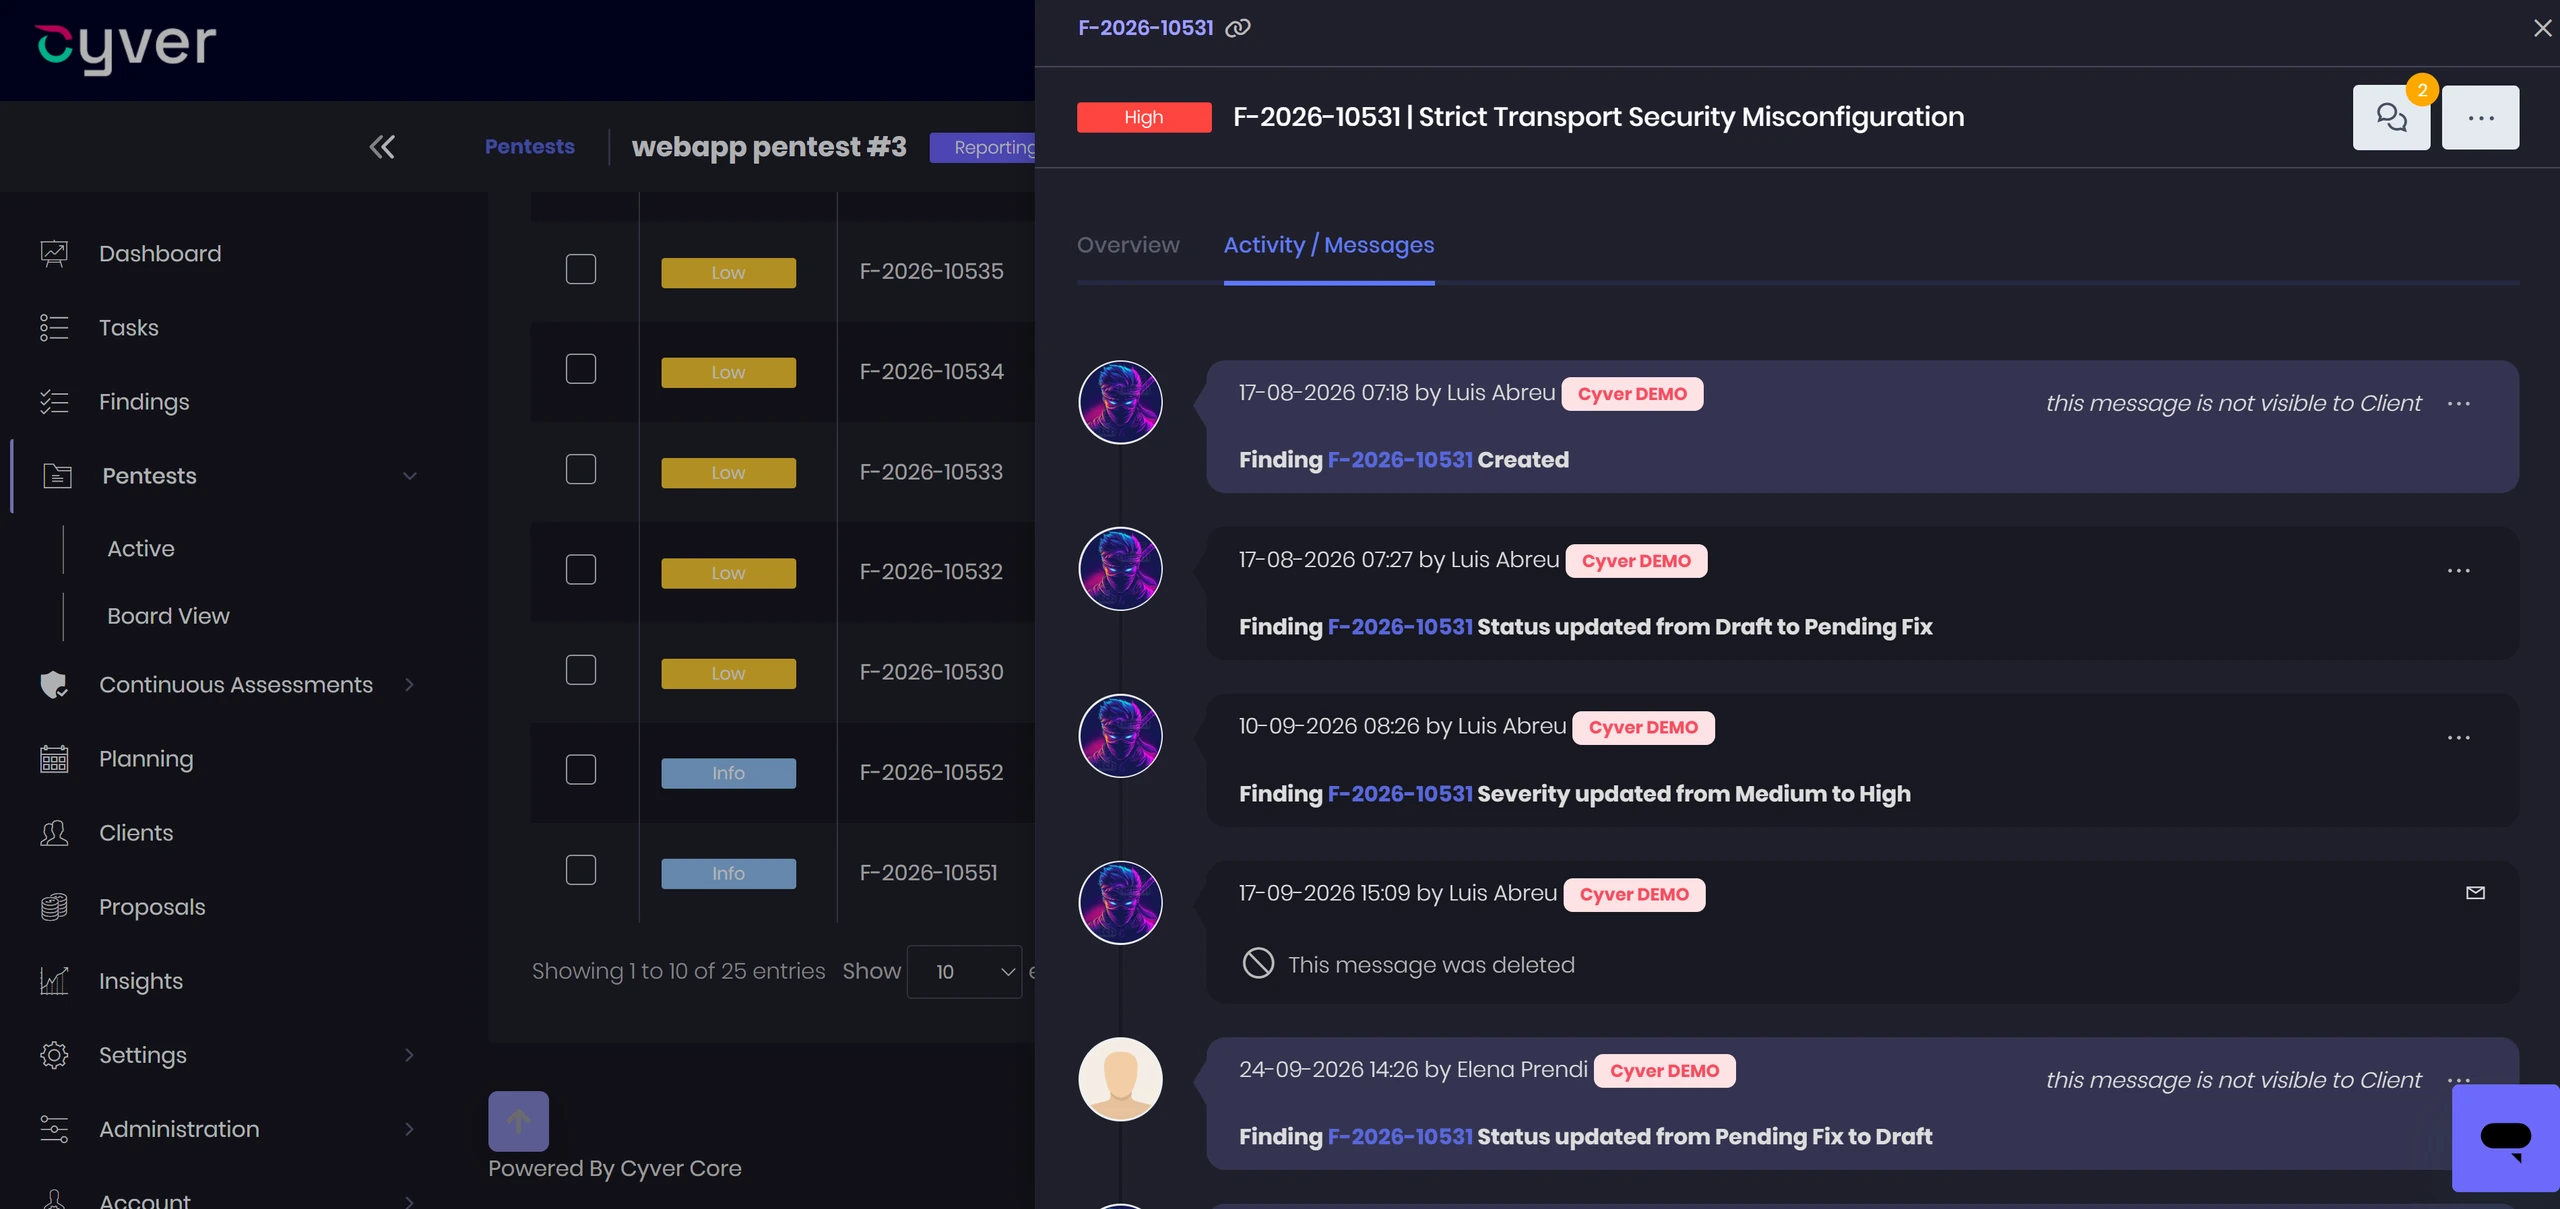
  • Client collaboration – Coordinate updates, discussions, and retest requests.
  • Retesting – Verify fixes and record evidence and outcomes.
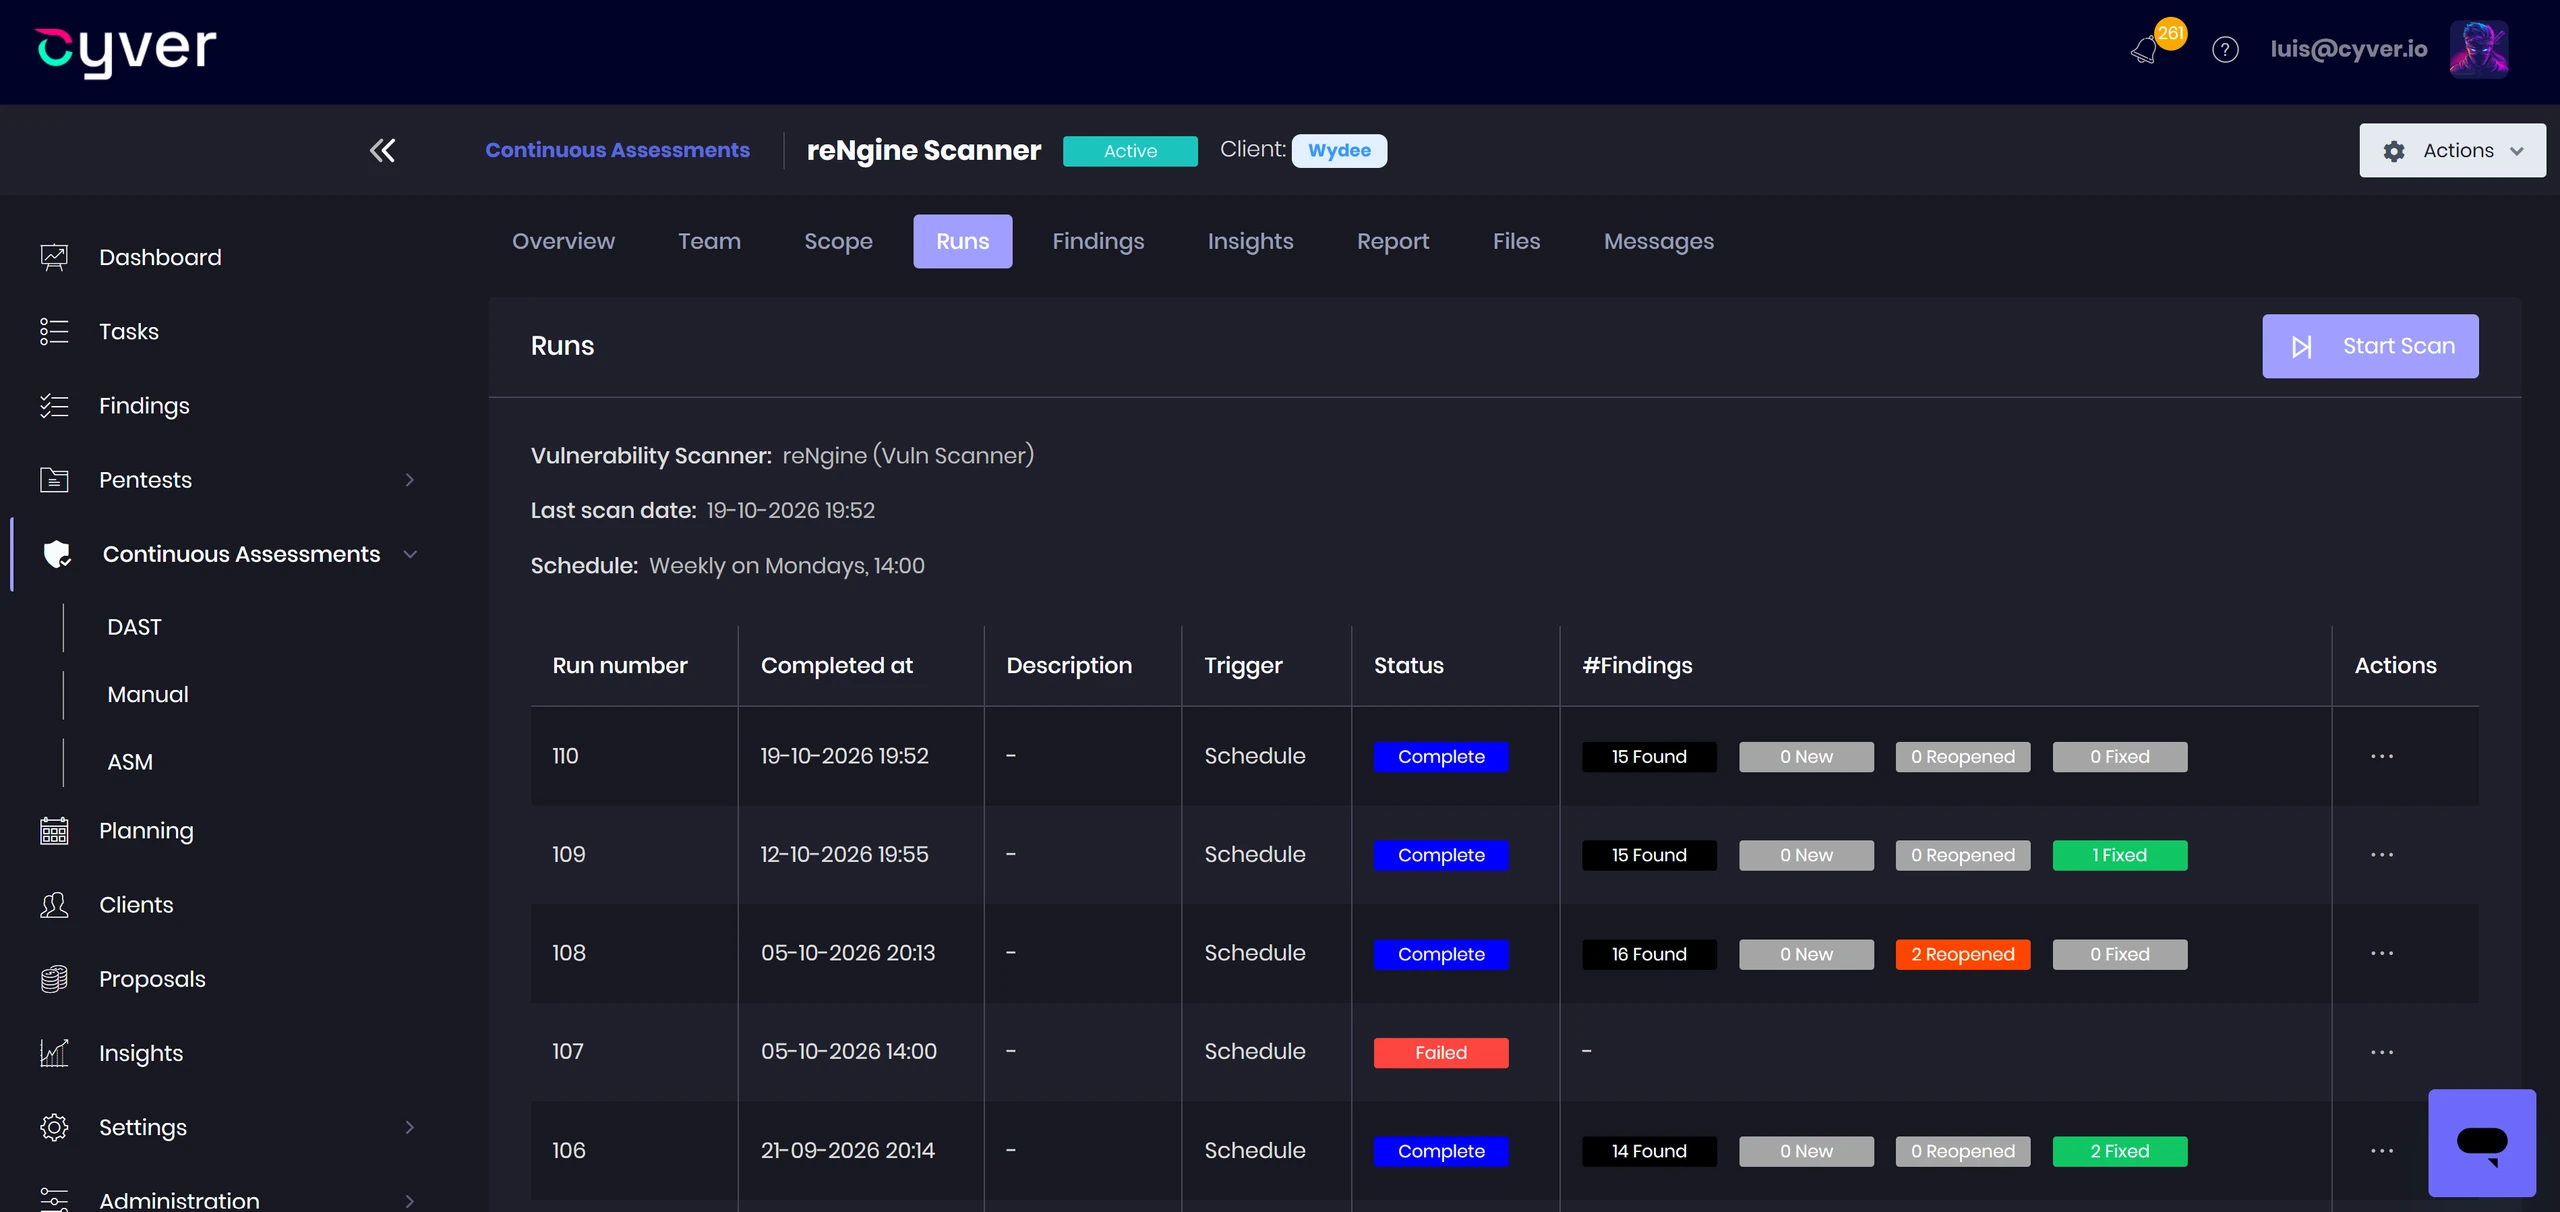
  • Continuous assessment – Track testing runs, recurring findings, and remediation trends.

One platform. Every workflow. From findings to client delivery.

Customer Centric

Getting Started in Days Braces Content

Not Weeks

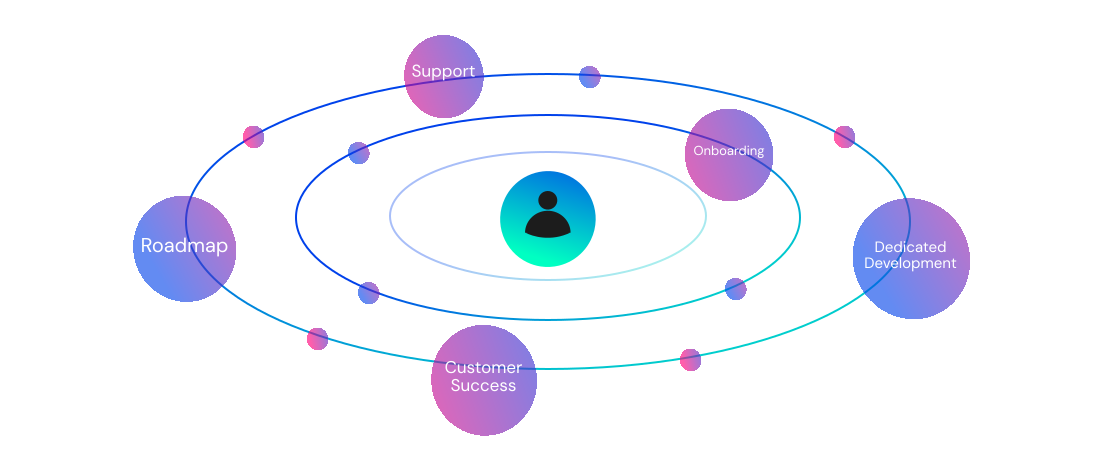
From quick onboarding and technical setup to roadmap collaboration and custom development, Cyver Core works alongside your team to support the way you operate and grow.

  • Onboarding Included
  • Data Migration
  • Report Template Migration
  • Premium Customer Support
  • Customer Success
  • Dedicated Development & Support
  • Community Roadmap
Integrations

Your Pentest = Your Tooling

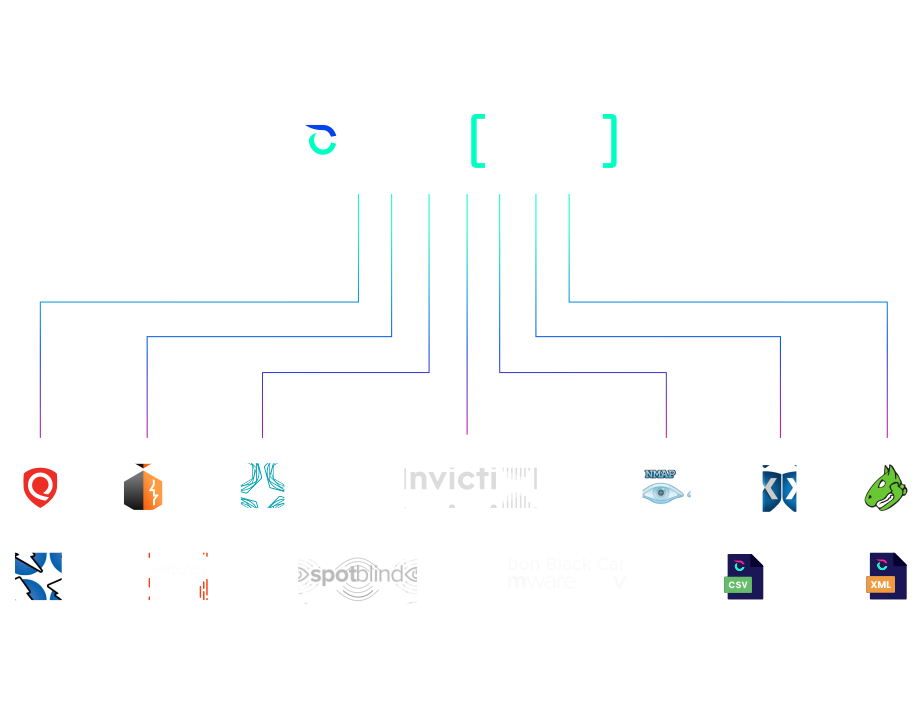
50+ Integrations. Your tooling, your methodology, your report, our platform. Don’t see your integration? Onboard, and we’ll build it for you!
Core Platform

The Core Platform Braces Content
to Support your Use Cases

Built for modern pentest teams, Cyver Core combines automation, integrations, security, and flexible deployment into one operational platform. Everything you need to run scalable offensive security workflows, connected in one place.
Core Platform
API
Hosting
AI
Security

Connecting Stakeholders

Connect all stakeholders with real-time workflows, dashboards, and notifications, no more fragmented communication.

Build Connectors with your Custom apps

Integrate Cyver with your ecosystem using events and webhooks to automate workflows across your tools.

Secure & Flexible Deployment

Deploy Cyver your way — cloud, private, or on-prem — with secure, scalable, and compliant hosting options.

AI-Powered Reporting

Generate reports, summaries, and writeups faster with AI — while keeping full control in your team’s hands.

Built for Trust

Enterprise-grade security designed to protect your data, privacy, and operations at every level.


Testimonials

Our Users Love
Cyver Core.
Check out why

Customers love Cyver Core! You will too!
Luciano Ciattaglia
“Cyver Core is amazing, we told Luis that when we were onboarded, it’s really useful and a much-needed tool for pentesters and auditors. A company like Hacken…
Luciano Ciattaglia
Director of Services, Hacken
☆☆☆☆☆
“Cyver Core is amazing, we told Luis that when we were onboarded, it’s really useful and a much-needed tool for pentesters and auditors. A company like Hacken, without a tool like Cyver, it’s just chaos.”
Luciano Ciattaglia
Luciano Ciattaglia
Director of Services, Hacken
Vratislav Pavel Skořepa
“At WardenSec, we started using Cyver Core software a year ago and it has been the best investment we have made since we started our business. The task…
Vratislav Pavel Skořepa
Founder and Managing Director, WardenSec
☆☆☆☆☆
“At WardenSec, we started using Cyver Core software a year ago and it has been the best investment we have made since we started our business. The task checklists cover every pentesting framework imaginable and help us manage our team effectively. The average reporting time has been reduced by 70% thanks to the comprehensive findings library. We are now able to focus on what we do best – pentesting – rather than reporting.”
Vratislav Pavel Skořepa
Founder and Managing Director, WardenSec
Miguel Santos
“We want our clients to be sure we are always there for them, whenever they need a pentest. Cyver helps us a lot with delivering this kind of…
Miguel Santos
Offensive Security Unit Manager, Layer8
☆☆☆☆☆
“We want our clients to be sure we are always there for them, whenever they need a pentest. Cyver helps us a lot with delivering this kind of offering and is, without a doubt, adding value to our customers. It simplifies how we deliver; clients can now manage pentests and finding, and some of them had no way to do that before. Plus, it helps us cross sell other services that we also offer through Cyver.”
Miguel Santos
Miguel Santos
Offensive Security Unit Manager, Layer8
Scott Sailors
“Cyver Core has finally allowed us to provide a continuous pentest model. We’ve been struggling with that and working to provide the best value with testing and the next…
Scott Sailors
AlphaONE Operations
☆☆☆☆☆
“Cyver Core has finally allowed us to provide a continuous pentest model. We’ve been struggling with that and working to provide the best value with testing and the next step was to build a dashboard to deliver customer interaction. With Cyver Core, it’s all just there. The reporting is a little bit easier and more seamless; consistency is there, I’ve been very pleased overall and now we have that pentest-as-a-service product ready to go”
Scott Sailors
Scott Sailors
AlphaONE Operations
Seven Hiltrop
“Cyver Core adds a layer of automation like findings uploads to real-time collaboration, so I can easily scale pentesting to the client”
Seven Hiltrop
☆☆☆☆☆
“Cyver Core adds a layer of automation like findings uploads to real-time collaboration, so I can easily scale pentesting to the client”
Seven Hiltrop
Seven Hiltrop

Trusted By World Leading Cybersecurity Companies

 Whitepaper

Does Pentest Management Deliver ROI?

Download our free whitepaper to find out how pentest management platforms like Cyver Core reduce time expenditure on manual work, streamline communication, and bridge the gap between pentesting and the demand for digital services. It’s free and no obligation.
Any questions?

We’re here to help

What is a Pentest Management Platform?

Pentest Management Platforms like Cyver Core digitize pentest workflows, replacing manual communication and reports with digital workflows. It means real-time results, live communication with clients, and findings as tickets. Plus, we offer automated pentest reporting, complete with integrations for tools like Burp Suite, Nessus, NMap, & more. Our goal is to help pentesters save time (70-85% of time spent on every report), reduce overhead hours for pentest management, and deliver pentest-as-a-service to clients.

How is Cyver Core Secured?

Cyver Core is fully secured, regularly pentested, and regularly backed up. We maintain SOC2 compliant infrastructure, as verified by external auditors. All user data is stored redundantly and automatically backed up inside Microsoft Azure architecture, with fully redundant server architecture and network connectivity. We take security seriously, and you can see a full list of our security practices in our security policy.

Will My Clients See I Use Cyver Core?

No! Cyver Core is fully white label. When you onboard your clients to our platform, they see your branding and brand name. You can also fully customize reports, project templates, and other digital assets. Your clients, your brand, your digital privacy, powered by Cyver Core.

How Does Cyver Core Automate Workflows?

Cyver Core utilizes standardized workflows to automatically progress projects based on pre-defined parameters and settings. You set up project templates and Cyver Core automatically performs workflows inside those, to move the project from one stage to the next, to create Findings tickets from imported data, to notify stakeholders, and to schedule the next pentest. In addition, Cyver Core uses automation and Smart features to auto-fill tickets, to create projects, and to generate reports, so you have to do the minimum manual work possible. Visit our features page to learn more.
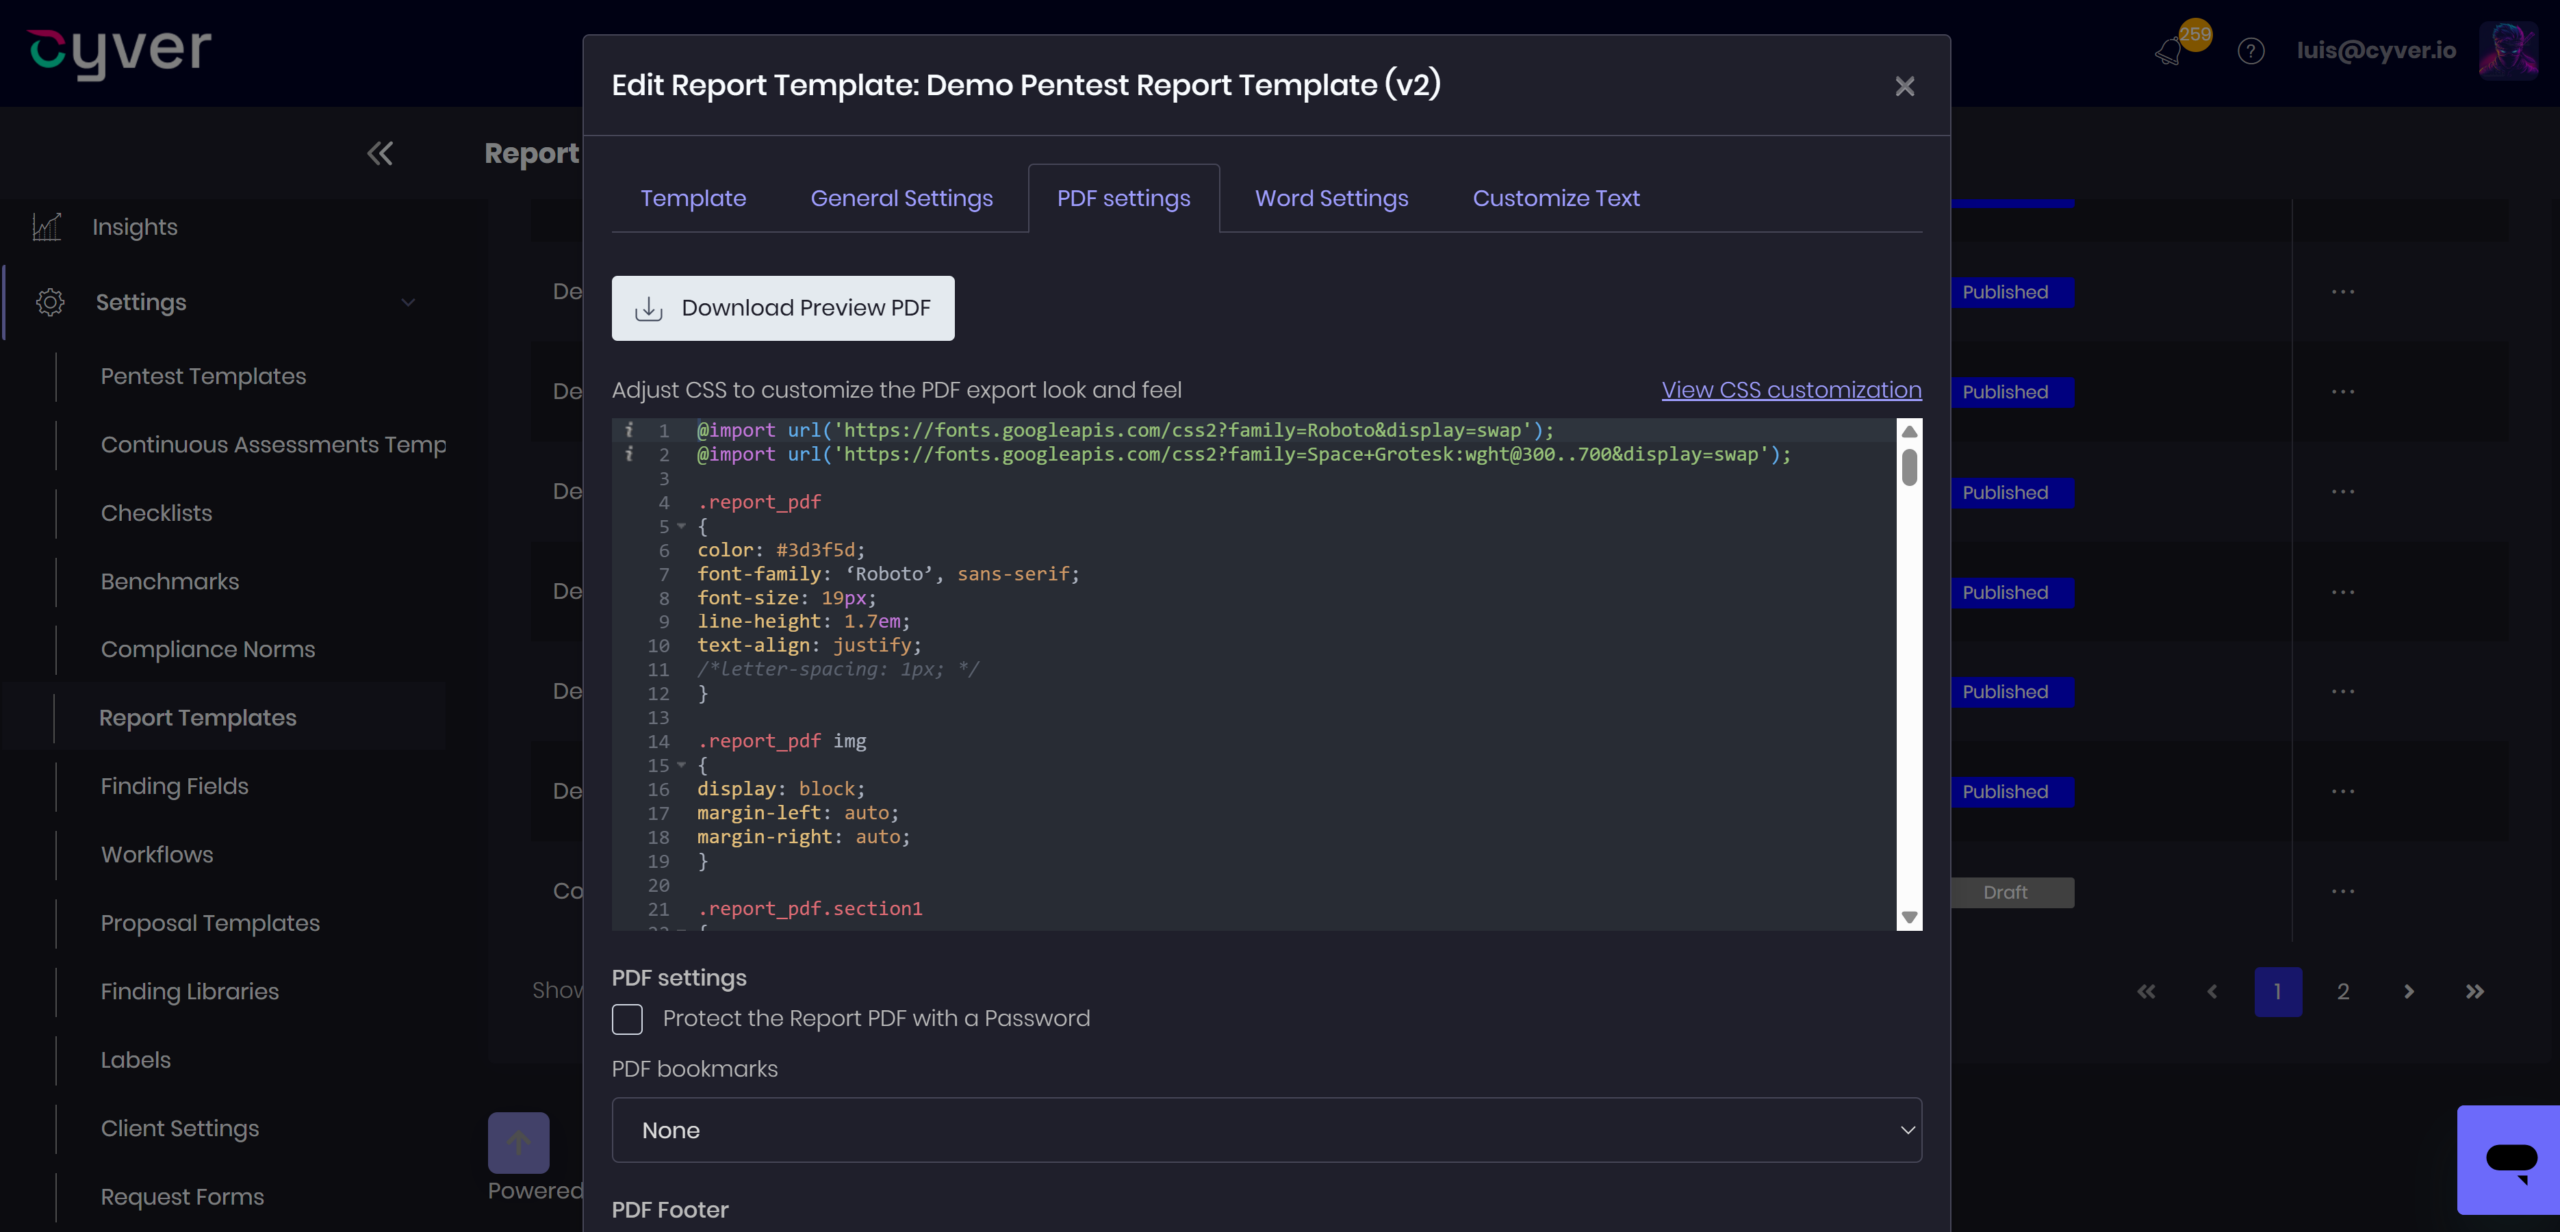
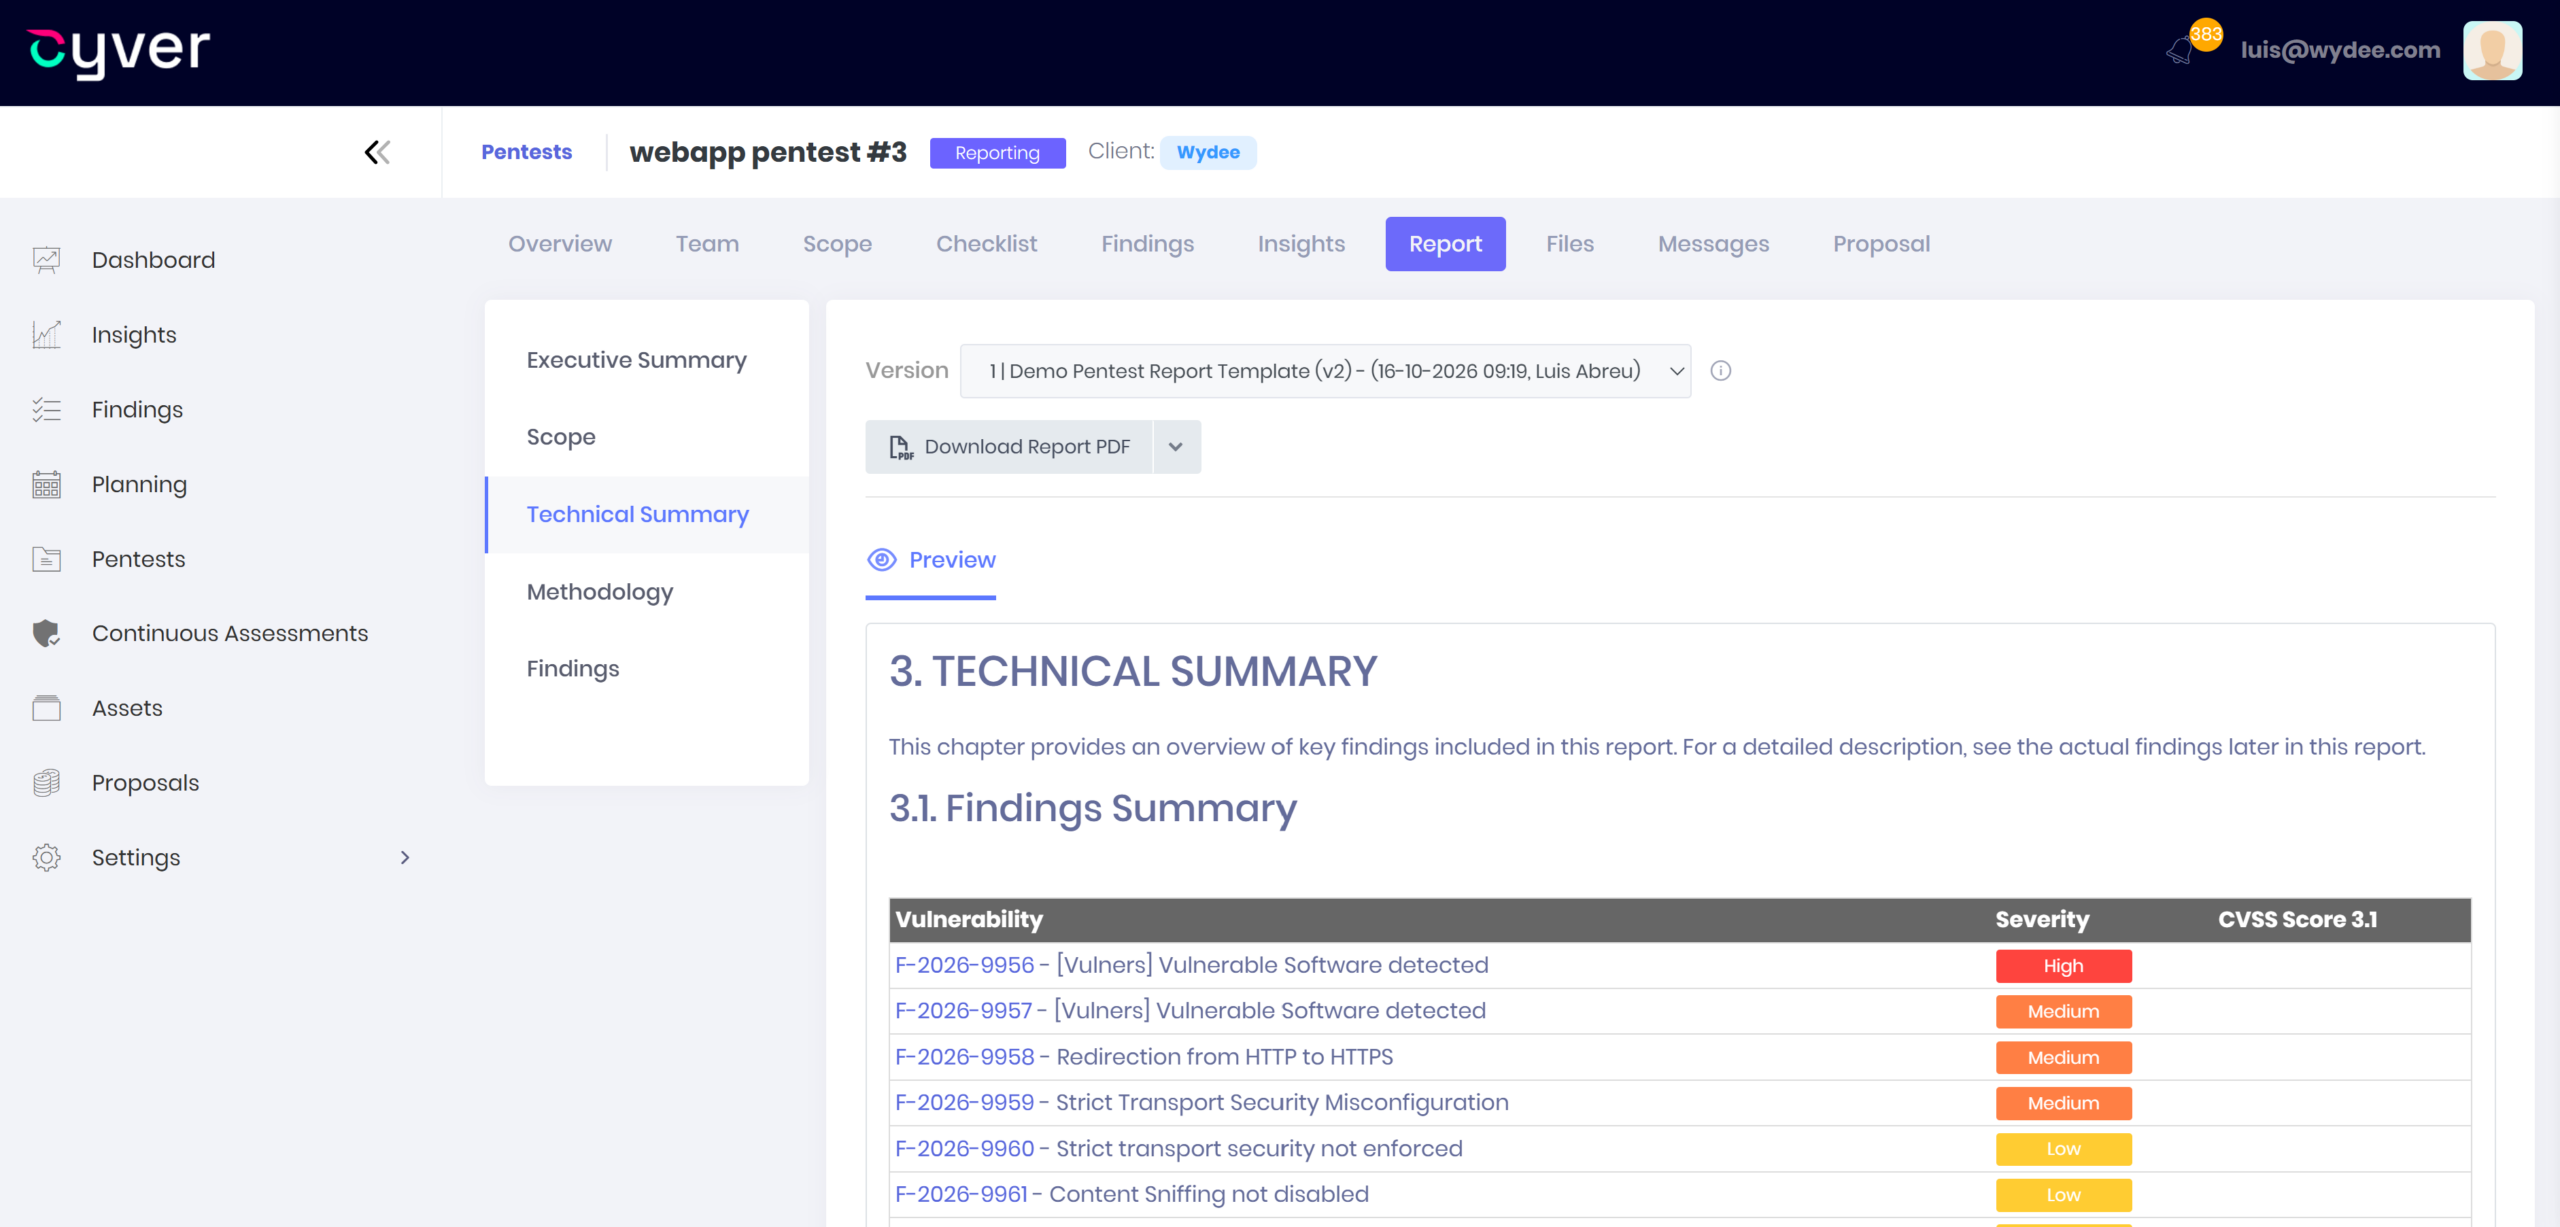
Report Template Management

Configure reusable report templates with custom branding, document structure, and dynamic tokens for project and client data.

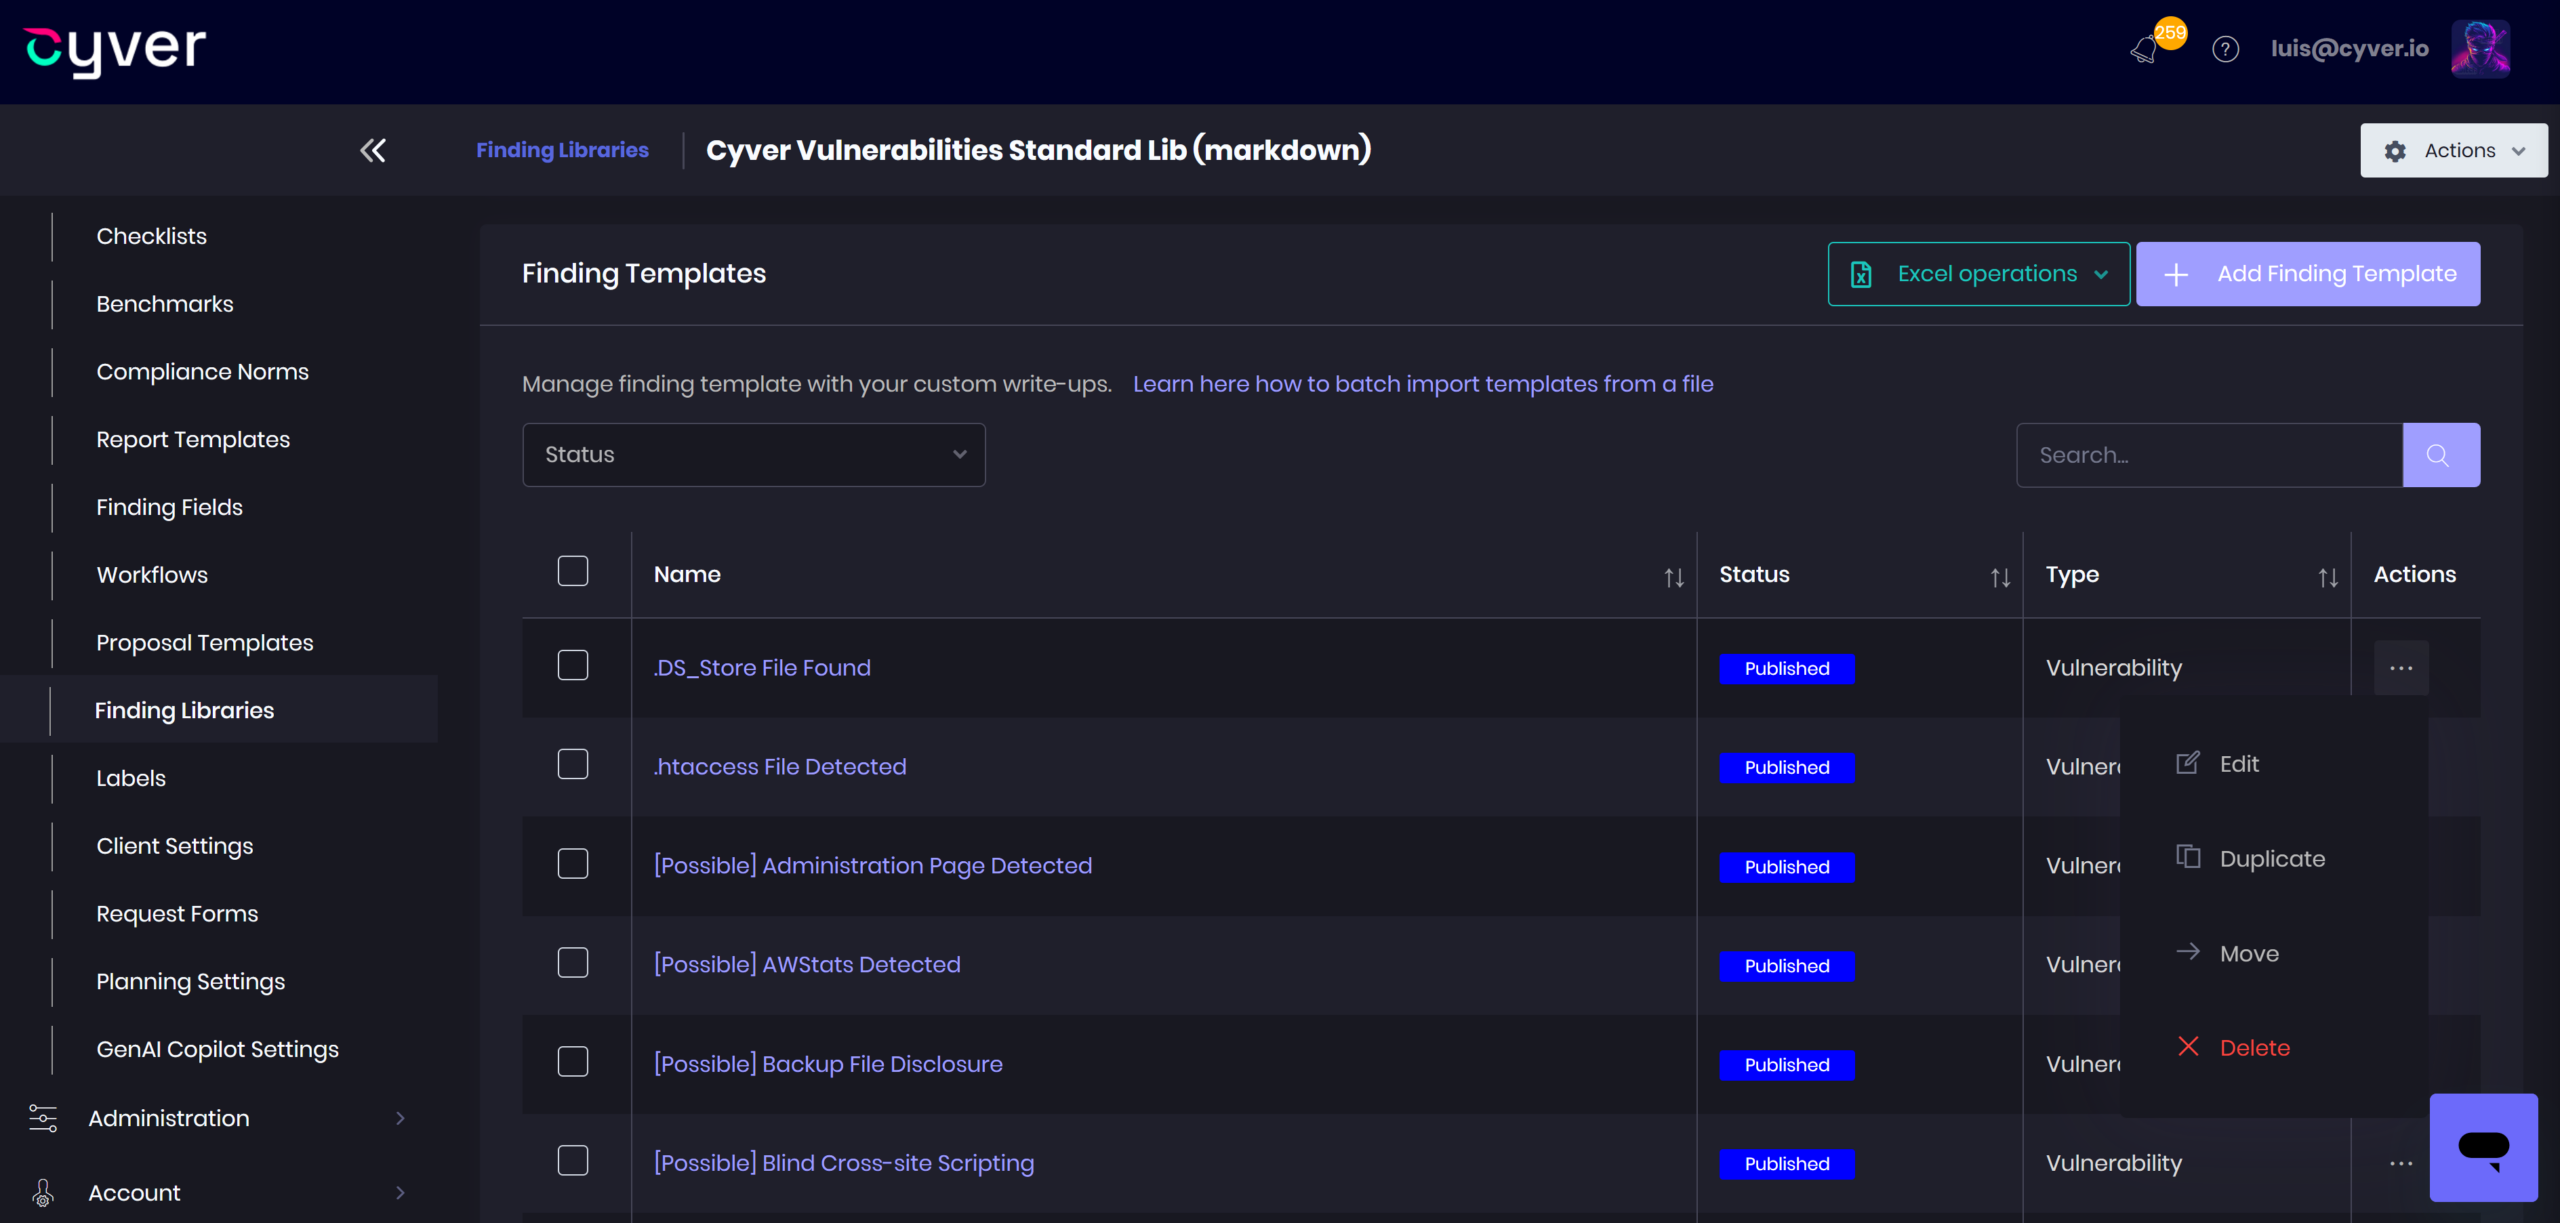
Finding Libraries

Maintain shared libraries of finding descriptions, risk assessments, and remediation guidance for reuse across pentest projects.

Finding Management and Scoring

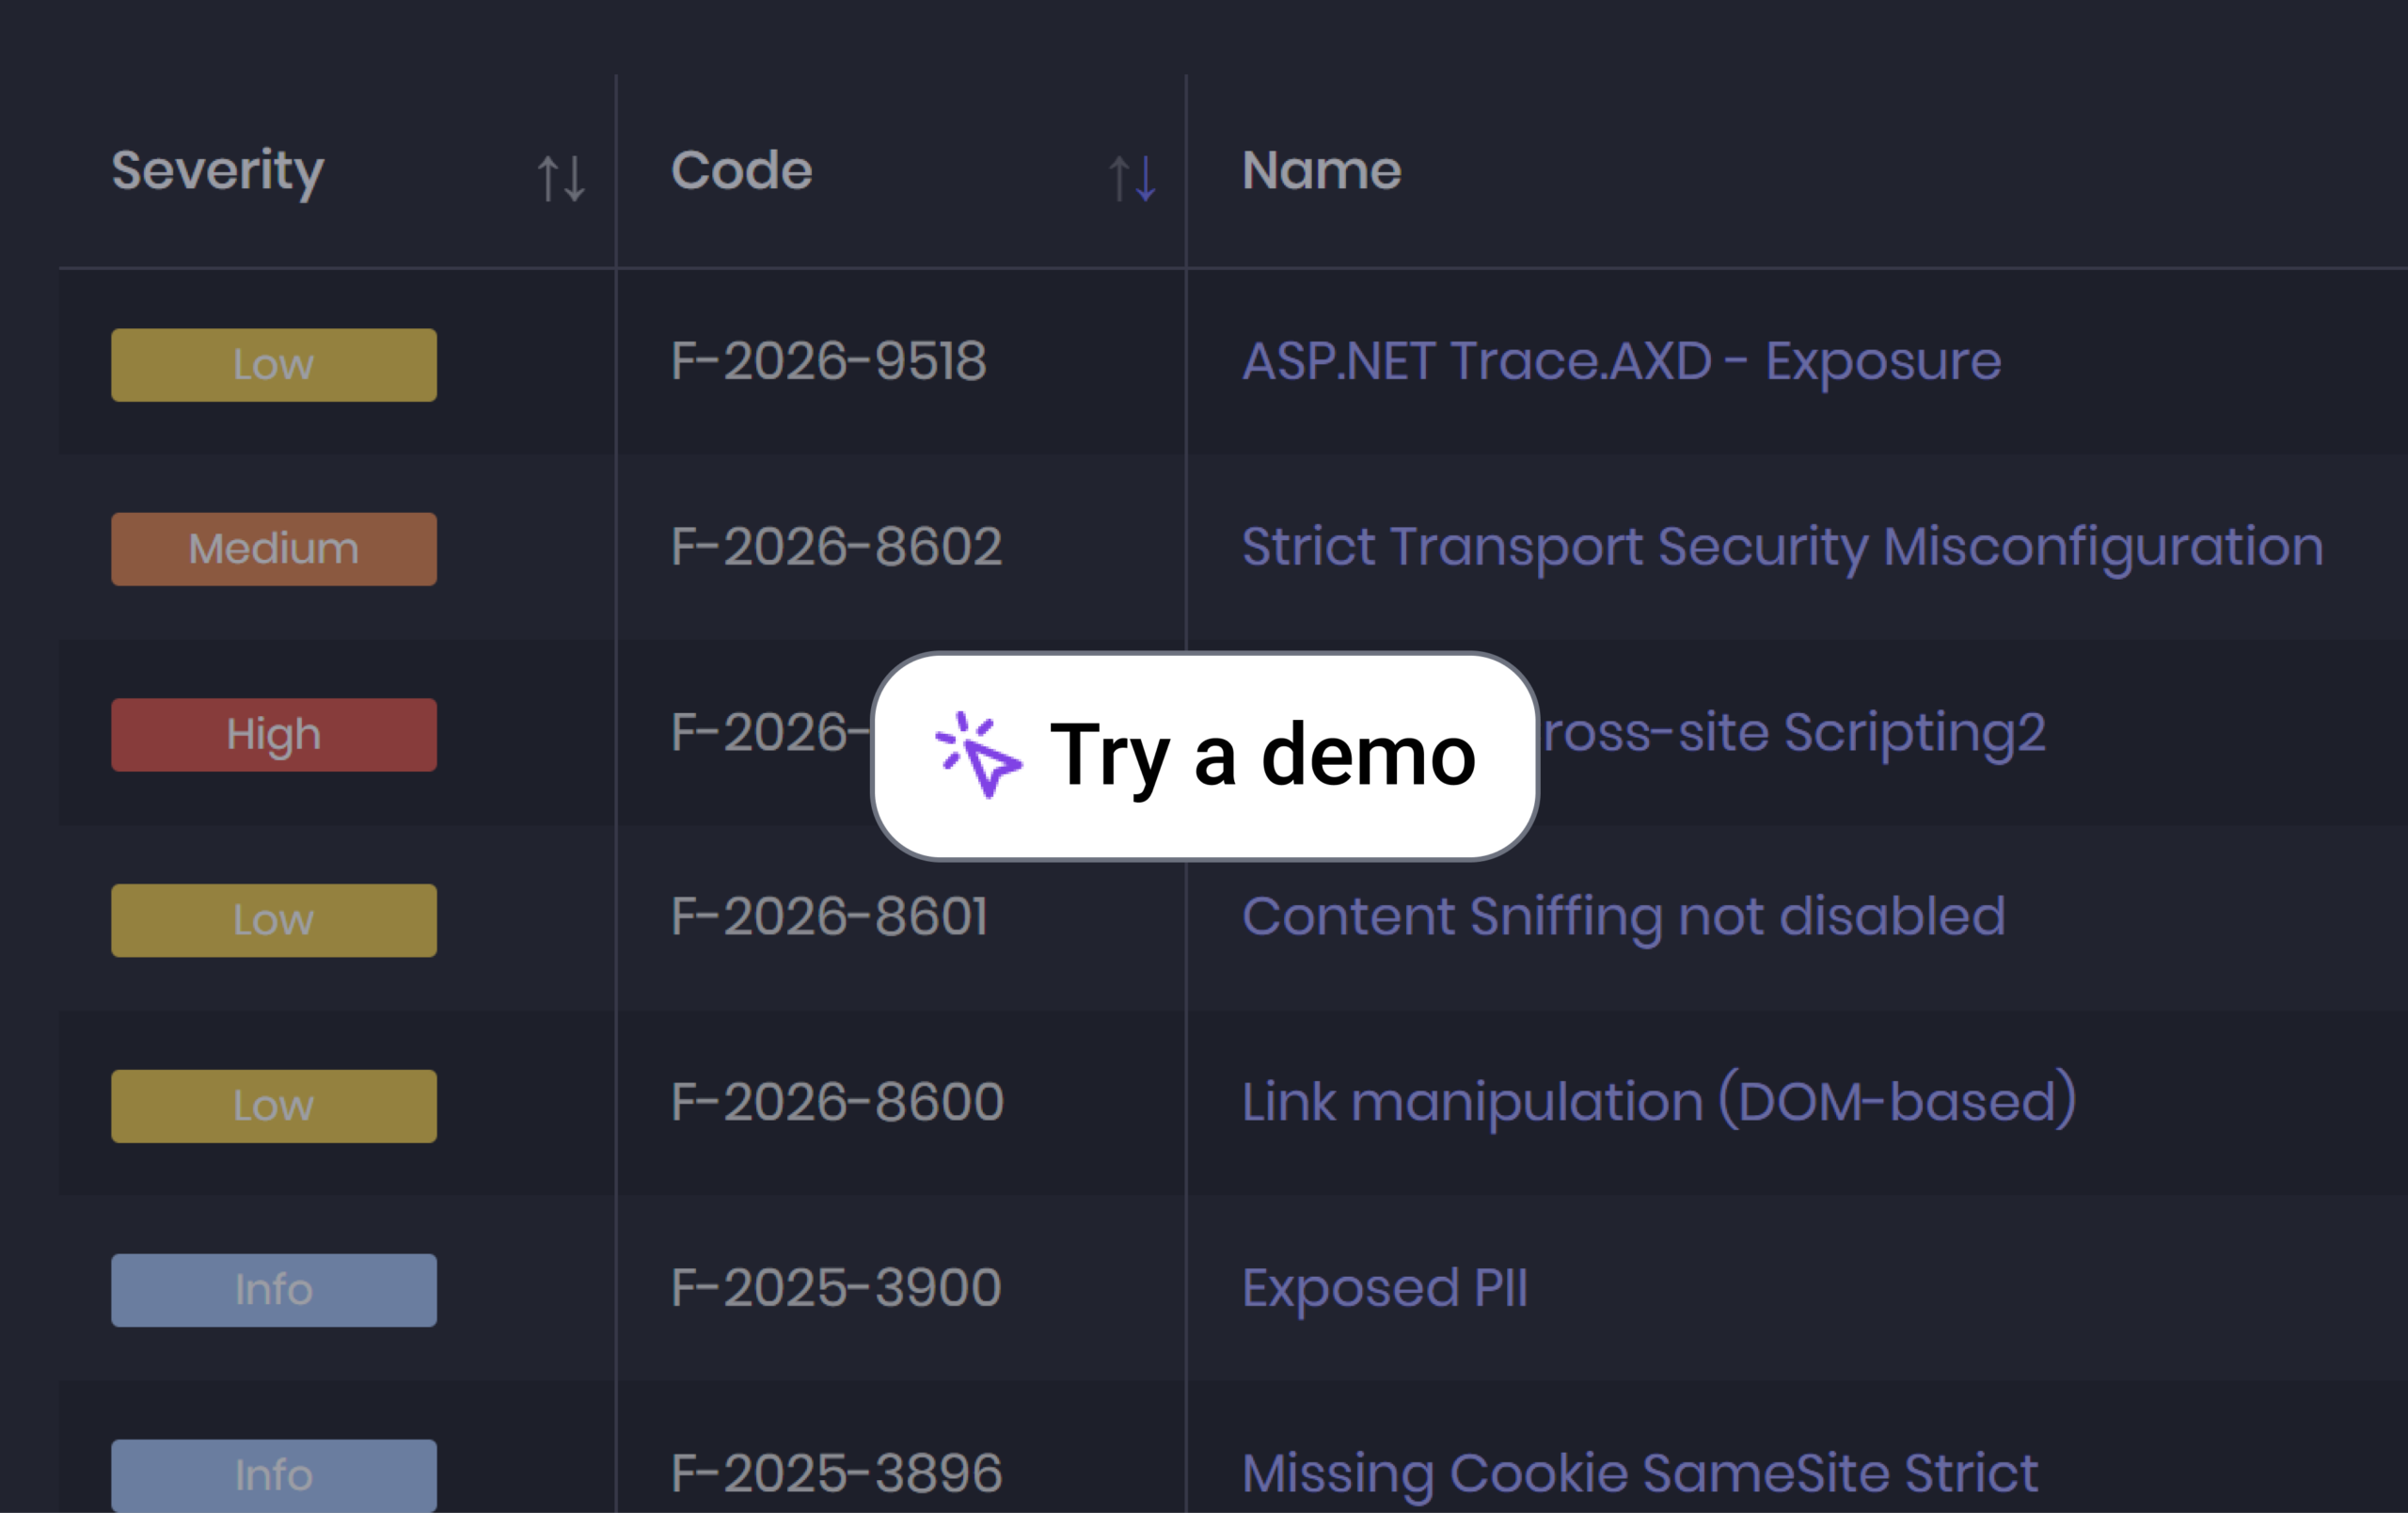
Document findings with evidence, affected assets, and remediation guidance. Assign severity using CVSS scores, the built-in calculator, or custom scoring.

Tool Integrations and Imports

Import results from tools such as Burp Suite, Nessus, Nmap, and Qualys into a centralized finding management workflow.

Collaborative Report Editor

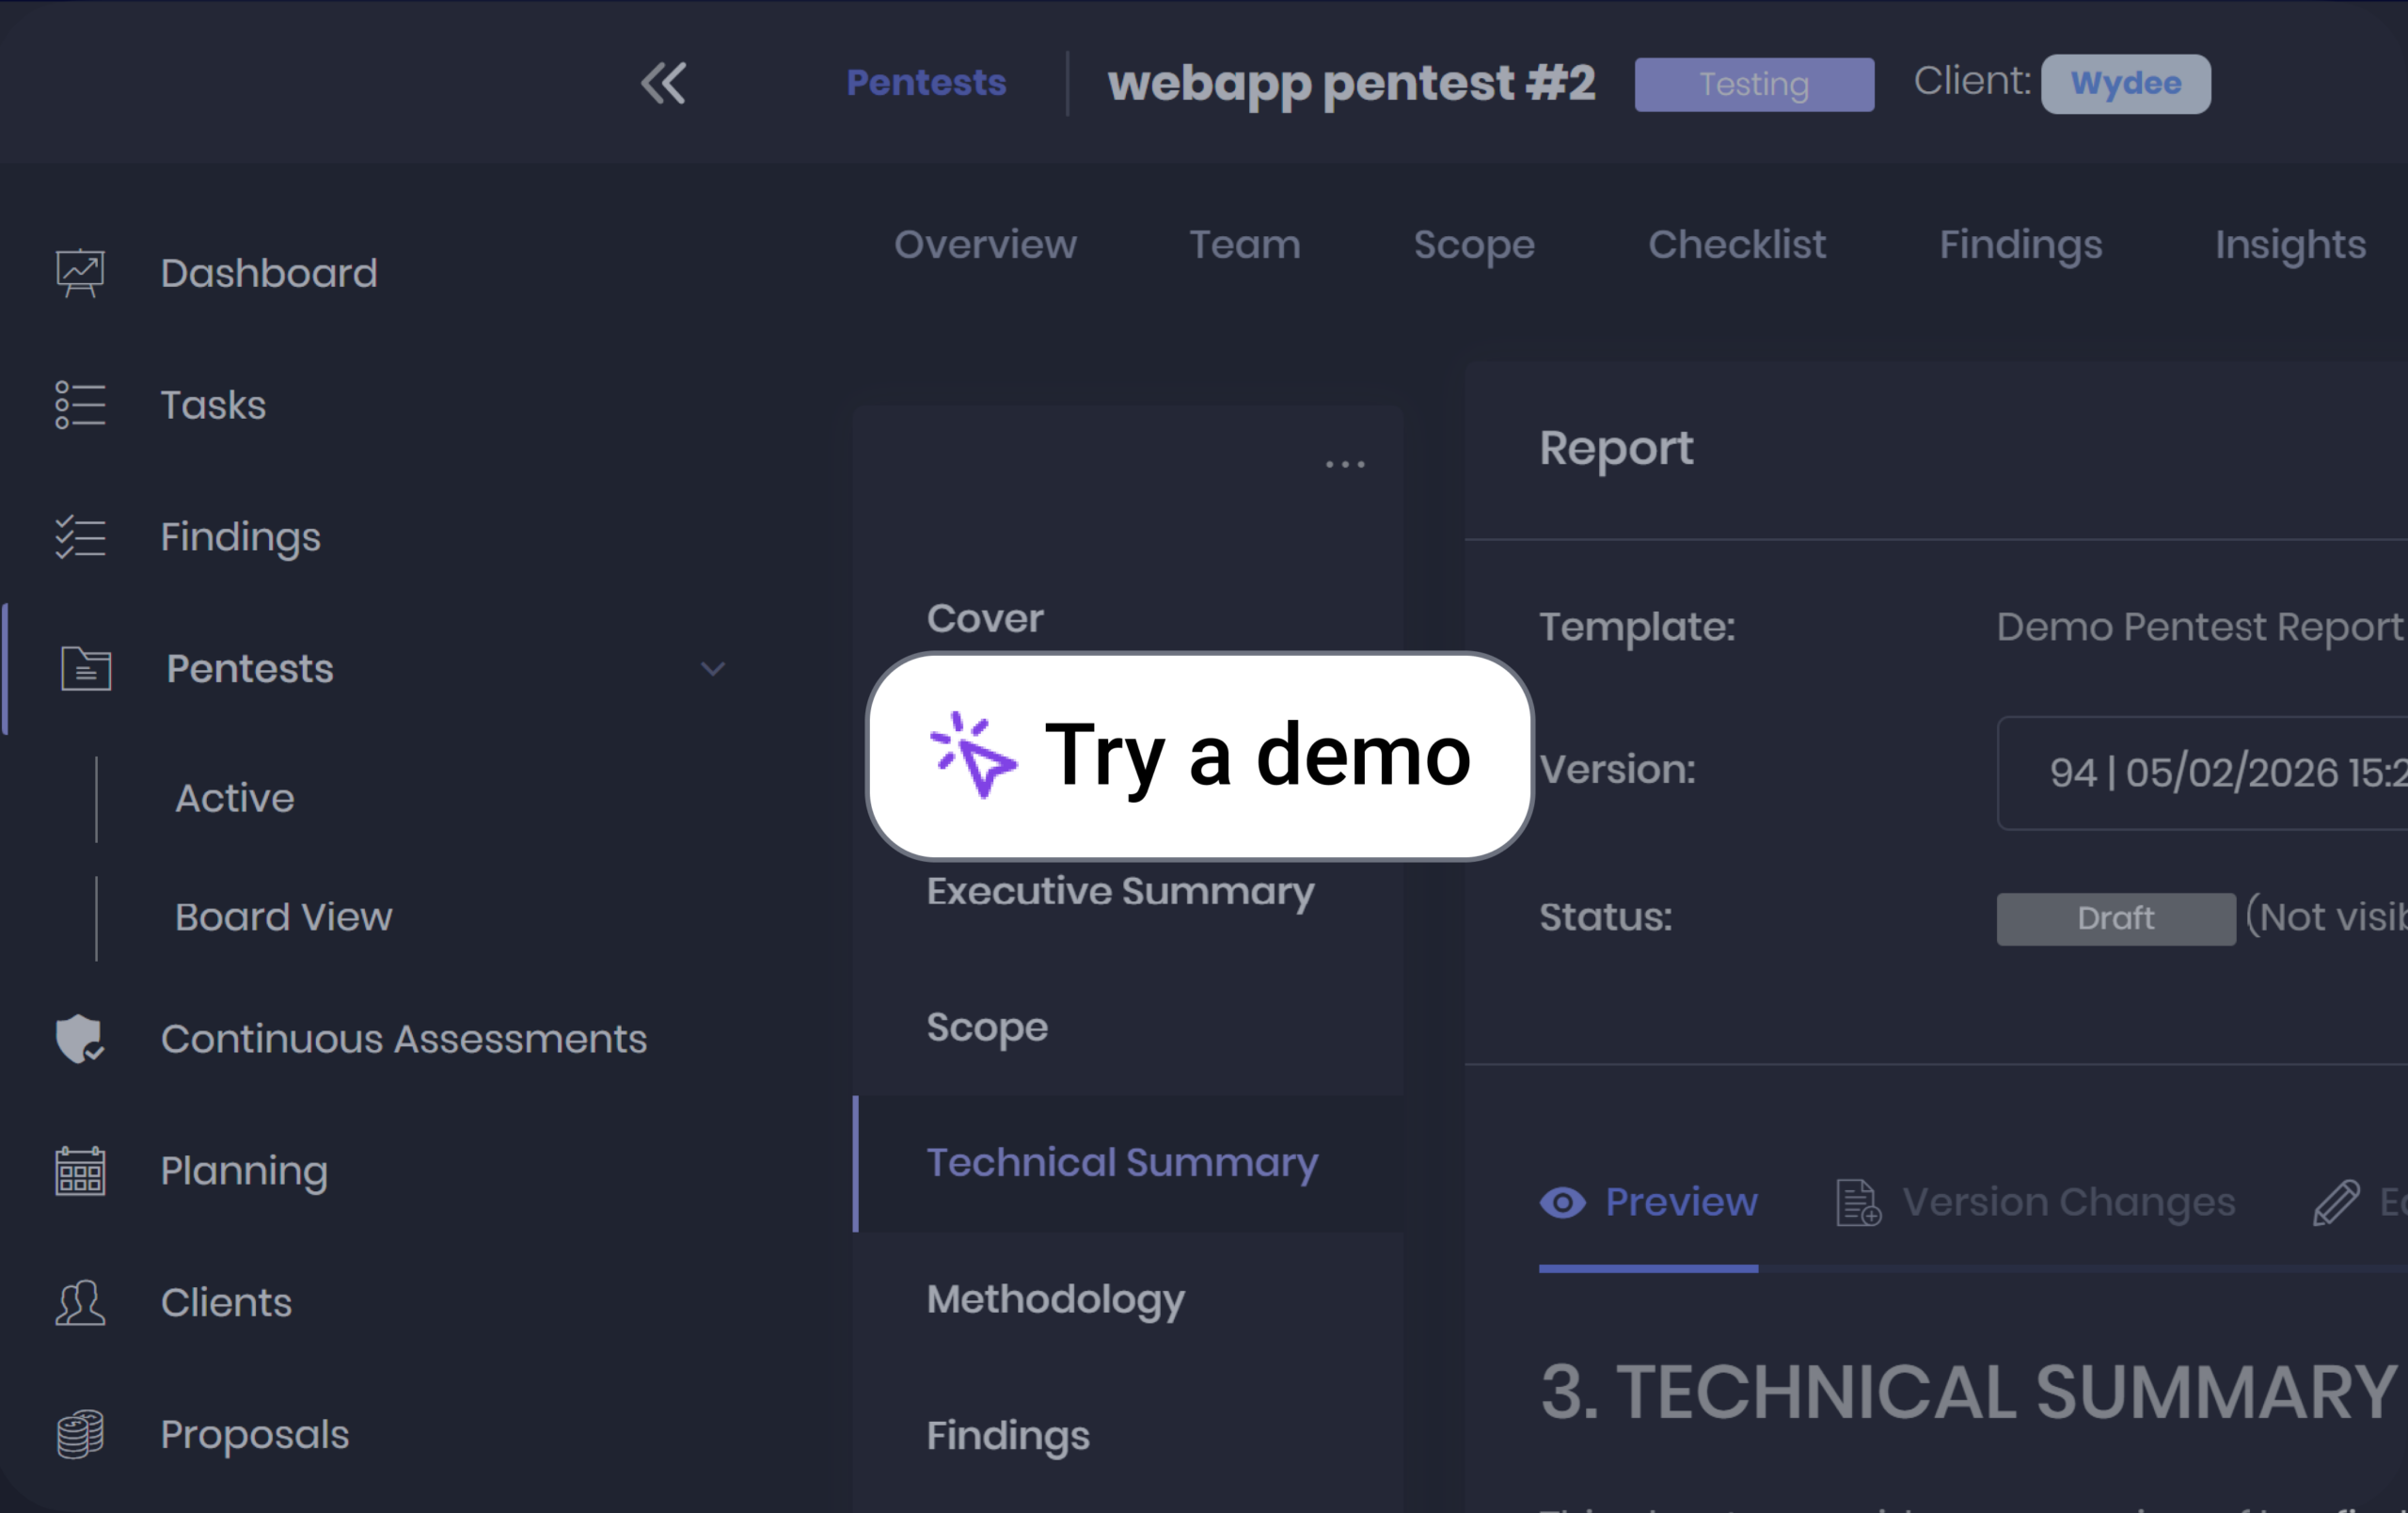
Edit reports with rich-text formatting, dynamic tokens, and AI assistance. Support concurrent editing with automatic saving and version control.

Comments and Peer Review

Add comments, review technical details, and resolve feedback with teammates before finalizing findings and reports.

Report Delivery and Client Portal

Deliver branded reports through the client portal, with access to findings, remediation status, and retesting updates.

Ready to dive into the platform?

  • Walk through the plaform, capabilities, and solutions
  • Understand what Cyver Core offers
  • Improve your team’s efficiency.
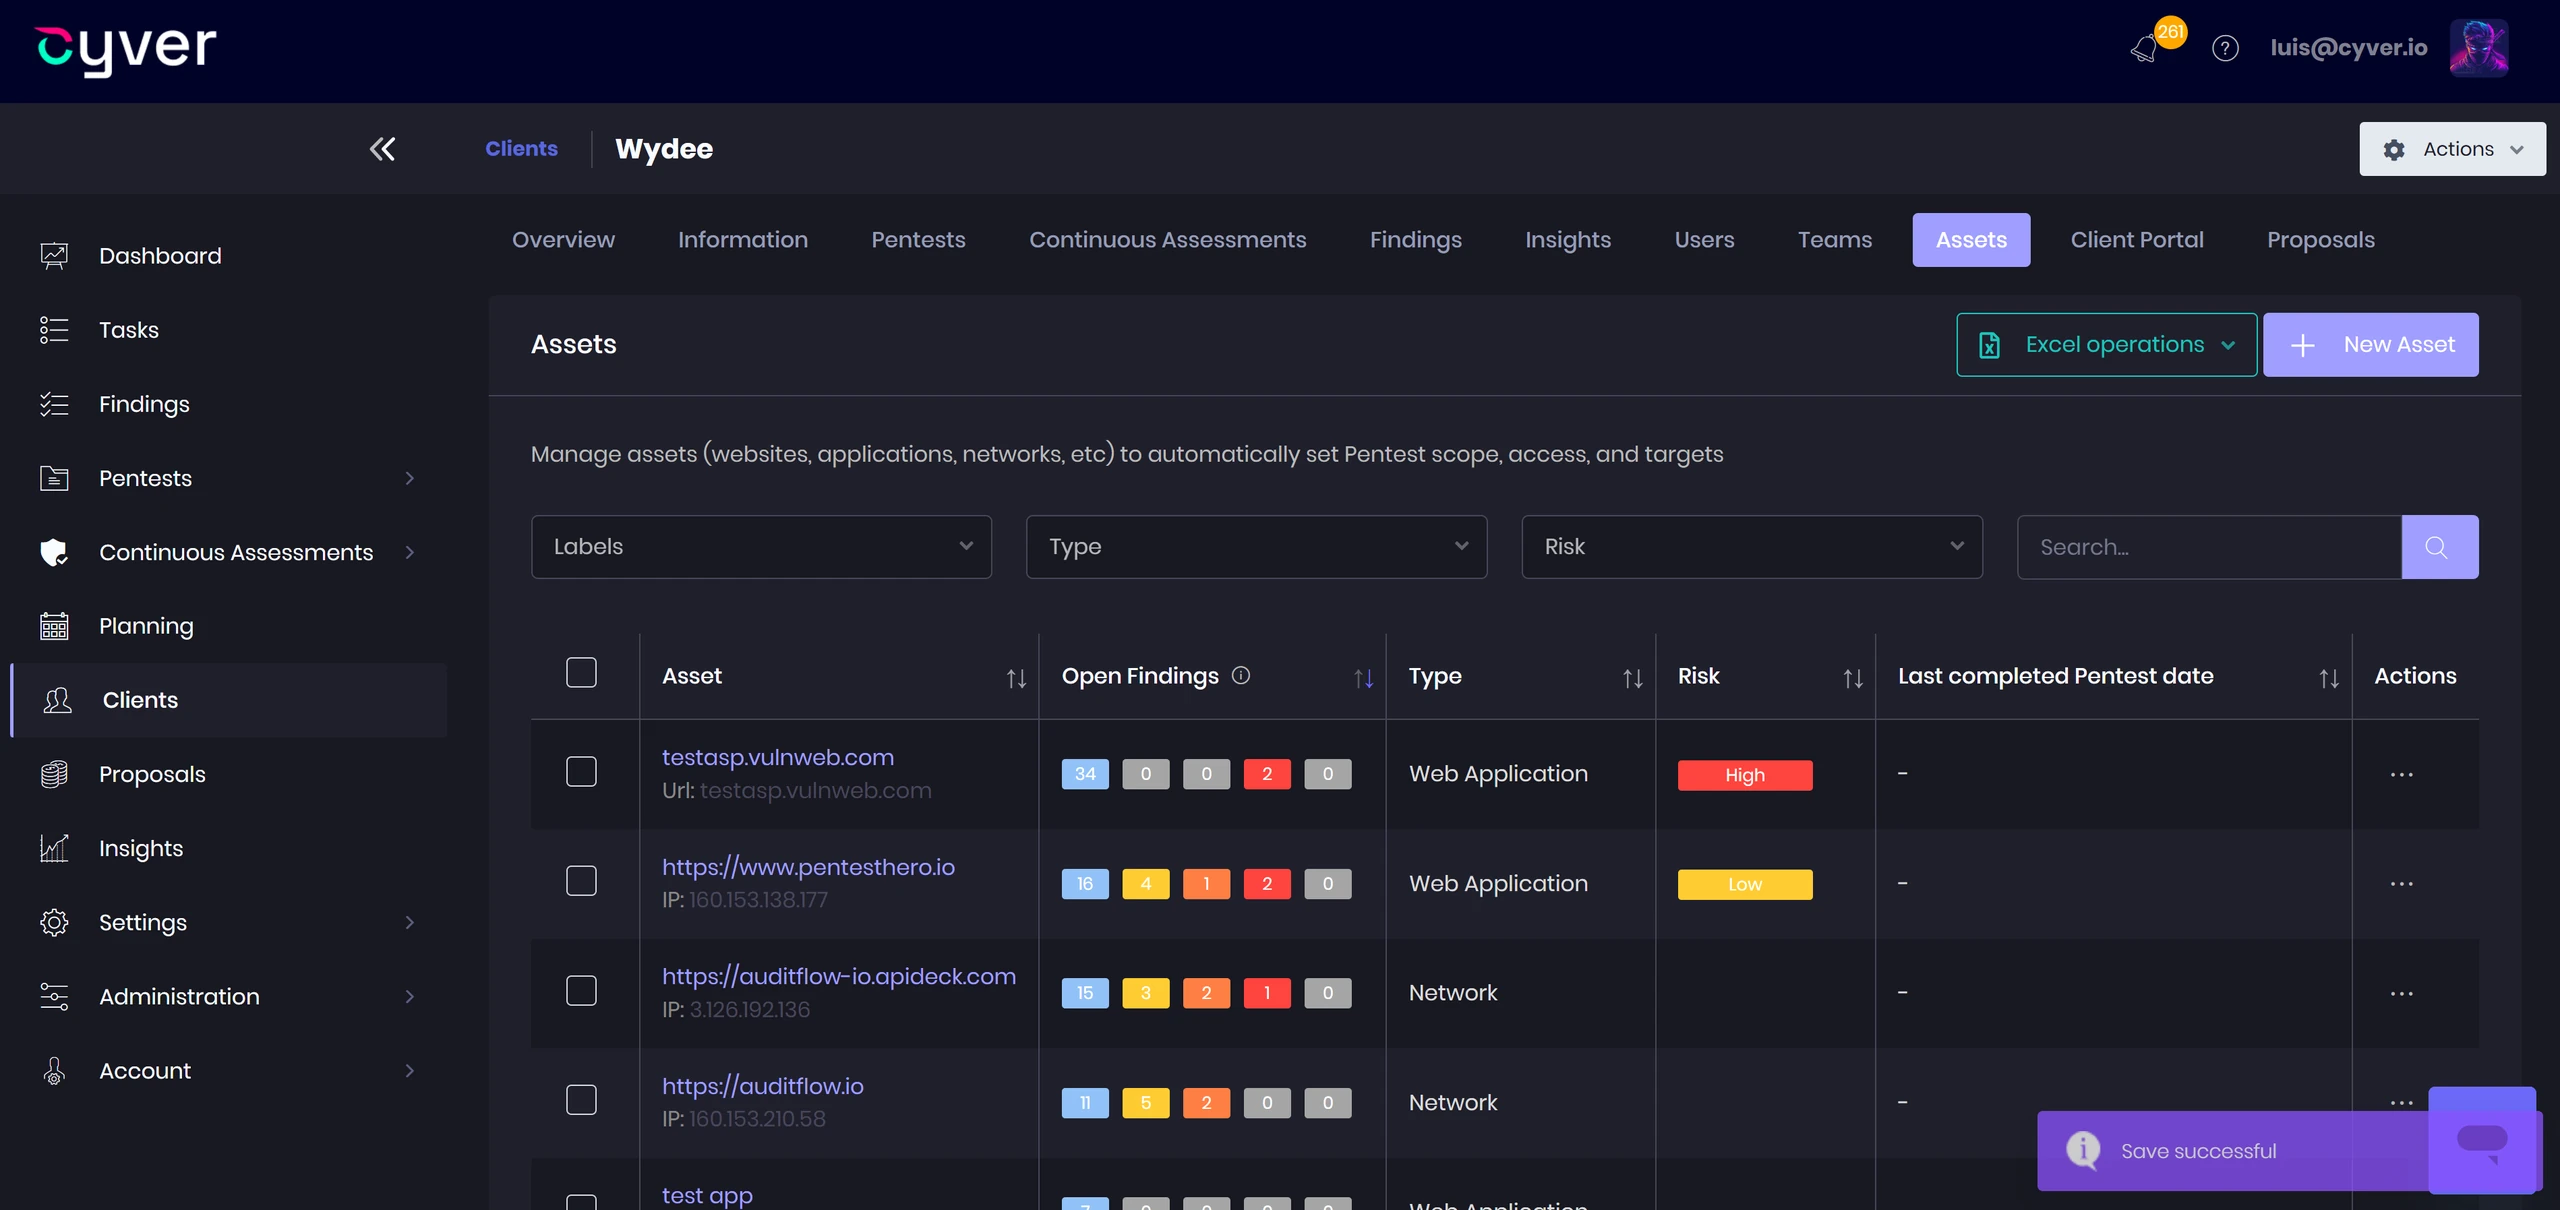
Cyver Core vulnerability management: Asset and Finding Inventory

Asset and Finding Inventory

Maintain a centralized inventory of assets and associated vulnerabilities. Organize findings by client, project, team, and affected system.

Cyver Core vulnerability management: Scanner and Tool Integrations

Scanner and Tool Integrations

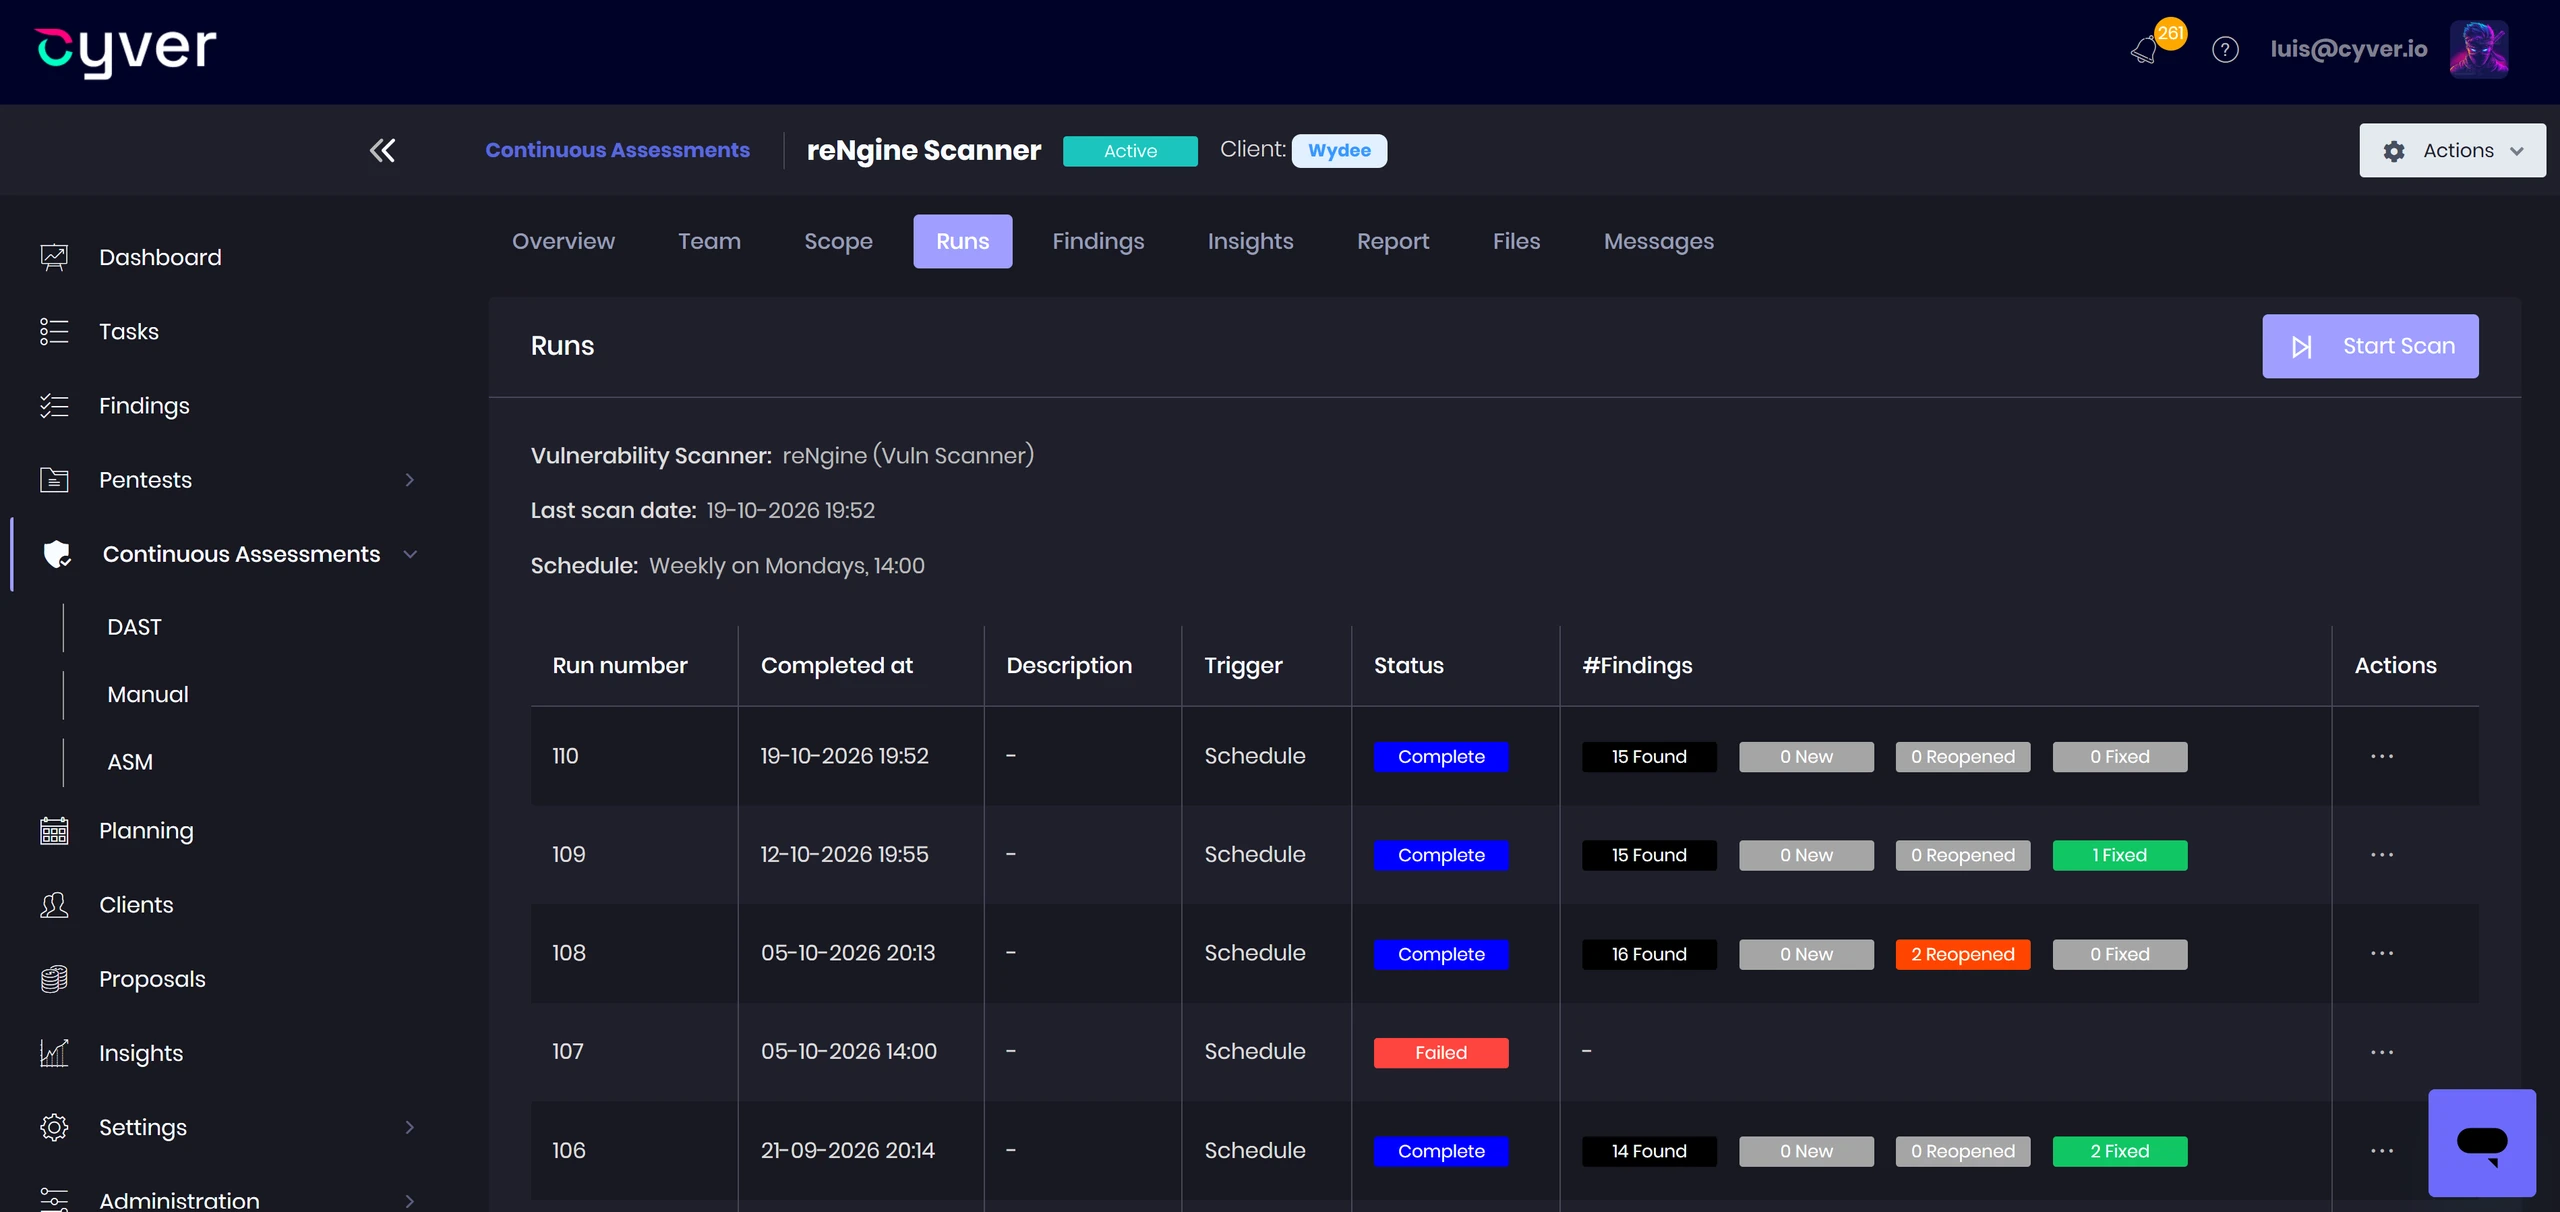
Import findings from vulnerability scanners and security tools, including Tenable, reNgine, and Escape. Consolidate automated results alongside manual pentest findings.

Cyver Core vulnerability management: Finding Classification and Scoring

Finding Classification and Scoring

Document vulnerability details, evidence, and remediation guidance. Classify findings using CVSS scores, the built-in calculator, or custom scoring.

Cyver Core vulnerability management: Risk Prioritization

Risk Prioritization

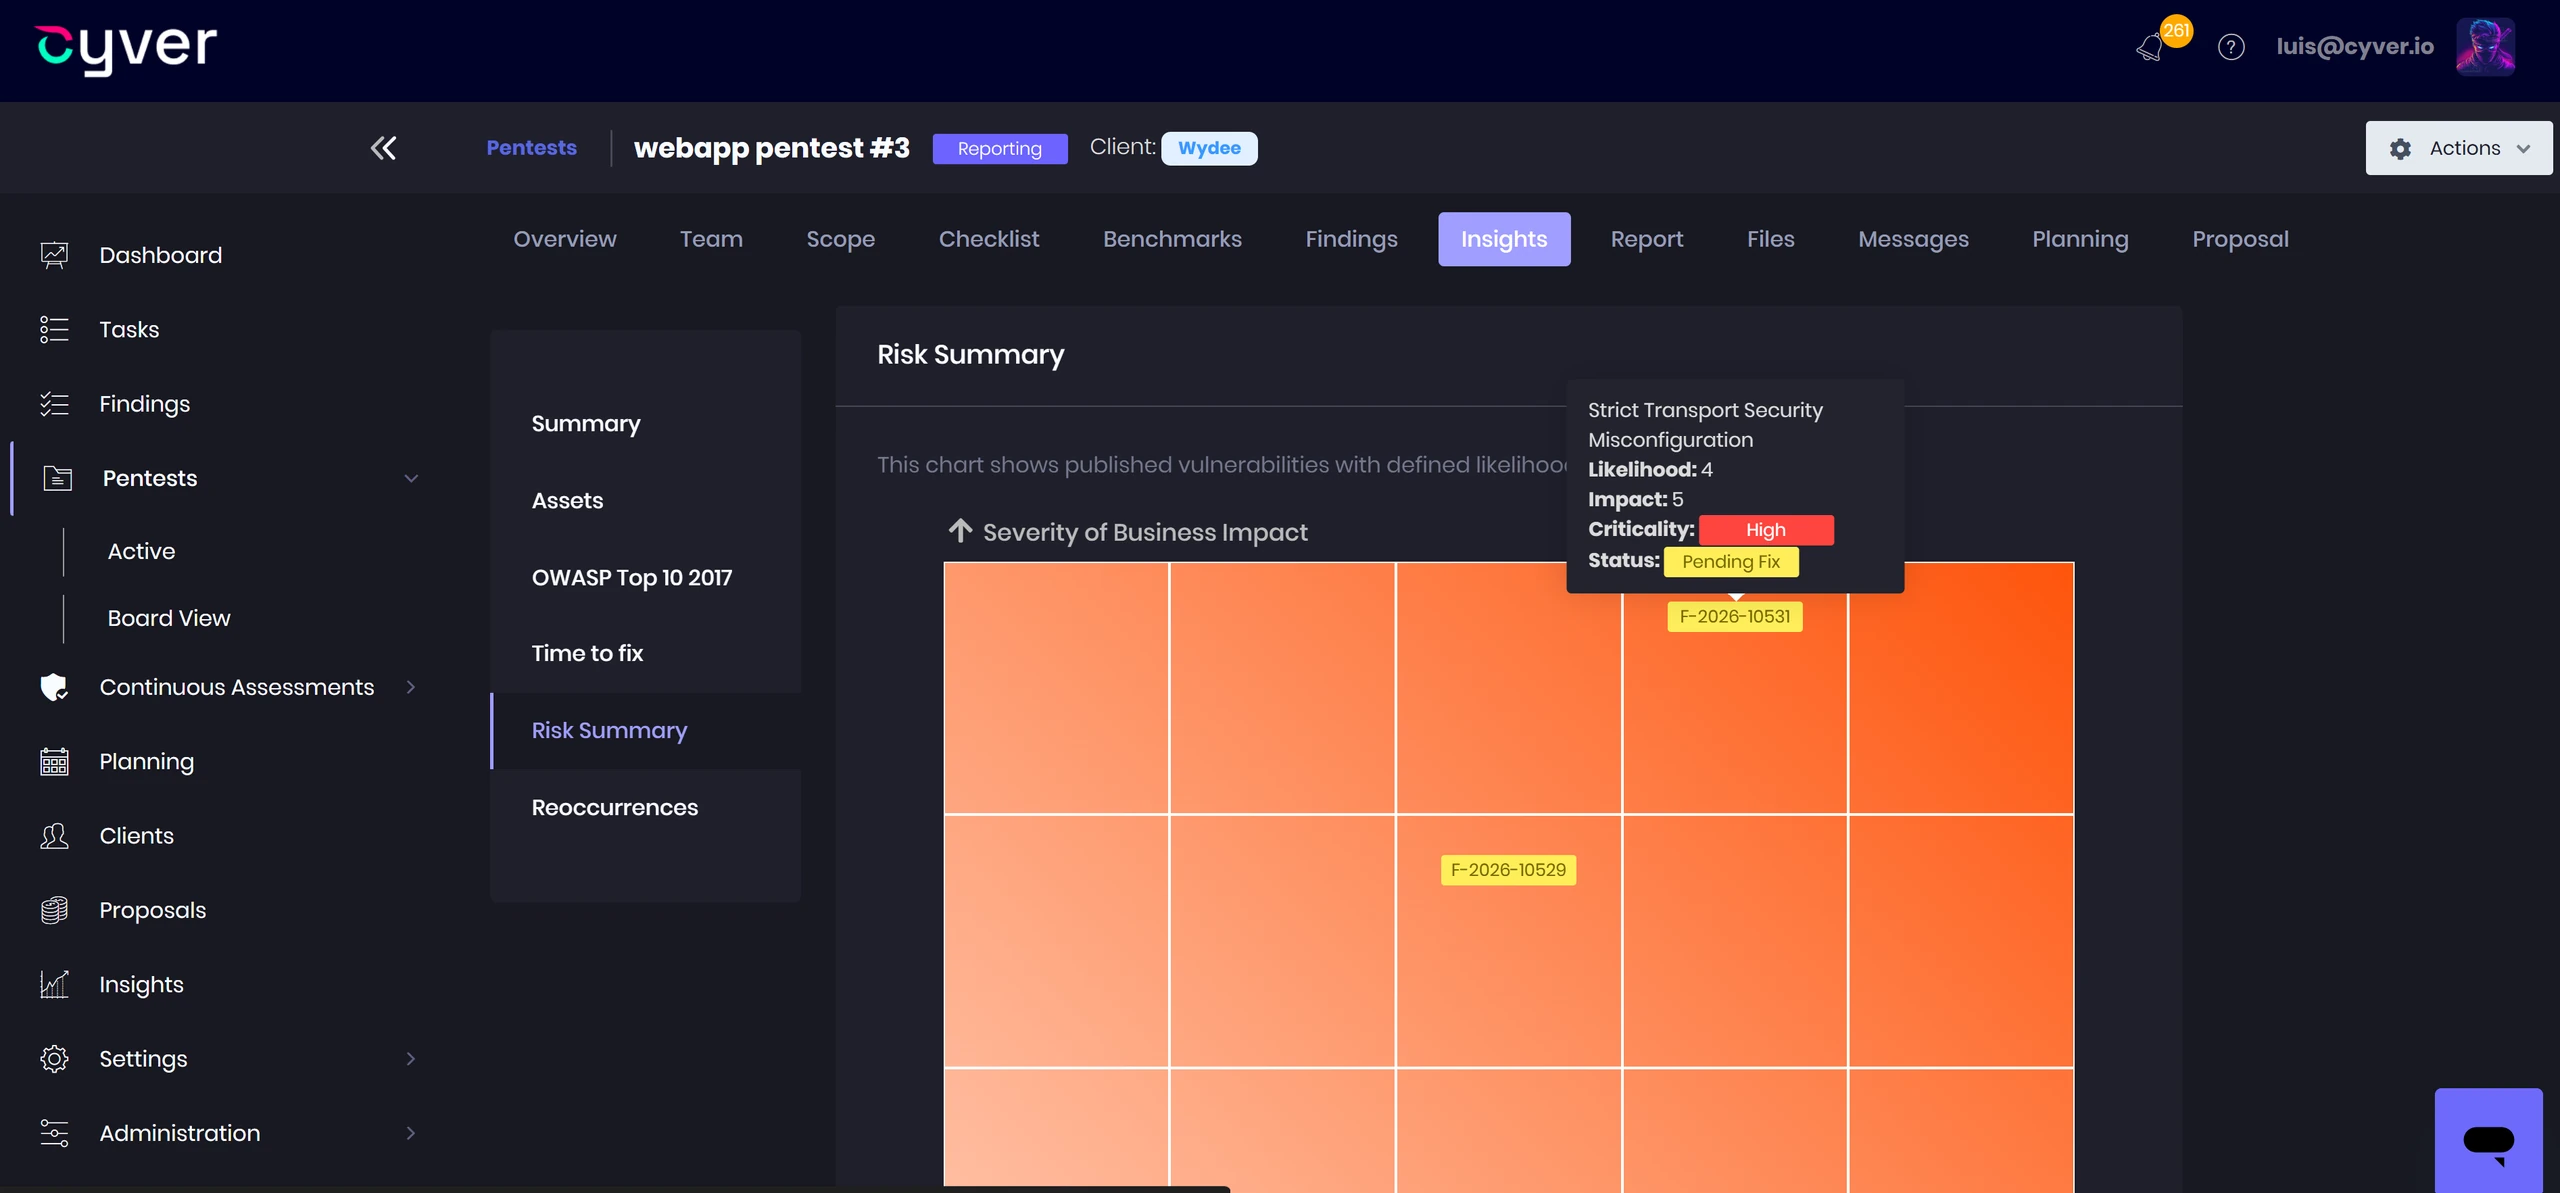
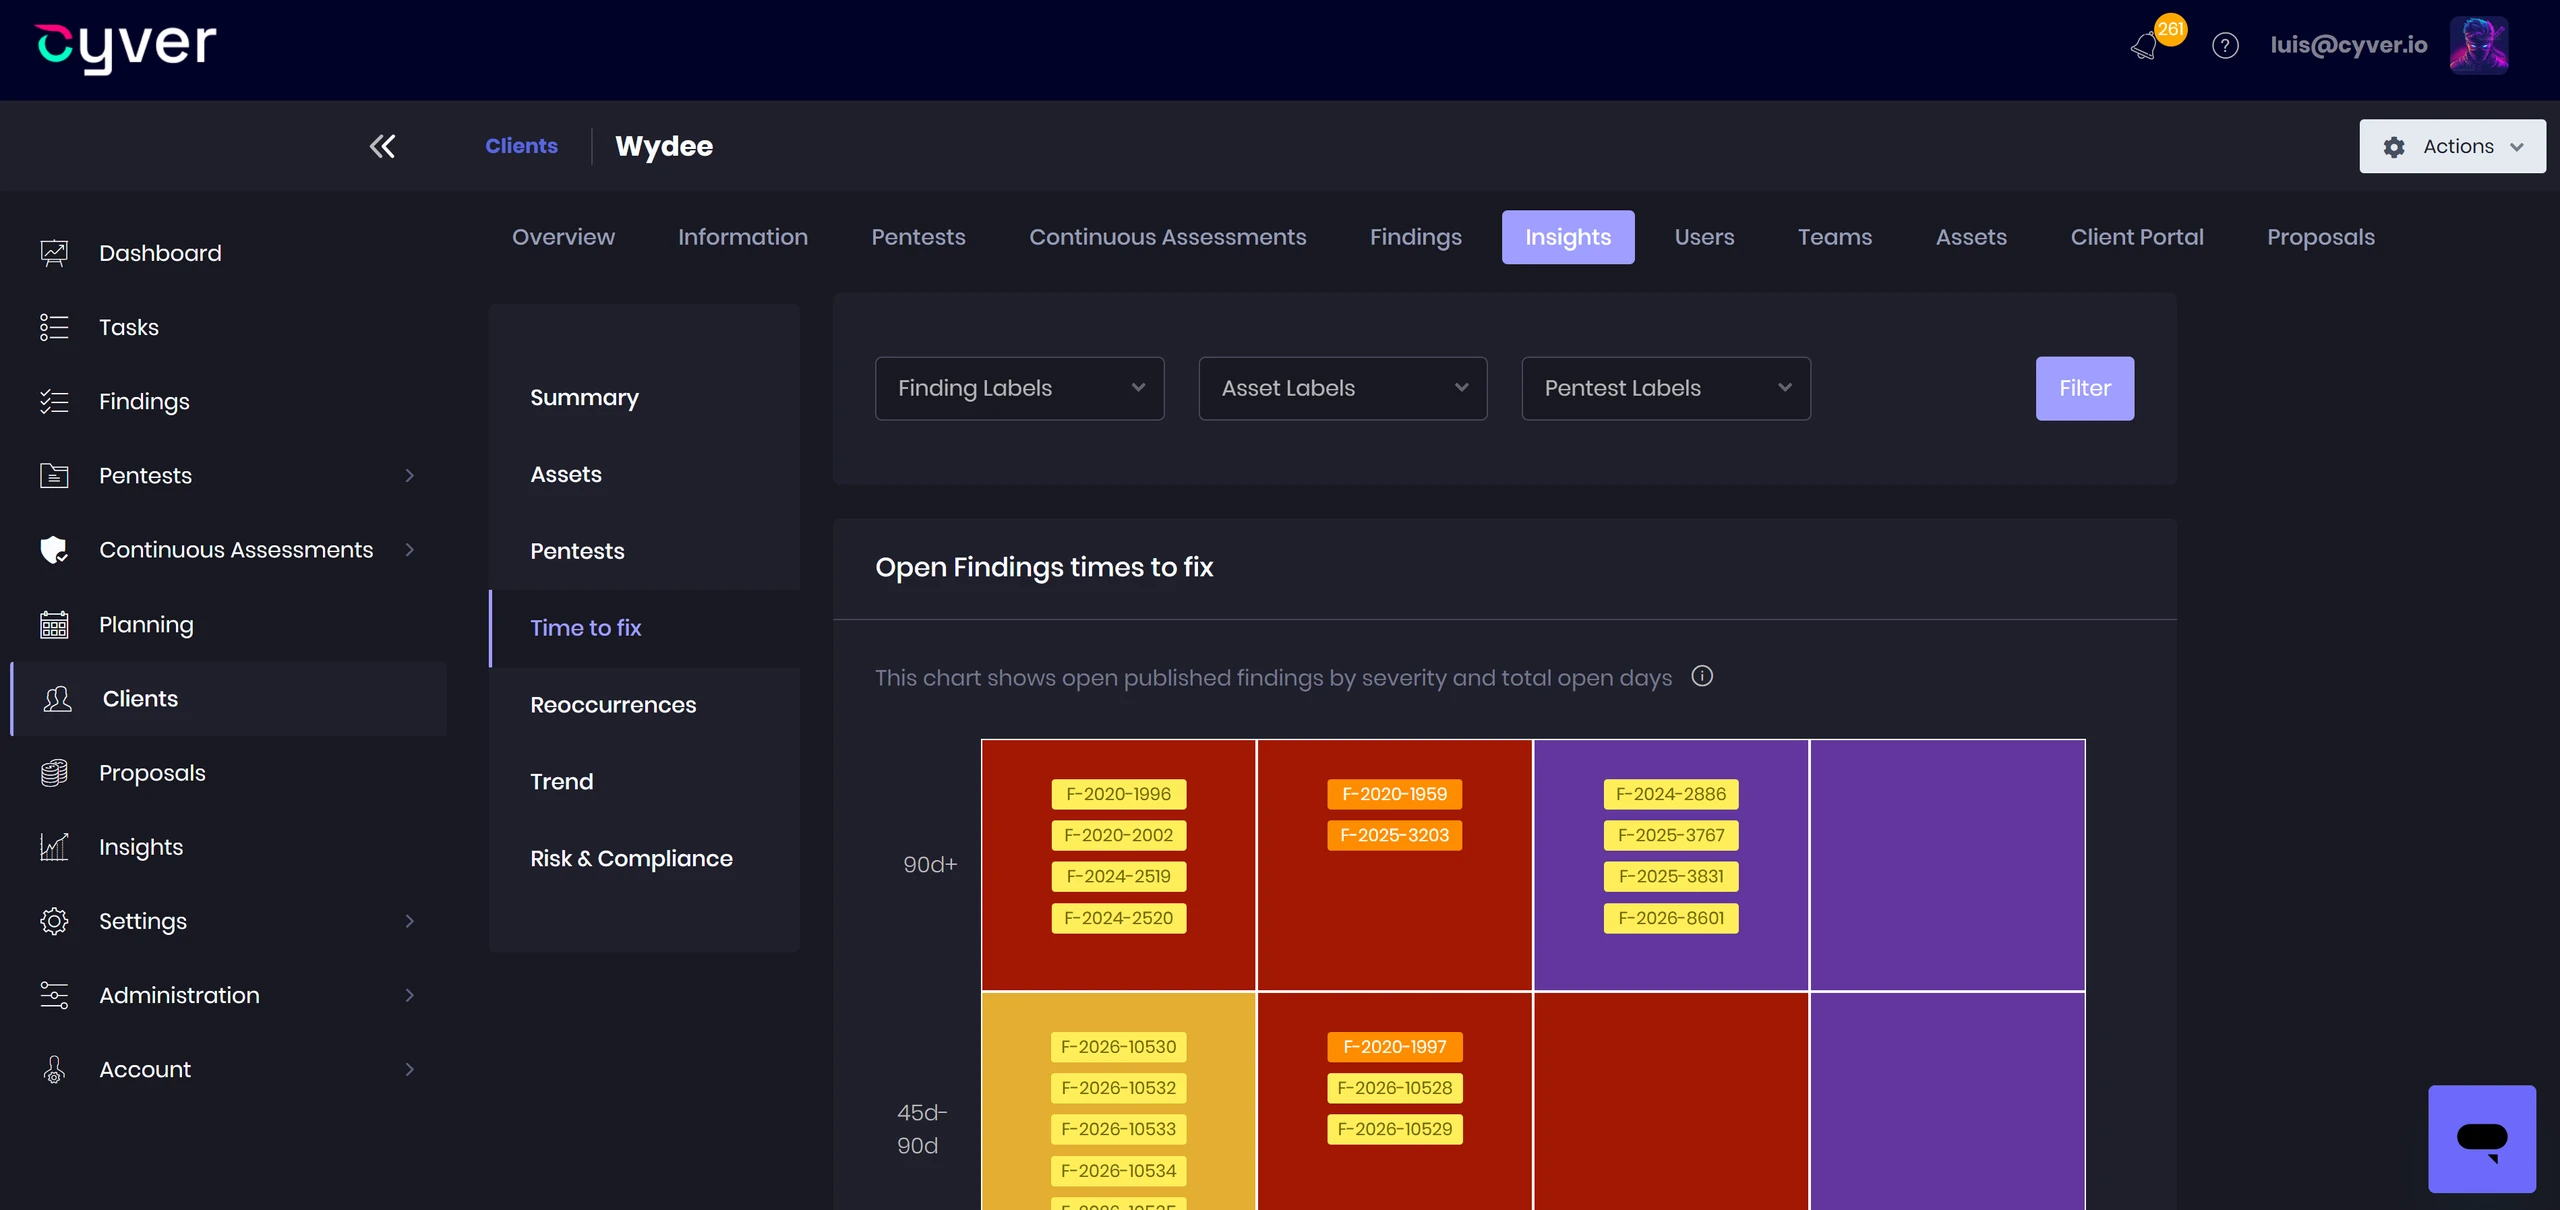
Prioritize vulnerabilities using severity, asset context, and business impact. Filter findings to identify critical exposures and plan remediation activities.

Cyver Core vulnerability management: Remediation Assignment and Tracking

Remediation Assignment and Tracking

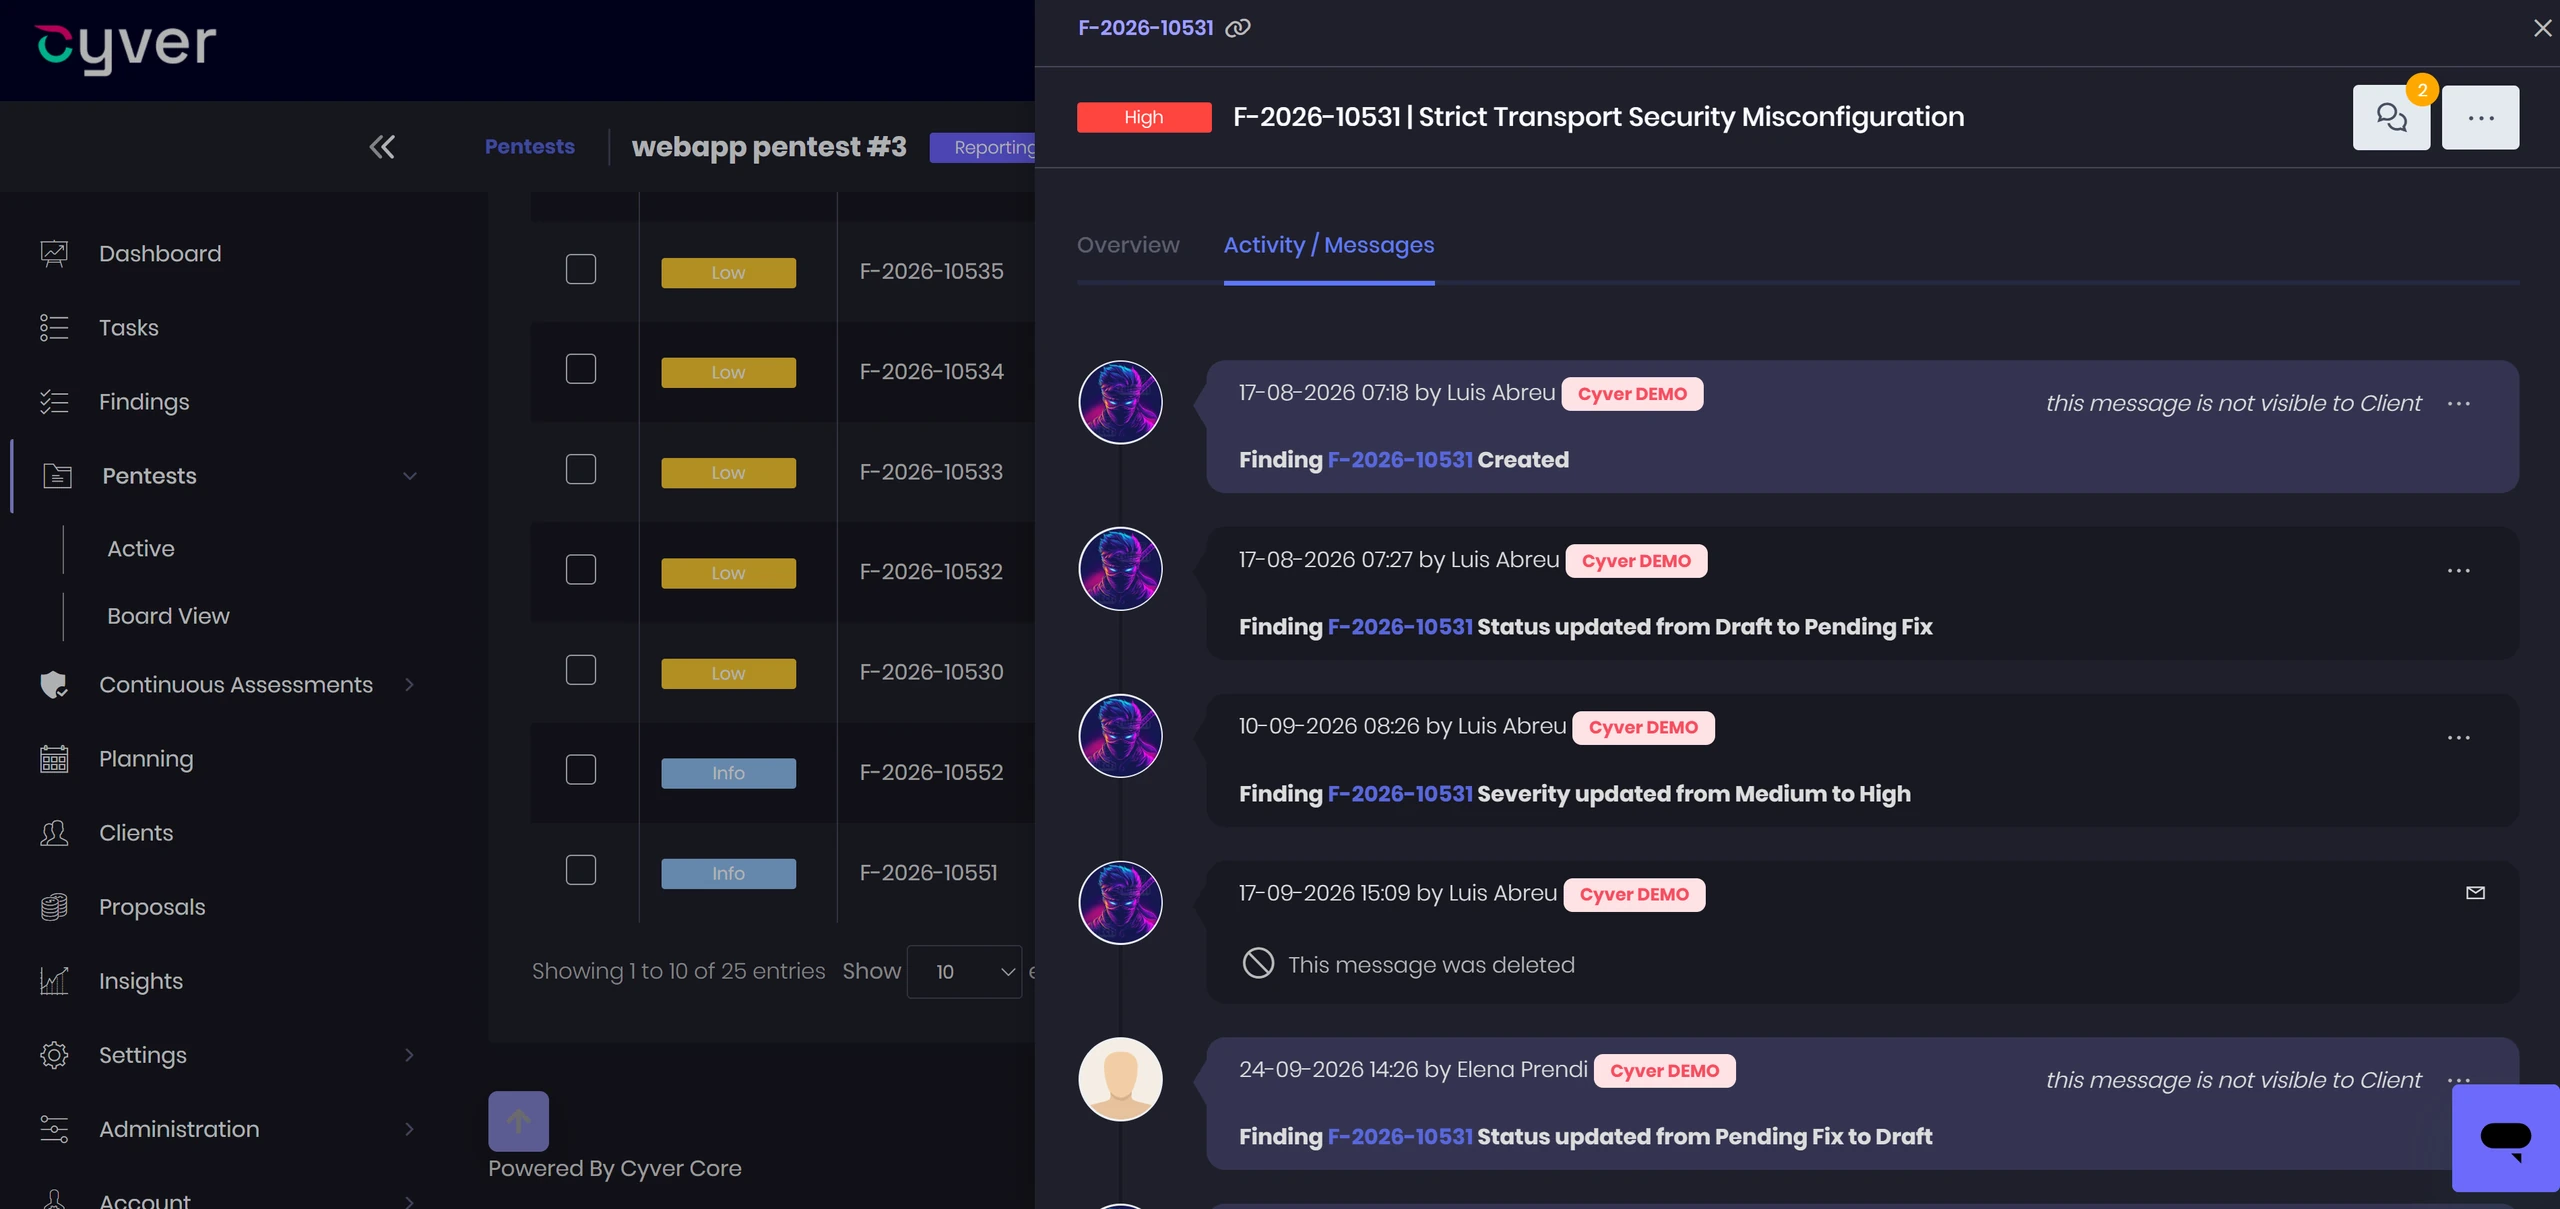
Assign findings to responsible teams and track remediation status. Keep technical discussions, progress updates, and supporting evidence attached to each finding.

Cyver Core vulnerability management: Retesting and Closure

Retesting and Closure

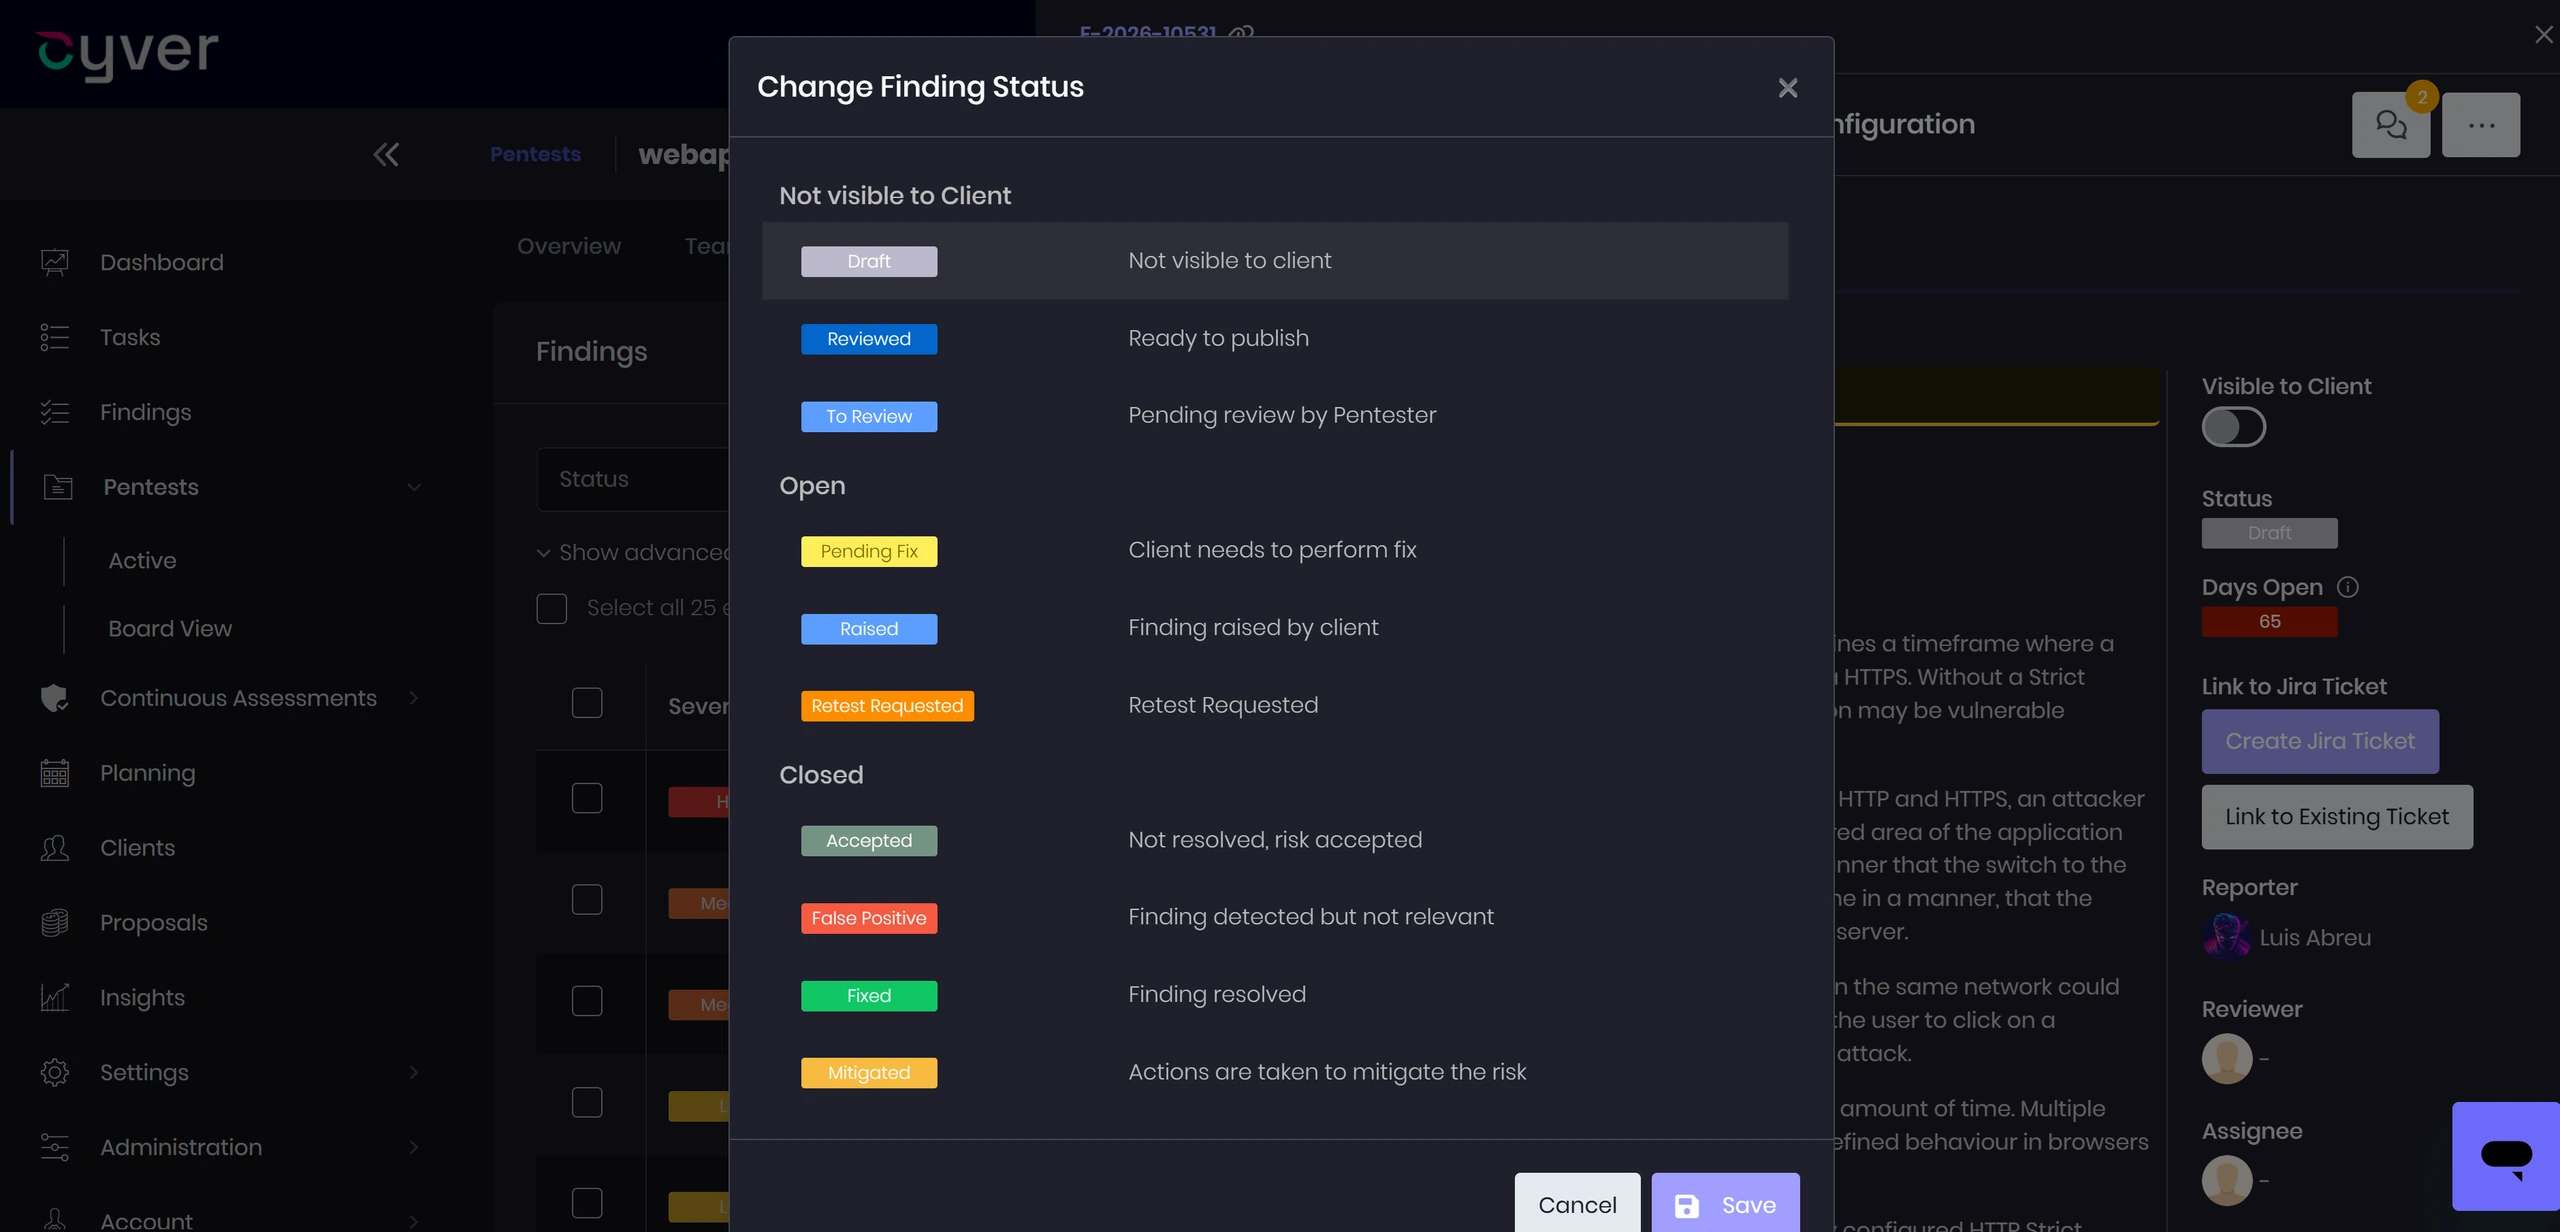
Request retesting and document whether remediation resolves the vulnerability. Update finding status and retain evidence of verification.

Cyver Core vulnerability management: Dashboards and Reporting

Dashboards and Reporting

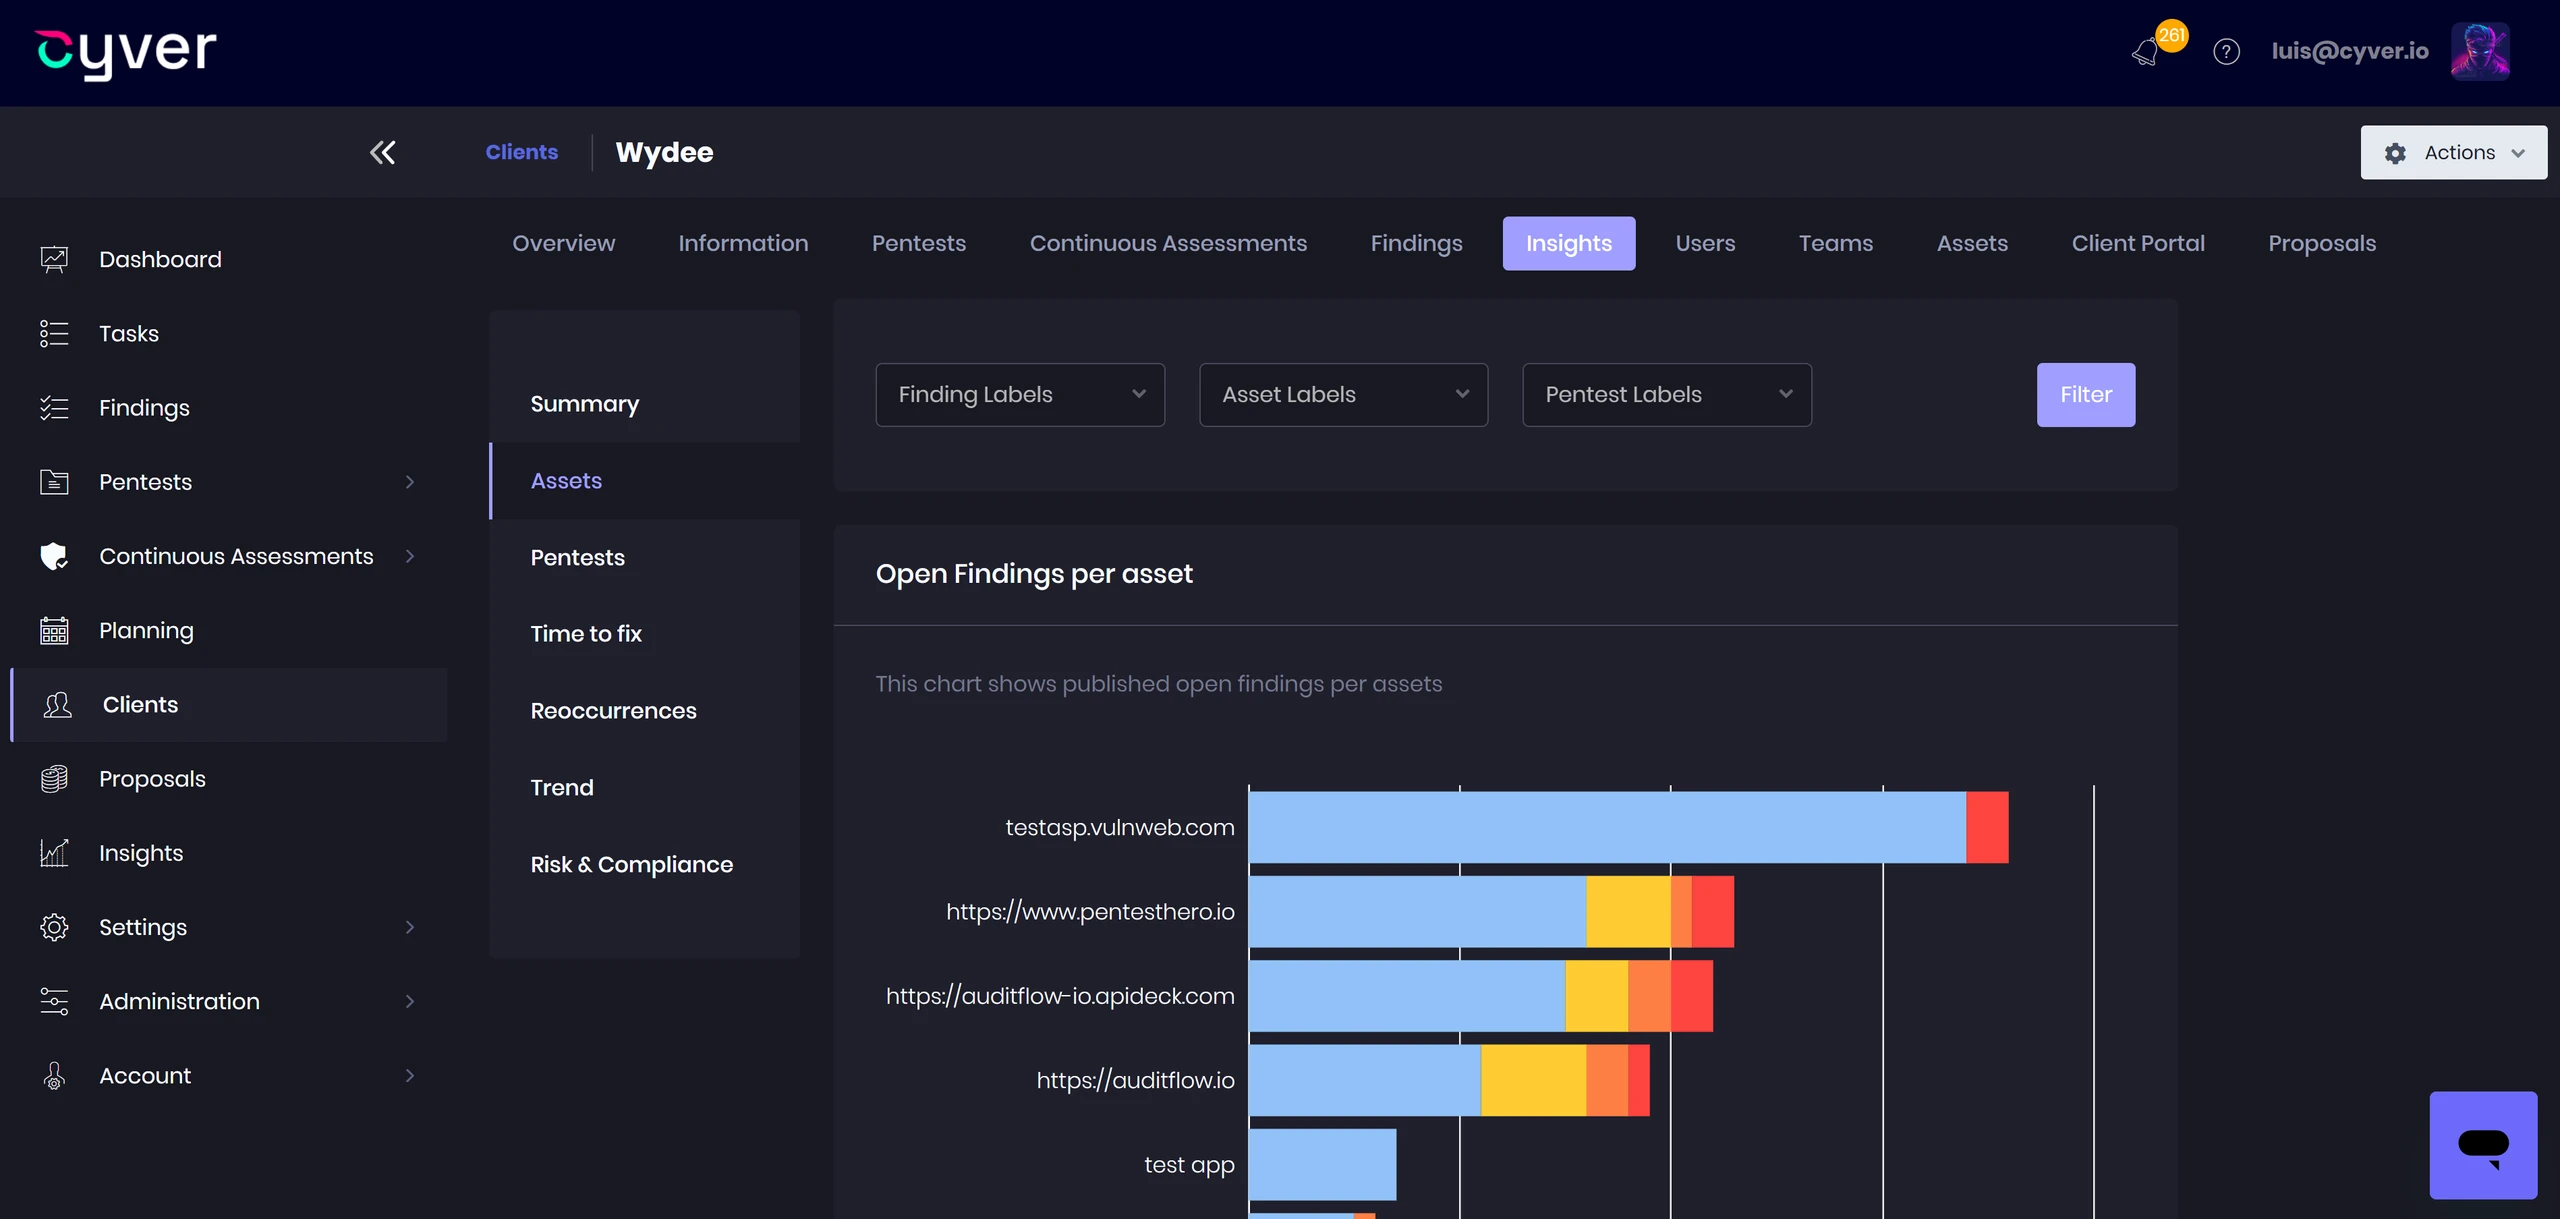
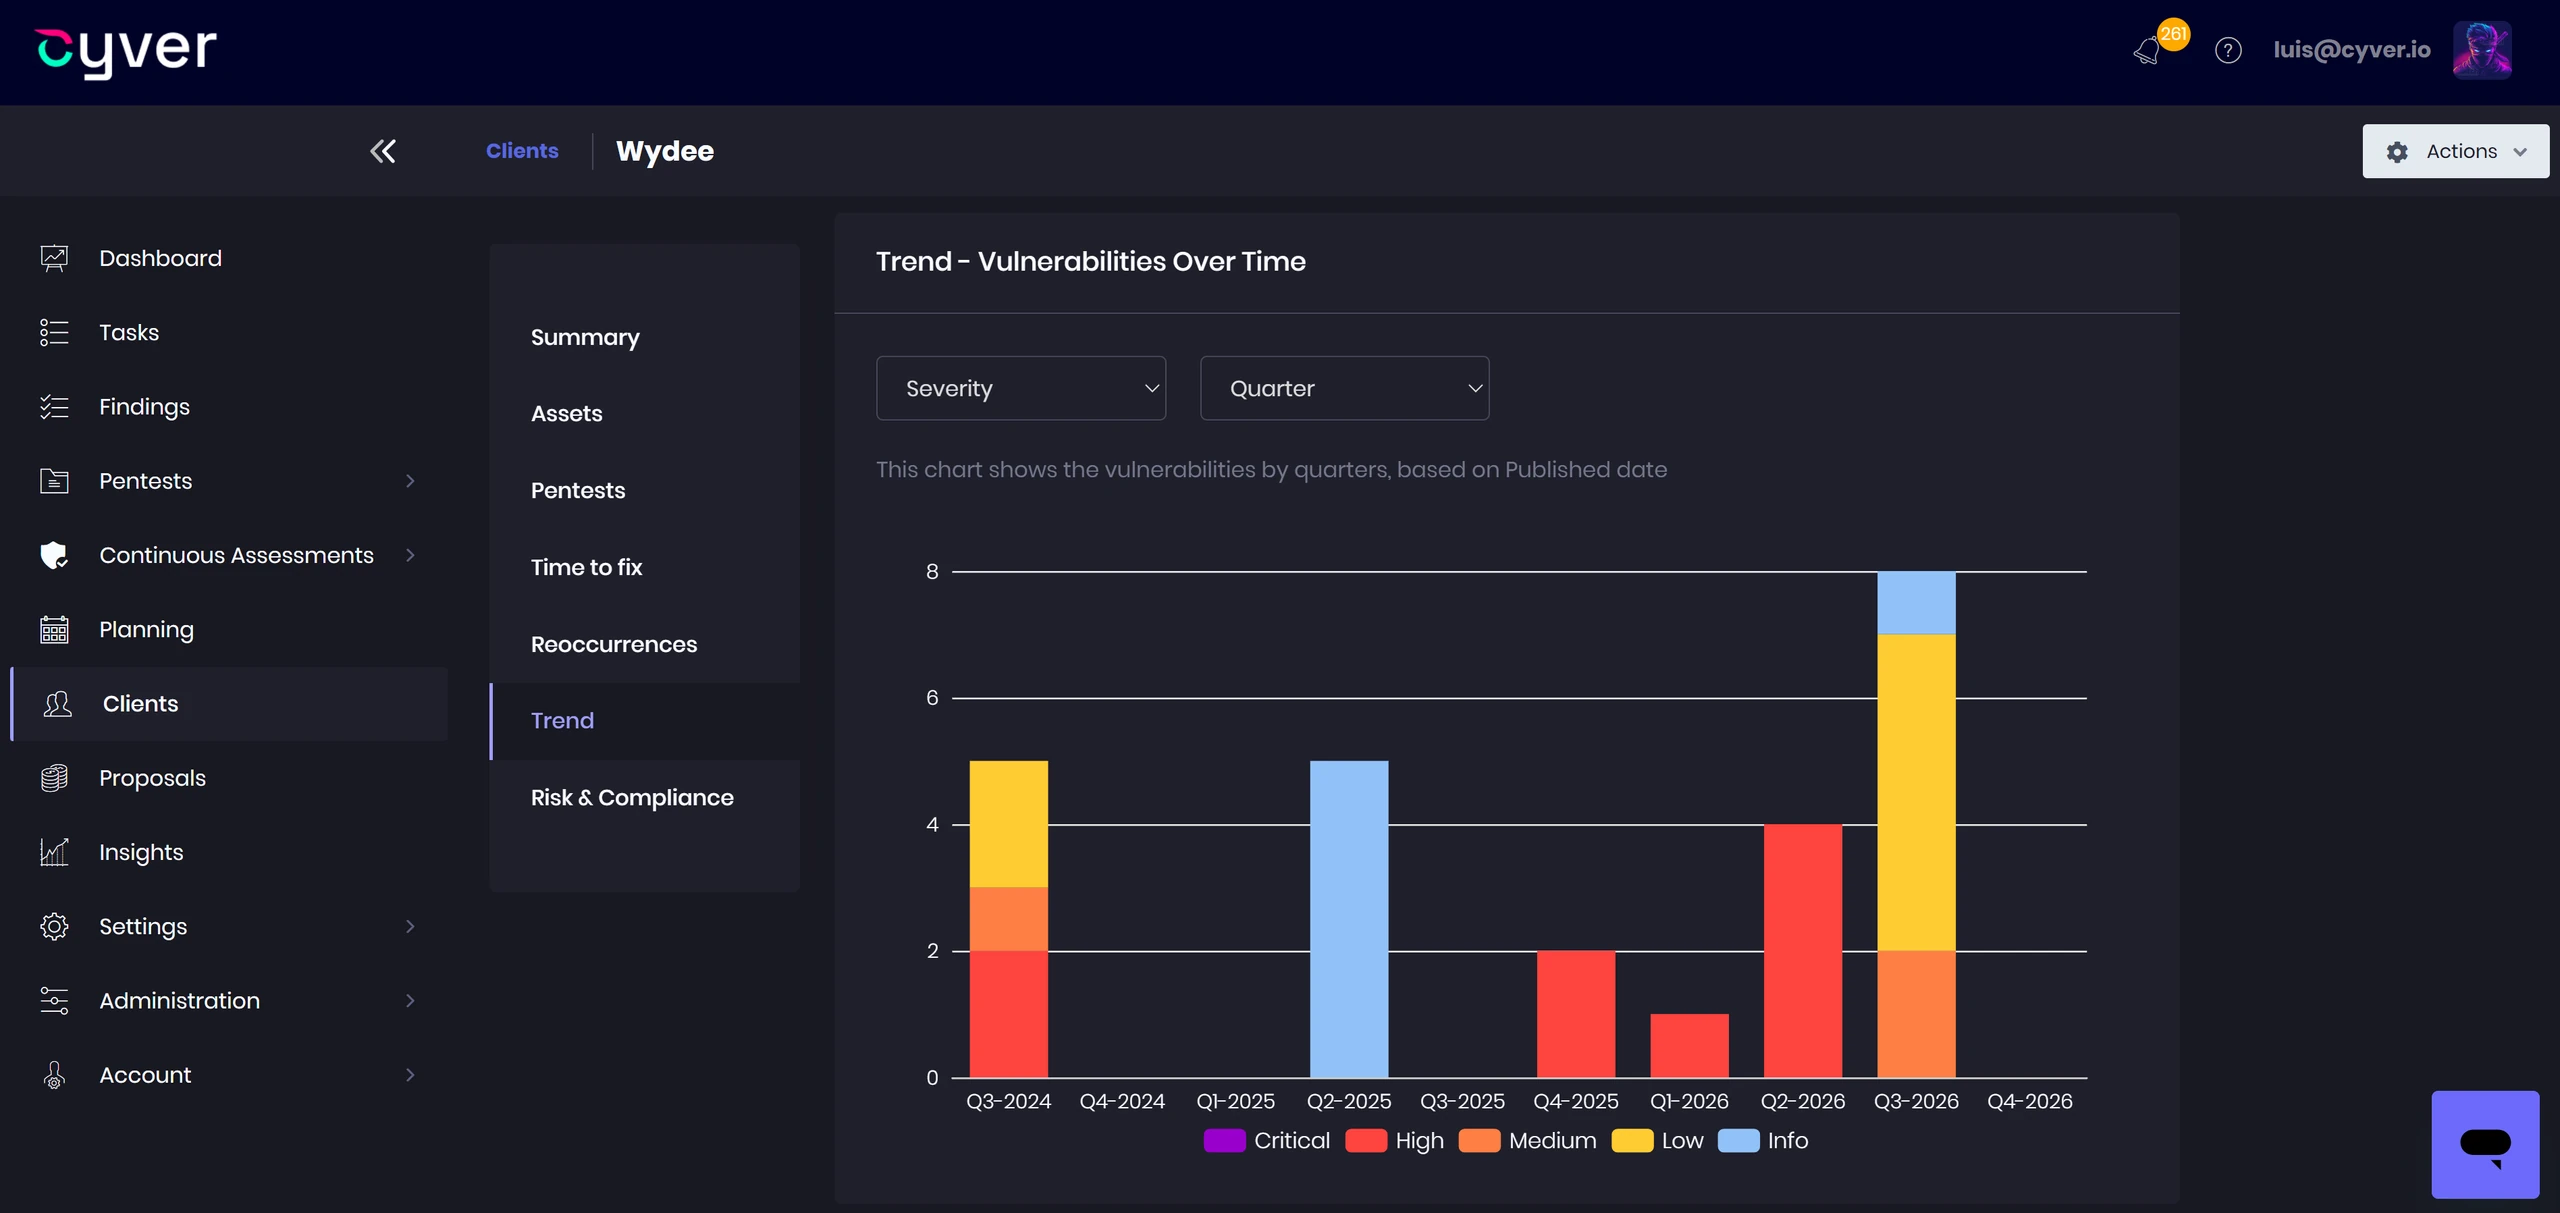
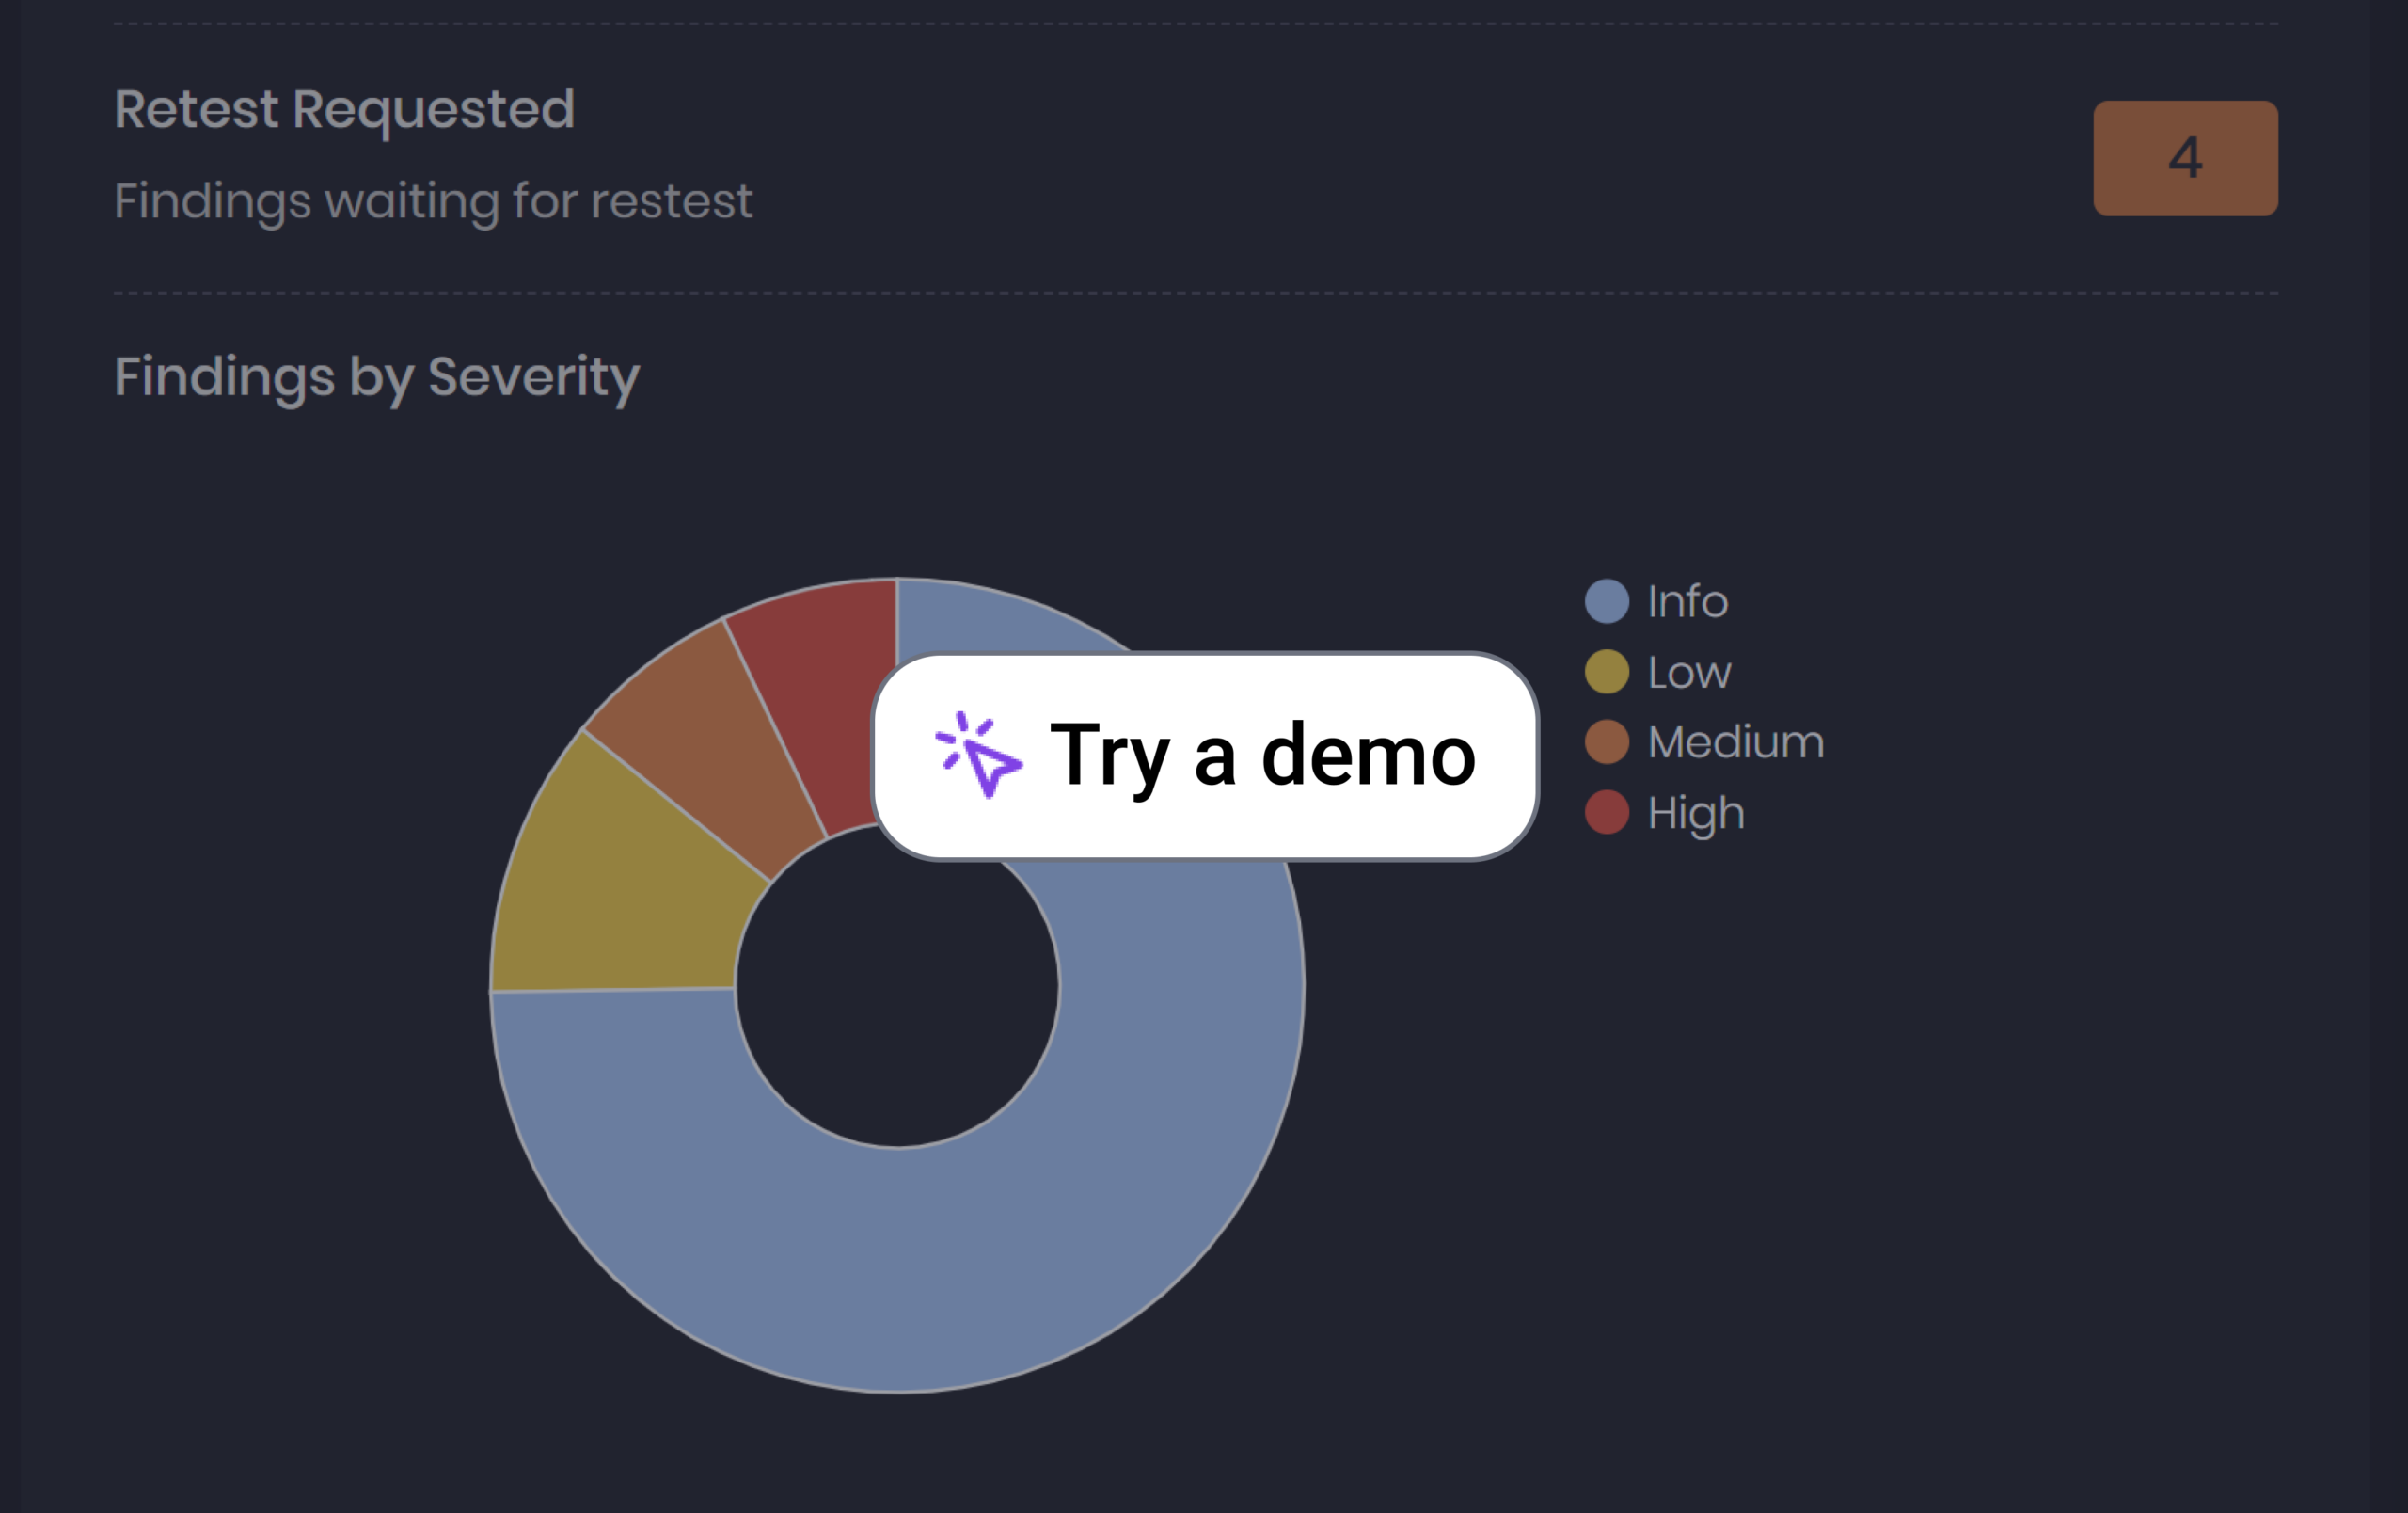
Monitor vulnerabilities by severity, status, asset, and client. Report on outstanding findings and remediation progress across projects.

Ready to dive into the platform?

  • Walk through the plaform, capabilities, and solutions
  • Understand what Cyver Core offers
  • Improve your team’s efficiency.
Cyver Core red teaming: Scenario Management

Scenario Management

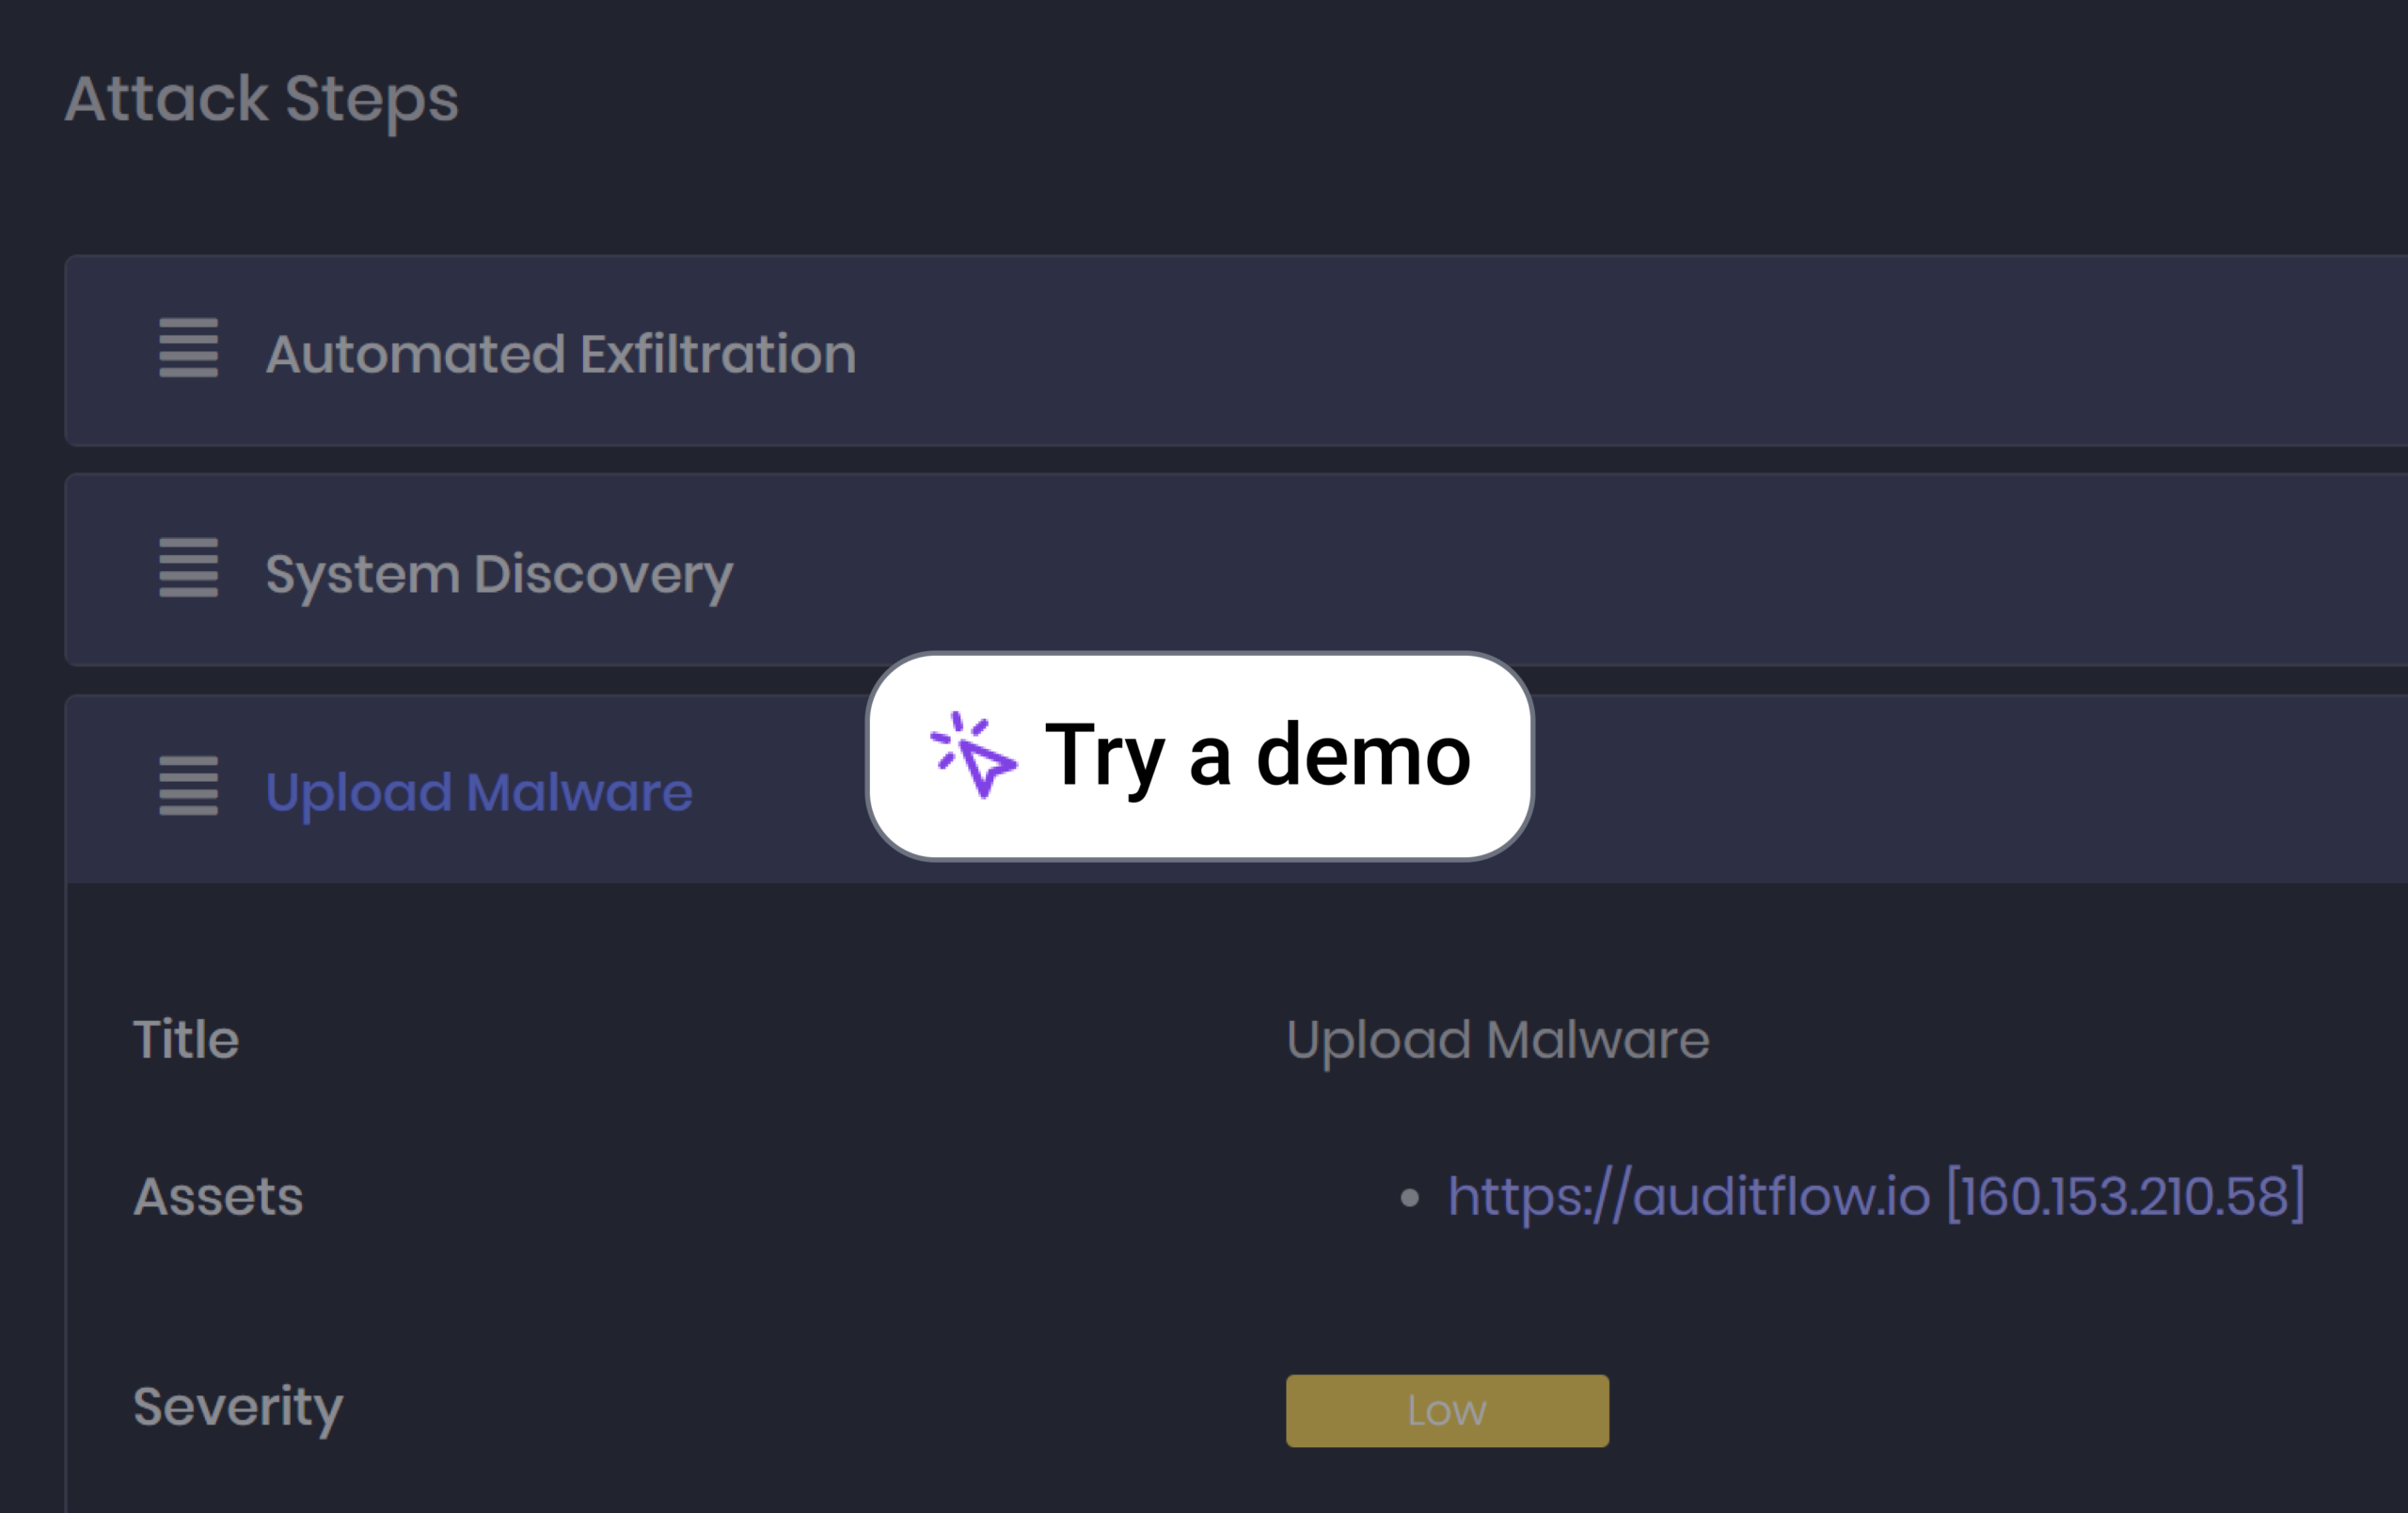
Define engagement scenarios with descriptions and objectives. Organize multiple scenarios within a project and associate each with relevant attack chains.

Cyver Core red teaming: Attack Chain Libraries

Attack Chain Libraries

Create reusable attack chain templates and organize them into libraries. Import predefined chains into projects or build new chains for specific scenarios.

Cyver Core red teaming: MITRE ATT&CK Mapping

MITRE ATT&CK Mapping

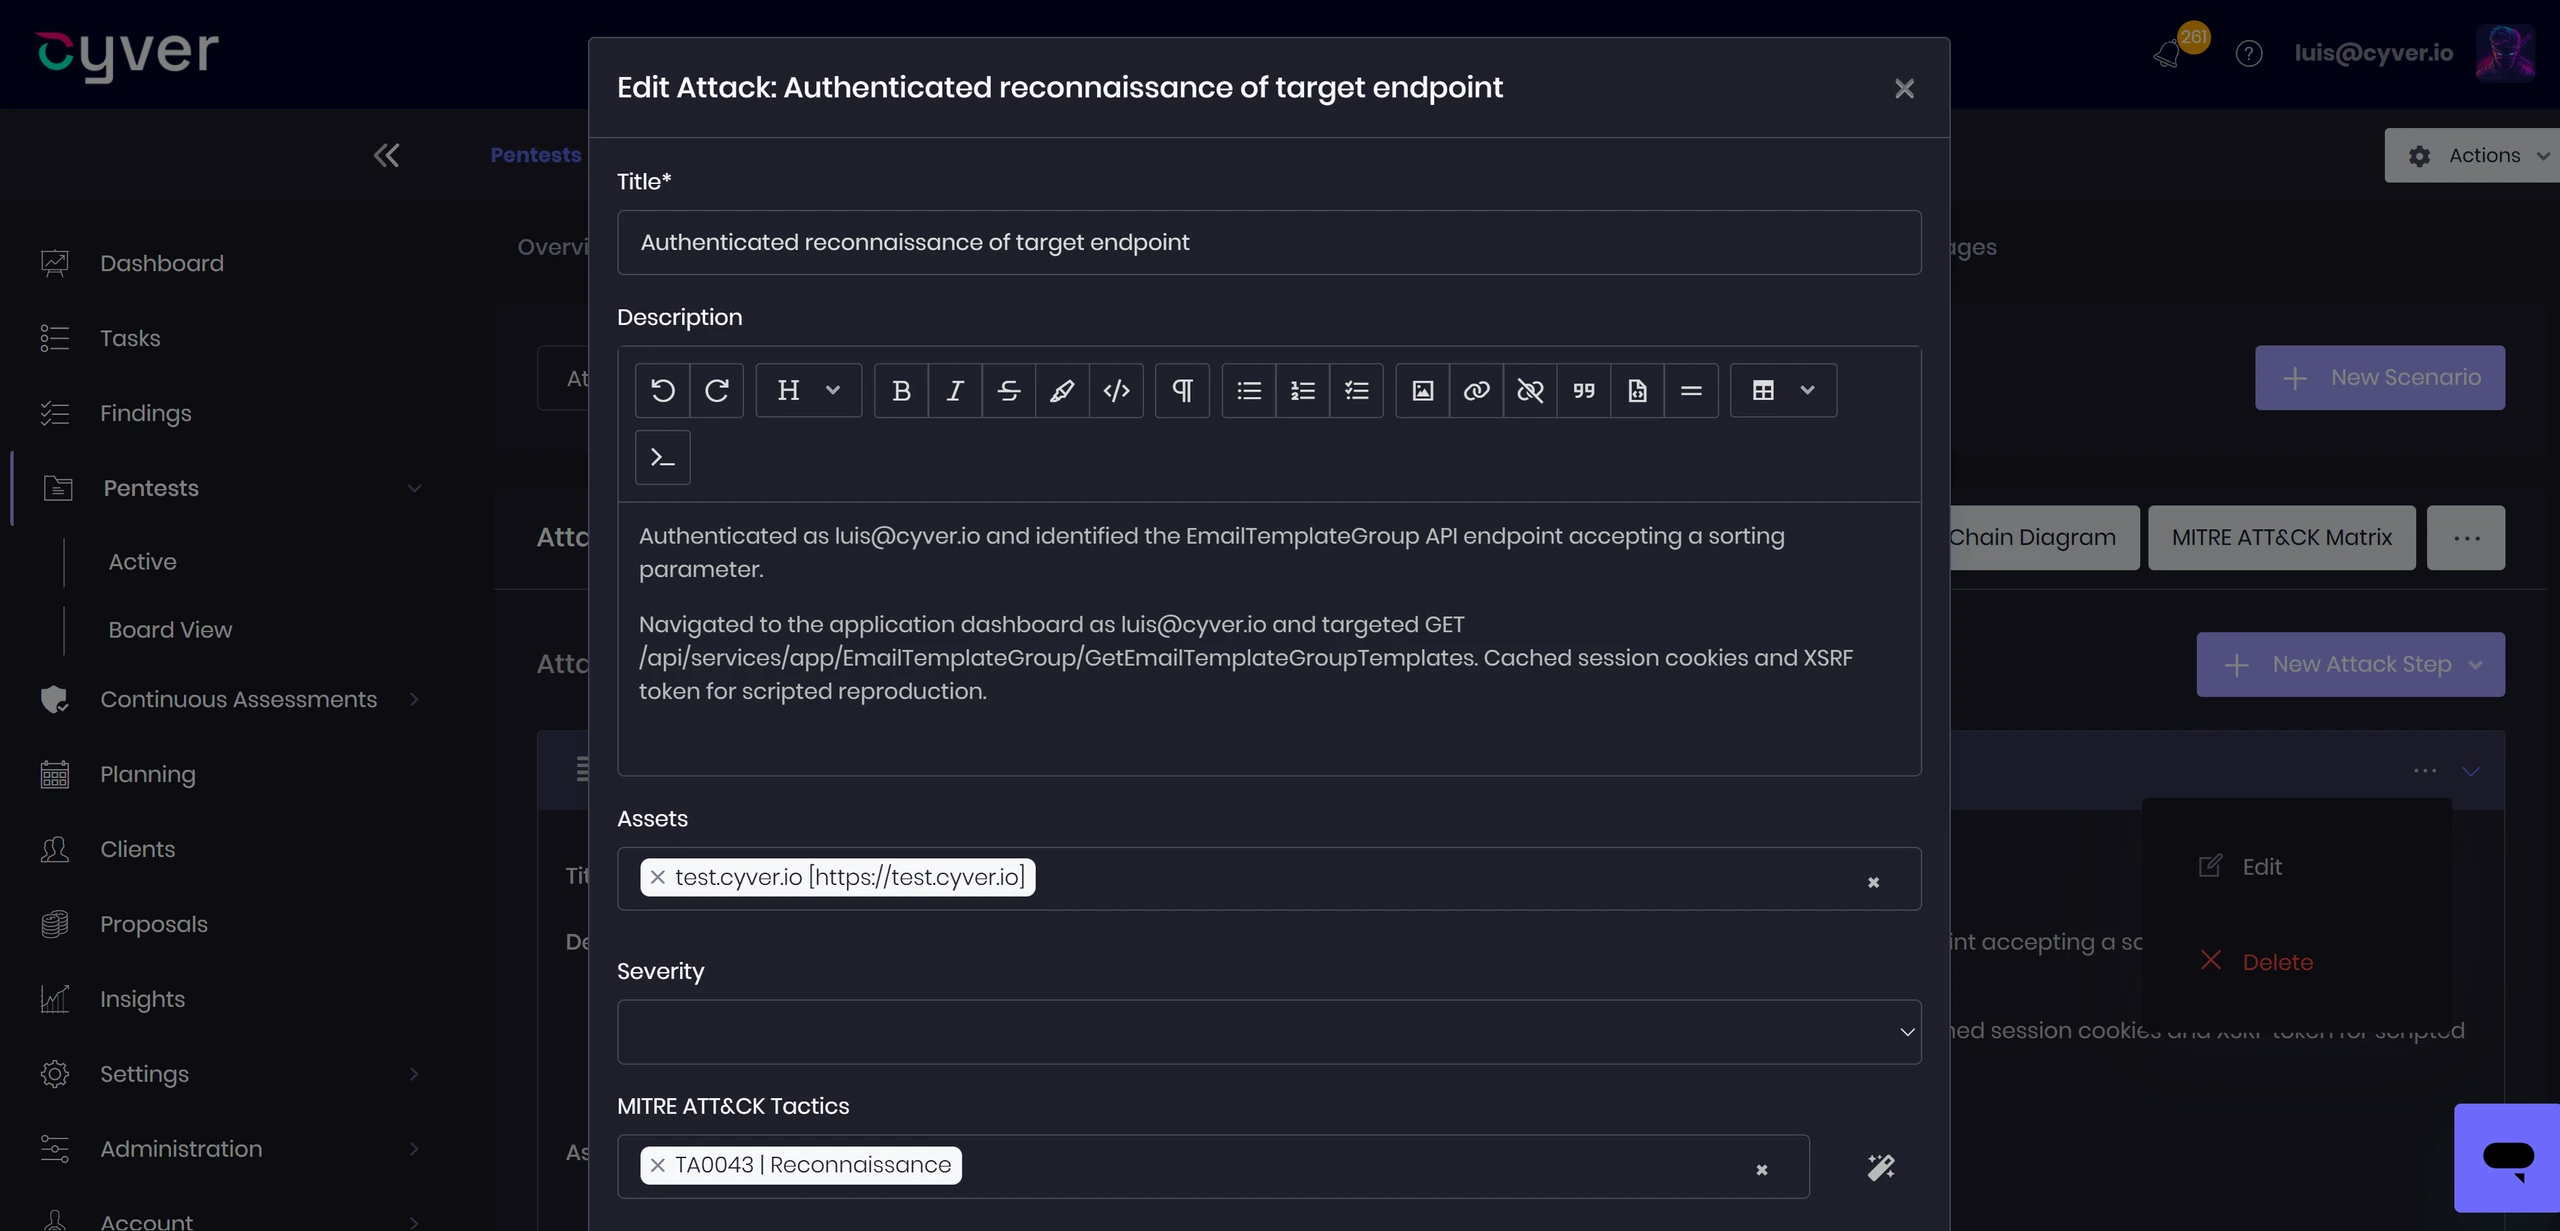
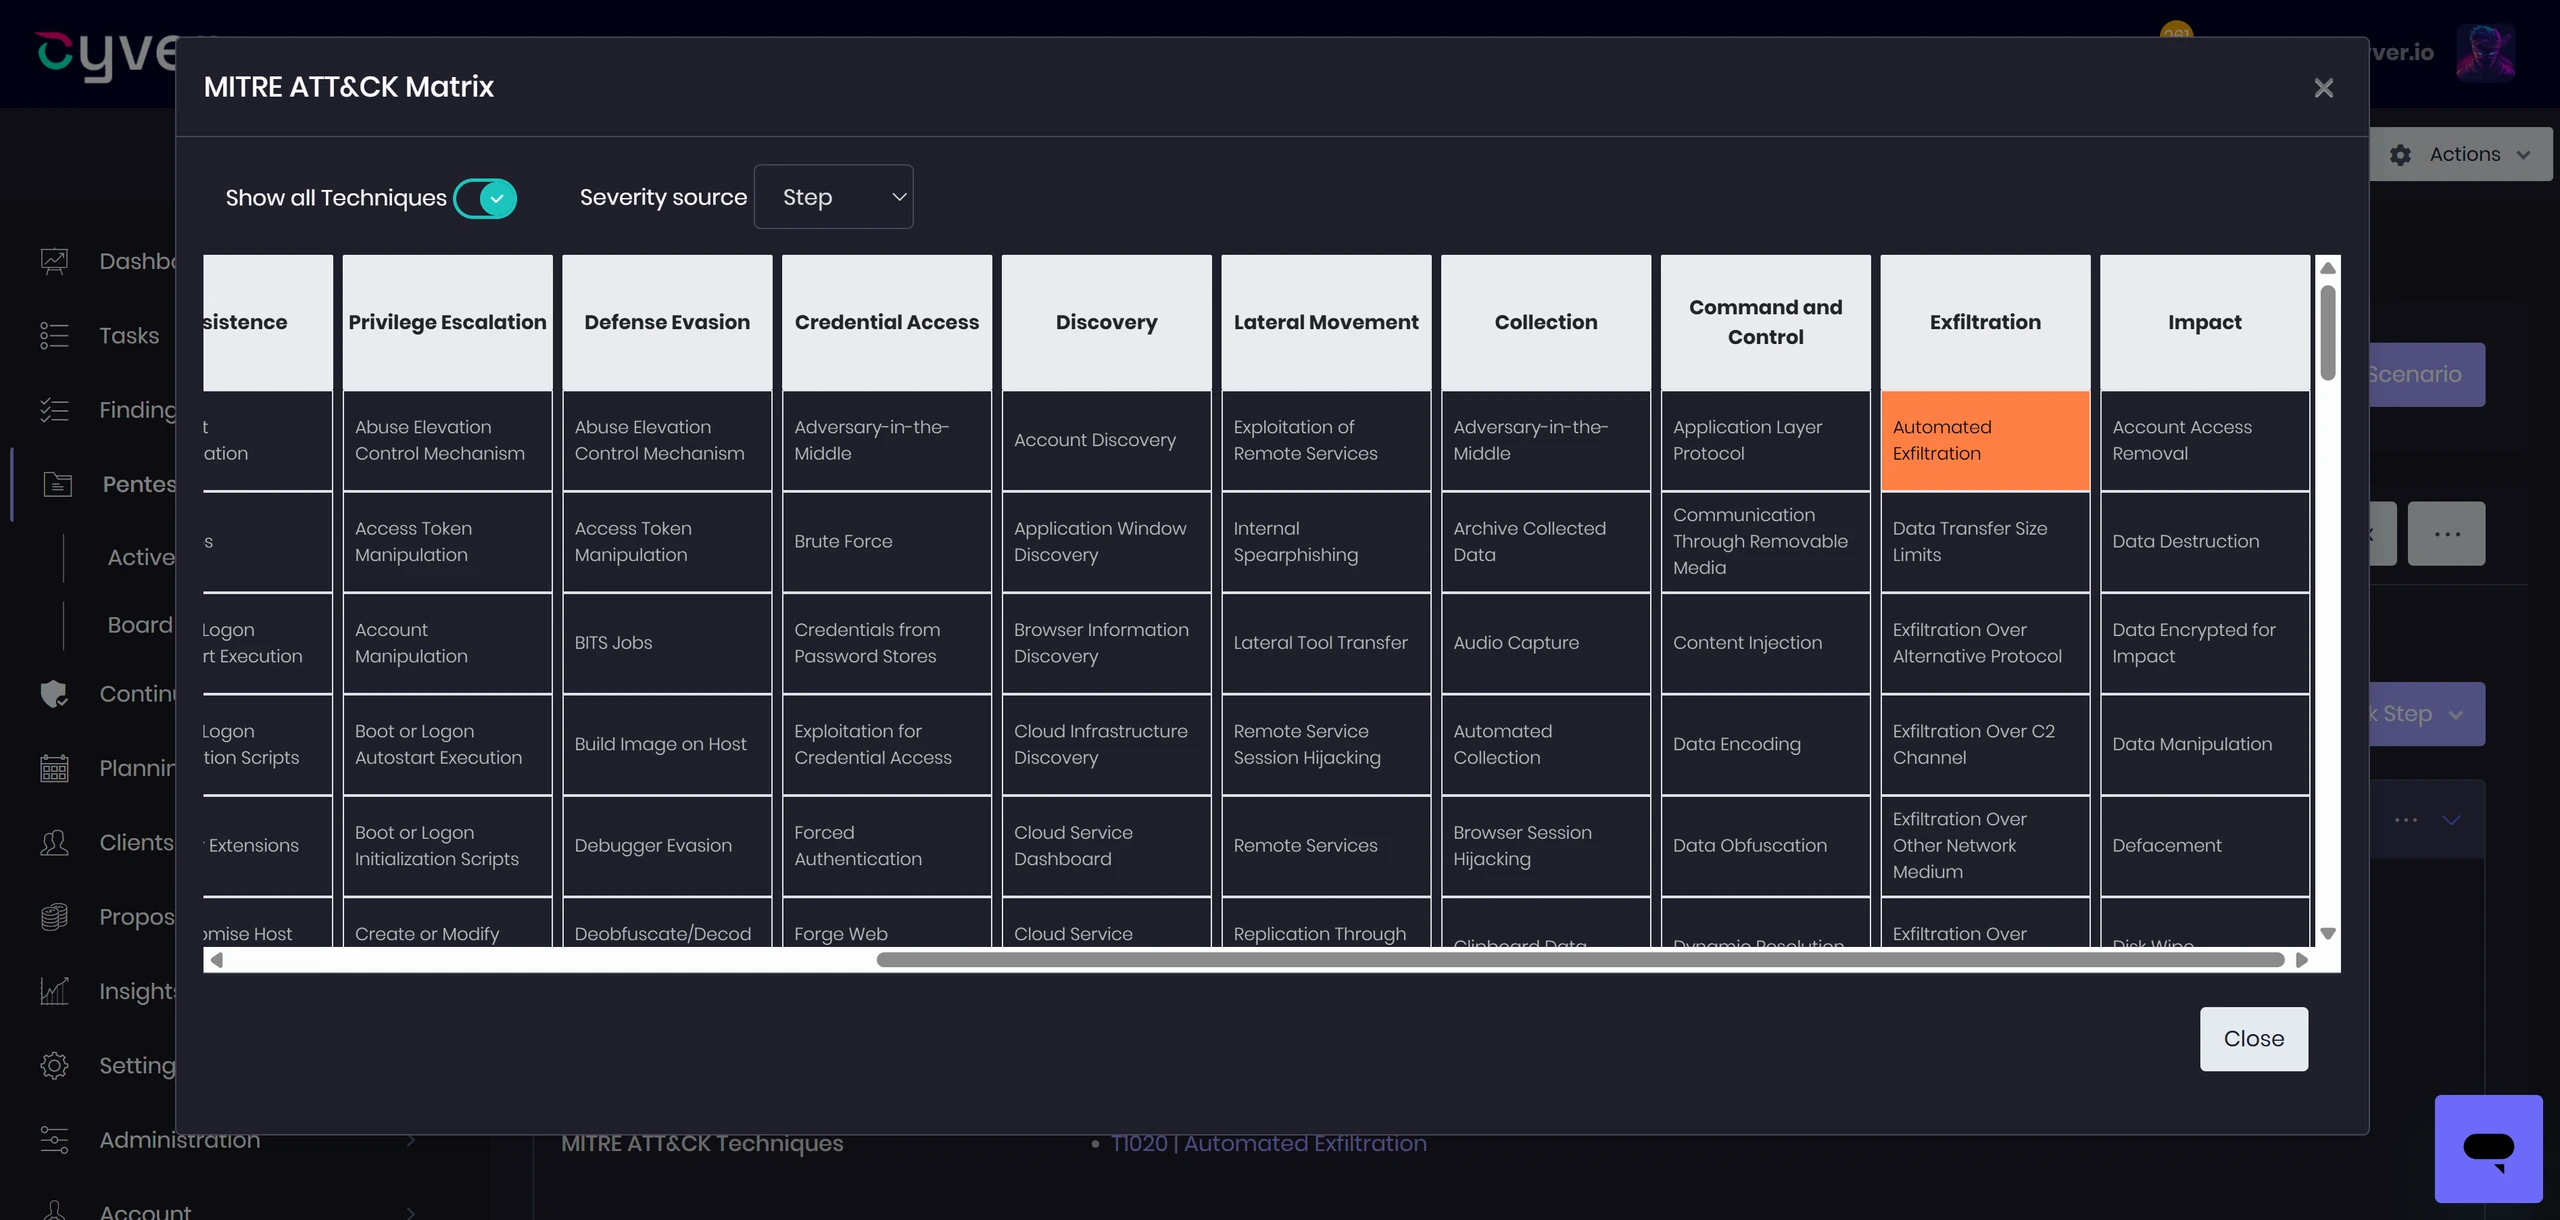
Map attack steps to MITRE ATT&CK tactics and techniques. Select the framework version and use the Navigator view to annotate techniques with colors and notes.

Cyver Core red teaming: Attack Chain Visualization

Attack Chain Visualization

Build attack diagrams to document sequences and relationships between steps. Switch between synchronized Navigator, Diagram, and Steps List views.

Cyver Core red teaming: Attack Step Documentation

Attack Step Documentation

Edit individual steps through a dedicated drawer. Document execution details and observations within the context of each attack chain.

Cyver Core red teaming: Findings and Peer Review

Findings and Peer Review

Document findings with supporting evidence, affected assets, and remediation guidance. Collaborate through comments and peer review before finalizing results.

Cyver Core red teaming: Reporting and Client Delivery

Reporting and Client Delivery

Compile engagement objectives, attack narratives, and findings into branded reports. Share results through the client portal for remediation and follow-up.

Ready to dive into the platform?

  • Walk through the plaform, capabilities, and solutions
  • Understand what Cyver Core offers
  • Improve your team’s efficiency.
Cyver Core PTaaS: Pentest Requests and Scoping

Pentest Requests and Scoping

Collect pentest requests through the client portal. Define target assets, testing requirements, and scope before scheduling each engagement.

Cyver Core PTaaS: Project Planning and Scheduling

Project Planning and Scheduling

Organize pentest projects, assign testers, and manage timelines. Coordinate testing activities across clients, teams, and engagements.

Cyver Core PTaaS: Testing Methodologies and Checklists

Testing Methodologies and Checklists

Structure testing with reusable methodologies and checklists, including OWASP WSTG and ASVS. Track execution and document testing coverage.

Cyver Core PTaaS: Findings and Evidence Management

Findings and Evidence Management

Record findings with supporting evidence, affected assets, CVSS scores, and remediation guidance. Import tool results and reuse finding libraries.

Cyver Core PTaaS: Client Collaboration and Visibility

Client Collaboration and Visibility

Provide clients with portal access to project progress and published findings. Keep questions, comments, and technical discussions within the engagement.

Cyver Core PTaaS: Report Review and Delivery

Report Review and Delivery

Prepare branded reports using reusable templates and the collaborative editor. Complete peer review and deliver reports through the client portal.

Cyver Core PTaaS: Remediation and Retesting

Remediation and Retesting

Track remediation status, manage retest requests, and document validation results. Maintain a history of findings and follow-up testing across engagements.

Ready to dive into the platform?

  • Walk through the plaform, capabilities, and solutions
  • Understand what Cyver Core offers
  • Improve your team’s efficiency.
Cyver Core CTEM: Asset Inventory and Scoping

Asset Inventory and Scoping

Organize assets by client, team, or business context. Define the scope of exposure assessments and associate findings with affected systems.

Cyver Core CTEM: Exposure Data Consolidation

Exposure Data Consolidation

Consolidate findings from pentests, vulnerability scanners, and security tools. Import results into a shared workflow for assessment and follow-up.

Cyver Core CTEM: Risk Assessment and Prioritization

Risk Assessment and Prioritization

Assess findings using CVSS scores, custom scoring, and asset context. Prioritize remediation based on severity and business impact.

Cyver Core CTEM: ASM, DAST and Scanner Integrations

ASM, DAST and Scanner Integrations

Integrate attack surface management (ASM), dynamic application security testing (DAST), and vulnerability scanners such as Tenable, reNgine, and Escape. Consolidate discovered assets and findings to support exposure validation and targeted pentesting.

Cyver Core CTEM: Remediation Coordination

Remediation Coordination

Assign findings to responsible teams, track remediation status, and exchange technical guidance. Maintain discussions and updates alongside each finding.

Cyver Core CTEM: Retesting and Verification

Retesting and Verification

Manage retest requests and verify remediation effectiveness. Record validation evidence and update finding status based on retest results.

Cyver Core CTEM: Exposure Tracking and Reporting

Exposure Tracking and Reporting

Monitor open findings, remediation progress, and assessment results across projects. Share dashboards and reports to support ongoing exposure management.

Ready to dive into the platform?

  • Walk through the plaform, capabilities, and solutions
  • Understand what Cyver Core offers
  • Improve your team’s efficiency.